by hannahadmin | Sep 14, 2026 | Agentic AI, Next-gen Security solutions, Seimless
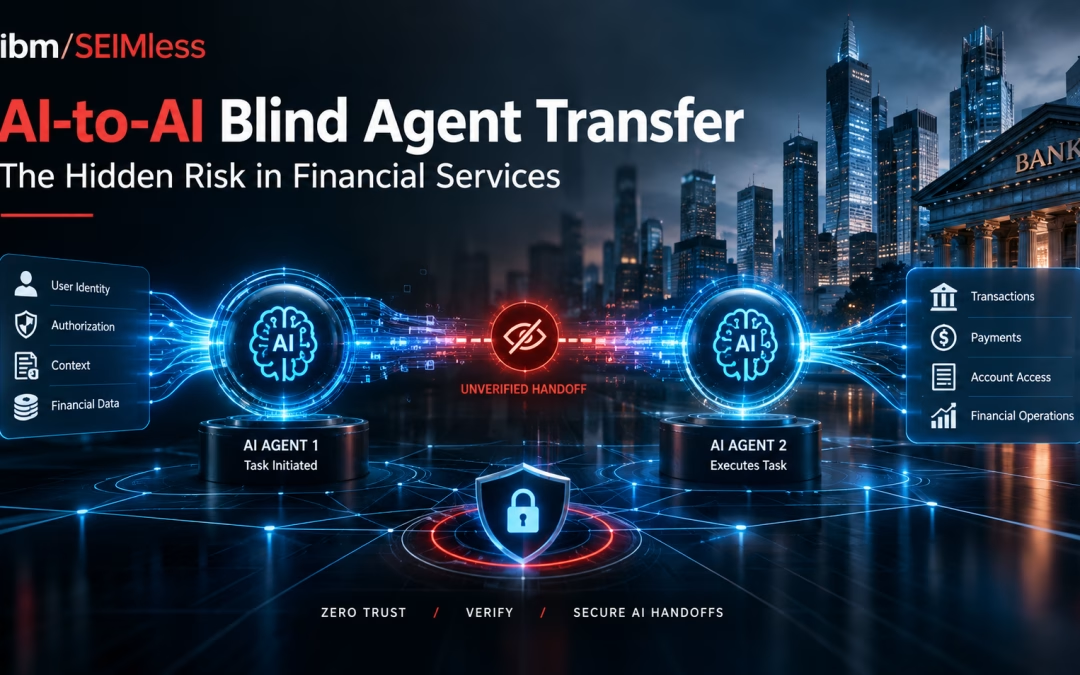
Every bank, insurer, and broker-dealer in America now runs software that hands work to other software without a human in the loop. The failure mode nobody has named yet is blind agent transfer: the moment one AI agent passes a task, a context window, and an inherited set of permissions to a second agent that cannot verify who originally asked, what they were actually authorized to do, or whether the instruction was ever legitimate. A blind agent transfer is not a bug in any single model. It is a gap in the architecture between them — and in financial services, that gap sits directly on top of money movement, customer identity, and regulatory recordkeeping.
The industry spent three years hardening the prompt. It spent almost no time hardening the handoff. That is the wrong order, and the standards bodies have started saying so out loud.
DEFINITION
Blind agent transfer is an automated handoff between two or more AI agents in which the receiving agent acts on inherited instructions, context, and credentials without independently verifying the identity of the original requester, the scope of delegated authority, or the provenance of the context it was given. The result is an action that executes with real-world consequence but no unbroken chain of accountability back to a human principal.
What a Blind Agent Transfer Actually Looks Like Inside a Bank
Abstract risk does not move budgets, so here is the concrete version. A mid-size commercial bank deploys a servicing assistant that handles inbound payment-exception requests. It is read-only by design. When it encounters an exception it cannot resolve, it calls an operations agent that holds write access to the payments queue. That operations agent, in turn, calls a treasury tooling agent through a Model Context Protocol server to check available balance and release the item.
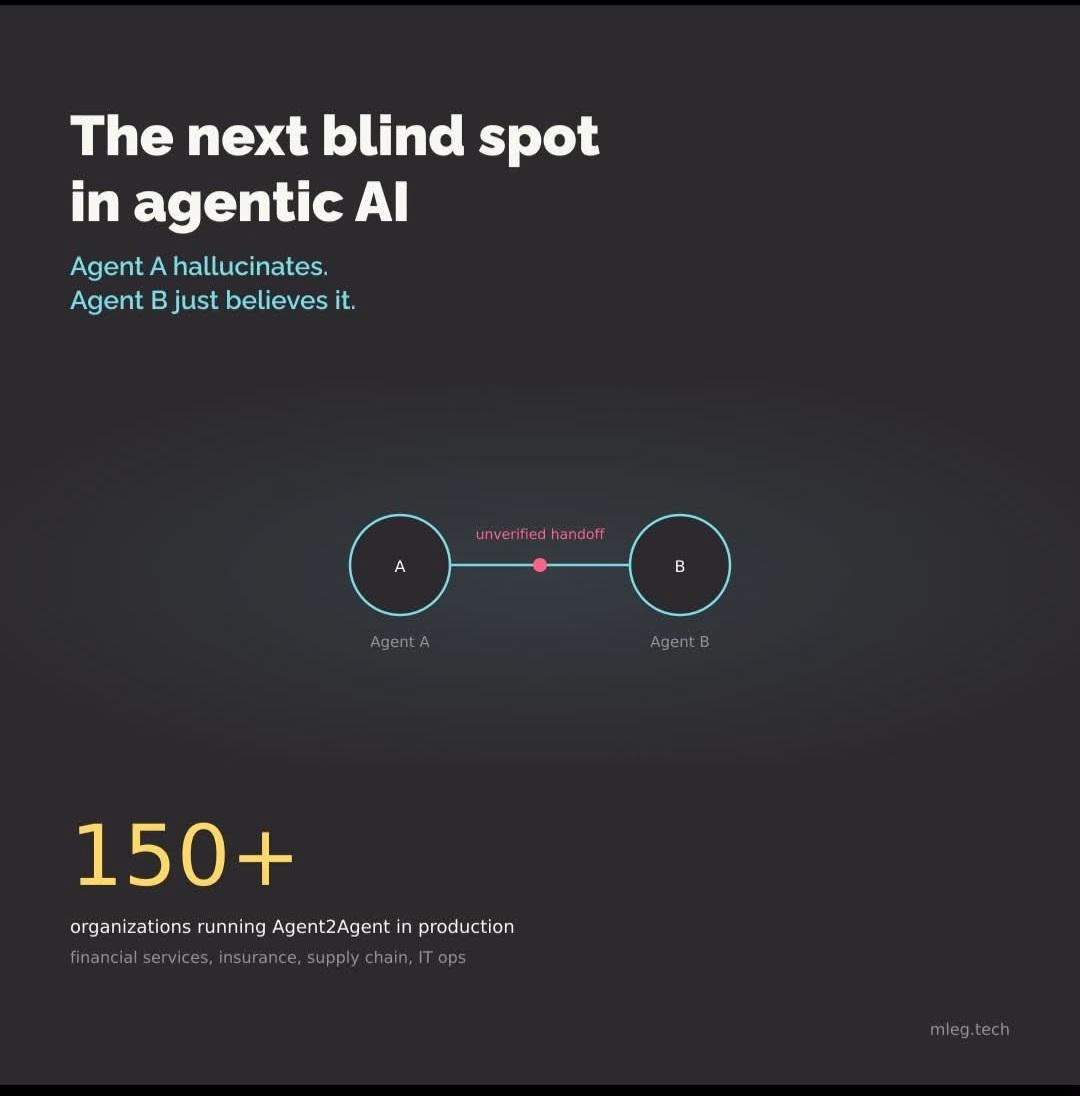
Three agents. Two handoffs. One service account.
The servicing assistant did its job. The operations agent received a well-formed task with a plausible customer reference and a summary of the conversation. It did not receive — because nothing in the architecture required it — a cryptographically verifiable assertion of which authenticated customer started the thread, what entitlements that customer holds, or whether the summarizing agent was itself manipulated. That is a textbook blind agent transfer. If the original inbound message contained an indirect prompt injection buried in an attached remittance advice, the injection does not have to defeat the agent with write access. It only has to survive one summarization step and ride the handoff.
This is the same structural weakness that made third-party compromise the dominant breach vector of the last two years — the pattern we broke down in our analysis of escalating third-party cyber risk after the Ericsson service-provider hack and in our post-mortem of the Change Healthcare breach. Trust that is inherited rather than proven is the vulnerability. Agentic architectures simply industrialize it.
Why Financial Services Is the Worst Possible Place for Blind Agent Transfer
Other sectors can absorb an unattributable automated action. Regulated finance cannot, because four separate obligations all assume a traceable human principal.
Model risk governance. The Federal Reserve issued SR 26-2, Revised Guidance on Model Risk Management, on April 17, 2026, superseding the fifteen-year-old SR 11-7 framework that most institutions still built their inventories around. Multi-agent chains complicate the most basic question those frameworks ask: what is the model, where does it end, and who owns its output? A blind agent transfer makes the boundary unanswerable.
Third-party and vendor risk. Under the Interagency Guidance on Third-Party Relationships (OCC Bulletin 2023-17, also published in the Federal Register), a banking organization remains responsible for activities performed by third parties. When an internal agent silently delegates to a vendor-hosted agent, that delegation is a third-party relationship that no one filed.
Supervisory conduct rules. FINRA reminded members in Regulatory Notice 24-09 that existing supervisory obligations apply in full to generative AI and large language models, and its 2026 Annual Regulatory Oversight Report continues to press on emerging Gen AI trends. FINRA’s broader artificial intelligence topic page is the current reference point for member firms.
Cybersecurity program requirements. New York’s Department of Financial Services published an industry letter on cybersecurity risks arising from artificial intelligence that explicitly ties AI risk back to the access-control and third-party provisions of Part 500. Meanwhile, the SEC’s cybersecurity disclosure rules put a four-business-day clock on material incidents — a clock that starts whether or not your logs can explain which agent did what.
Layer on Treasury’s report on AI in financial services, FinCEN’s alert on deepfake and generative-AI fraud schemes (FIN-2024-Alert004), and the examination expectations codified across the FFIEC IT Examination Handbook, and the compliance picture is unambiguous. Autonomy without attribution is a finding waiting to be written.
The Four Failure Modes of Blind Agent Transfer
1. Identity collapse
Most production agent stacks authenticate the platform, not the principal. Every downstream call arrives wearing the same service identity, so the receiving agent sees a trusted caller and nothing more. NIST opened a formal workstream on precisely this problem with its February 5, 2026 concept paper, Accelerating the Adoption of Software and Artificial Intelligence Agent Identity and Authorization. The paper’s framing is telling: the risk comes from giving agents access to diverse data, tools, and applications without adequate identification and authorization safeguards.
2. Authority inflation
This is the classic confused-deputy problem wearing new clothes. A low-privilege agent induces a high-privilege agent to act on its behalf, and the privileged agent obliges because the request is well-formed. Nothing is technically broken. The permissions worked exactly as written. They were simply written for a world with one actor per token. Token-exchange standards such as IETF RFC 8693 and the OAuth security best practices in RFC 9700 exist to carry delegation semantics properly — and are routinely skipped in agent deployments.
3. Context laundering
Every summarization step strips provenance. Text that entered the system as untrusted customer input leaves the first agent as an authoritative-sounding internal task description. By the third hop, no marker distinguishes attacker-supplied content from verified record data. The OWASP Top 10 for Agentic Applications (2026), released December 9, 2025, catalogs this family of risks, as does MITRE ATLAS and NIST’s adversarial machine learning taxonomy, NIST AI 100-2 E2025.
4. The audit gap
Ask most institutions to reconstruct a four-agent decision chain from ninety days ago and you will get application logs, not an evidentiary record. There is no signed assertion at each hop, no immutable ordering, and frequently no retention of the intermediate context at all. That is the difference between telemetry and an audit trail, and examiners know it.
What the Standards Bodies Are Now Saying About Agent Handoffs
The single most useful document published on this topic came from an unexpected source. On May 20, 2026, the National Security Agency’s Artificial Intelligence Security Center released Model Context Protocol: Security Design Considerations for AI-Driven Automation. Its language maps almost word-for-word onto blind agent transfer: agentic systems introduce “novel and systemic risks like dynamic tool invocation, implicit trust relationships, and context sharing,” and “misaligned assumptions or subtle inconsistencies at any stage can propagate and compound into exploitable conditions.” NSA’s conclusion is that the agentic environment must be treated as a continuum rather than a set of independently patchable endpoints.
NIST is building the control layer underneath that conclusion. The Control Overlays for Securing AI Systems (COSAiS) project, announced in the CSRC’s control overlays initiative, is producing five overlays on top of SP 800-53 Rev. 5 — and two of the five are specifically for AI agent systems, split between single-agent and multi-agent use cases. The existence of a dedicated multi-agent overlay is the clearest institutional signal available that agent-to-agent trust is now treated as its own control domain.
Alongside it sit the tools most institutions already have on the shelf: the NIST AI Risk Management Framework, SP 800-207 Zero Trust Architecture, the identity assurance model in SP 800-63-4, reference builds from the National Cybersecurity Center of Excellence, CISA’s artificial intelligence program and joint guidance on deploying AI systems securely, the CISA Zero Trust Maturity Model, Secure by Design commitments, and the KEV catalog for the underlying infrastructure those agents run on. GAO’s AI oversight work and the CFPB’s research on chatbots in consumer finance round out the U.S. policy picture.
Blind Agent Transfer Is a Network Problem Before It Is a Model Problem
Here is the uncomfortable conclusion most AI security vendors avoid: you cannot fix blind agent transfer inside the model layer. Guardrails, evaluations, and system prompts all operate on content. The failure is about identity, authority, and provenance in transit — which is network and cryptographic territory.
That is precisely where ibm/SEIMless built Exodus Quantum Resistant Networking. When agent-to-agent traffic crosses a segmented, cryptographically authenticated fabric rather than a flat internal network, the handoff becomes something you can actually govern:
For institutions still running exception workflows over legacy transport, our comparisons of MPLS security assumptions, SD-WAN architecture, and why today’s software-defined networks are not future-ready are the right starting point. Our Nxt-Gen Network Security Solutions overview maps the full control set.
A Seven-Control Blueprint to Eliminate Blind Agent Transfer
| Control |
What it stops |
| 1. Per-agent cryptographic identity — no shared service accounts across hops |
Identity collapse |
| 2. Signed delegation chains — carry the original principal and scope through every transfer using proper token exchange |
Authority inflation |
| 3. Provenance tagging — mark untrusted input at ingest and preserve the tag through summarization |
Context laundering |
| 4. Privilege ceilings — a receiving agent may never exceed the effective entitlements of the originating human |
Confused deputy escalation |
| 5. Human checkpoints on money movement — irreversible actions require re-authentication, not inherited authority |
Unattributable transactions |
| 6. Immutable handoff logging — signed, ordered, retained records of every transfer |
The audit gap |
| 7. Network segmentation between agent tiers — reachability follows policy, not topology |
Lateral agent abuse |
Control five is the one institutions argue about, because it trades away some of the automation ROI. It is also the one that will look obvious in hindsight. No examiner has ever accepted “the agent decided” as a control narrative.
The Quantum Overlay Nobody Is Modeling Yet
There is a second-order consequence of blind agent transfer that almost no risk register has caught. Multi-agent systems generate an enormous volume of intermediate context — customer PII, account detail, internal reasoning about credit and fraud decisions — and that context traverses the network and lands in storage. Under a harvest-now, decrypt-later posture, an adversary does not need to break the agent chain today. They only need to capture it.
NIST has already set the deprecation schedule for classical public-key cryptography in NIST IR 8547, and vulnerabilities in the surrounding stack keep arriving through the National Vulnerability Database. We covered the economics of that exposure in harvest now, decrypt later, the sequencing in our post-quantum cryptography migration playbook, and the collision of both timelines in agentic AI security meets Q-Day. Agent chatter is the richest harvest target most institutions have ever created, and it is usually the least protected.
Questions Your Board Will Ask Before the Next Audit Cycle
- How many agent-to-agent handoffs occur in production today, and which of them touch money movement or customer identity?
- For any given automated action last quarter, can we produce a signed chain back to an authenticated human principal?
- Which agents can invoke third-party or vendor-hosted agents, and are those relationships in our third-party inventory?
- What is our maximum blast radius if the highest-privilege agent acts on a laundered instruction?
- Are agent transcripts and intermediate context encrypted with quantum-resistant protection in motion and at rest?
If the answer to the second question is “not reliably,” blind agent transfer is already in the environment. It simply has not been named in a finding yet. Related reading: what zero trust actually means, our shadow AI enterprise playbook, the rise of AI agents, AI’s arrival on Wall Street, AI governance under pressure, AI-native networks, and why quantum-resistant networking is now a business necessity.
Blind Agent Transfer: Frequently Asked Questions
What is blind agent transfer in simple terms?
Blind agent transfer is when one AI agent hands a task to another AI agent along with inherited context and permissions, and the receiving agent acts without verifying who originally made the request or whether that person was authorized. The action executes, but the accountability chain back to a human is broken.
How is blind agent transfer different from prompt injection?
Prompt injection is the attack; blind agent transfer is the condition that lets the attack travel. An injection only has to compromise the first, least-privileged agent. If handoffs carry no verified identity or provenance, the malicious instruction is laundered into a trusted-looking internal task and delivered to an agent that can actually act.
Why is this specifically dangerous in banking and insurance?
Because model risk, third-party risk, supervisory, and incident-disclosure obligations all assume a traceable principal behind every action. Guidance including Federal Reserve SR 26-2, OCC Bulletin 2023-17, FINRA Regulatory Notice 24-09, and the NYDFS AI industry letter presumes you can answer who authorized what. A blind agent transfer makes that unanswerable.
Can guardrails or AI firewalls prevent blind agent transfer?
Only partially. Content filters inspect what agents say. Blind agent transfer is a failure of identity, delegated authority, and provenance in transit, which lives in the network and cryptographic layer. Per-workload identity, signed delegation, segmentation, and immutable handoff logging are the controls that close it.
Does the Model Context Protocol make this worse?
MCP makes tool invocation dramatically easier, which expands the number of handoffs without necessarily improving verification. NSA’s May 2026 security design considerations for MCP flag dynamic tool invocation, implicit trust relationships, and context sharing as systemic risks, and advise treating the agentic environment as a continuum rather than isolated endpoints.
Where should a financial institution start?
Inventory every agent-to-agent handoff that touches money movement or customer identity, then apply per-agent cryptographic identity, signed delegation, privilege ceilings, and human re-authentication on irreversible actions. ibm/SEIMless can assess the network layer beneath those agents and deploy quantum-resistant segmentation through Exodus QRN.
Blind agent transfer is solvable — but not at the model layer. ibm/SEIMless Communications Technologies, Inc., home of Exodus QRN, Inc., has spent more than 20 years securing the networks that regulated institutions run on, and we build quantum-resistant infrastructure for the agentic era. Let our team assess where your agent chains cross unprotected ground.
Contact Us | Our Blog | Our Services | See Previous Post…
by hannahadmin | Aug 28, 2026 | blog, cybersecurity, Enterprise technology, Next-gen Security solutions, Seimless
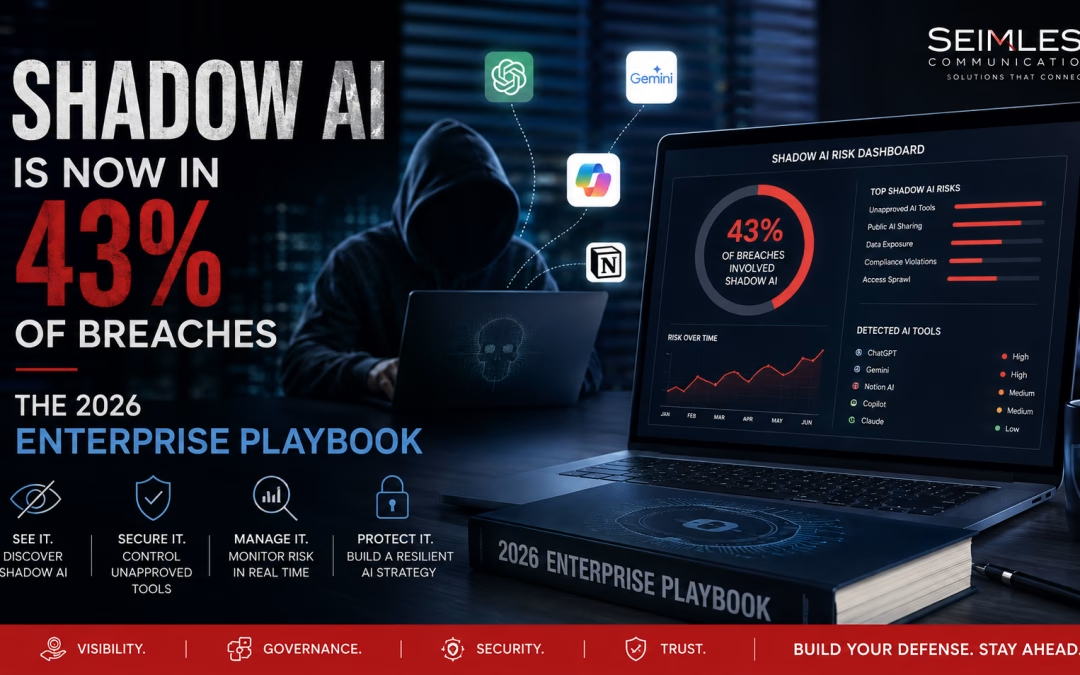
Shadow AI has become the fastest-growing security gap in the enterprise, and the 2026 numbers finally make the scale of it undeniable. IBM’s latest breach research puts unsanctioned AI tools inside 43% of security incidents. That figure more than doubled in a single year. Meanwhile, most organizations still have no process for approving, tracking, or revoking the AI tools their own employees use every day.
This is not a story about reckless staff. It is a story about a control gap. People adopt AI because it makes their work faster, and they reach for whatever tool is nearest when the sanctioned option does not exist. At ibm/SEIMless, we have watched the same pattern play out with cloud storage, then with messaging apps, and now with AI. The lesson repeats: you cannot secure what you have not inventoried.
This guide covers what shadow AI is, what the current data actually says, how it leaks information, what regulators now expect, and a practical program you can start this quarter.
What Shadow AI Actually Is, and What It Is Not
Shadow AI describes any artificial intelligence tool, model, agent, or AI-enabled feature that touches company data without security review, procurement approval, or governance oversight.
The definition sounds narrow. In practice it is very wide, because AI now arrives through four separate doors, and only one of them looks like a purchase.
The Four Faces of Shadow AI
Consumer chatbots on personal accounts. An analyst pastes a customer list into a free chatbot to reformat it. No contract governs that data. No log records the transfer.
AI features quietly added to approved software. Your sanctioned CRM ships an AI summarizer in a routine update. Nobody reviewed it, yet it now reads every record. This is the category most teams miss entirely.
Employee-built automations and agents. A finance lead wires an AI agent to a spreadsheet and an email inbox. The agent holds credentials, and no one has scoped them.
Browser extensions and plugins. Free extensions read page content by design. On an internal application, that means they read your data.
Notice what unites all four. None involves malice, and none triggers a purchase order. Consequently, none reaches the security team through the usual channels. Our post on how LLMs will improve network security explains the upside of AI in the enterprise; shadow AI is simply that same technology arriving without the guardrails.
The 2026 Numbers: Shadow AI Moved From Edge Case to Norm
The evidence base changed sharply this year. Three major studies now measure shadow AI directly rather than treating it as an anecdote.
IBM’s Cost of a Data Breach Report 2026, published on 29 July 2026, studied 602 breached organizations across 17 industries and 16 countries. It found shadow AI involved in 43% of incidents, up from roughly one in five the previous year. Furthermore, more than two-thirds of those organizations had no governance process to limit unauthorized AI deployment.
The same report puts the global average breach cost at $4.99 million, a 12% jump and an all-time high. AI-driven attacks rose 56%, led by deepfake impersonation and AI-enabled malware.
Netskope’s AI Report 2026 adds the usage picture. Only 56% of workplace AI users stay entirely inside organization-managed applications. Another 14% mix managed and personal tools, while 30% use personal accounts exclusively. In other words, nearly half of AI activity sits partly or wholly outside company control.
Verizon’s 2026 Data Breach Investigations Report rounds out the threat side. It reports that 15% of attack techniques are now bolstered by generative AI, and that 31% of breaches begin with software vulnerabilities, which have overtaken stolen credentials as the leading entry point.
What Shadow AI Costs When It Goes Wrong
Cost data from IBM’s earlier baseline research is the clearest picture available of shadow AI’s financial tail.
Breaches linked to shadow AI added as much as $670,000 to the average incident cost. Nearly two-thirds of those breaches exposed customer personally identifiable information. Intellectual property proved the most expensive category, at $178 per record.
One statistic stands out above the rest. Among organizations that suffered an AI-related breach, 97% lacked proper AI access controls. That is not a technology failure. That is an identity and permissions failure, and it is fixable.
Why the Governance Gap Persists
Ask any CISO why the gap exists and you get the same three answers.
First, procurement never sees the tool, because free tiers require no purchase. Second, network monitoring often misses it, since traffic to a major AI provider looks identical to ordinary web browsing. Third, and most importantly, the sanctioned alternative is either slower, worse, or missing altogether.
That third reason matters most. Employees do not route around controls for fun. They route around controls that cost them time.
Shadow AI Is Not Just Shadow IT With a New Name
Security teams reach for the shadow IT playbook first, and that instinct is only half right. The discovery methods transfer well. The remediation methods do not.
Shadow IT moved data to an unapproved location. You could usually find the file, delete it, and close the ticket. Shadow AI behaves differently in three ways that matter.
The data may not come back. A prompt sent to a consumer service can be retained, reviewed by humans, or used to improve a model. Deleting your local copy changes nothing about the copy that already left.
The exposure compounds over time. Model memorization means a snippet submitted today can surface in an output months later. Traditional shadow IT exposure was static, whereas this exposure has a long tail.
The tool acts on your behalf. An unapproved file-sharing service stored things. An unapproved AI agent authenticates, queries, writes, and sends. Therefore the blast radius is defined by permissions rather than by storage.
There is a fourth difference that is easy to miss. Shadow IT was mostly invisible to the vendor whose product it displaced, while shadow AI often arrives *from* the vendors you already trust. When a licensed application adds an AI assistant in a routine release, the shadow appears inside your approved estate. Our post on the five major impacts of machine learning models on data security covers that dynamic in more depth.
How Shadow AI Actually Leaks Enterprise Data
Understanding the mechanics helps you choose the right control. Shadow AI leaks data through five distinct channels, and each one needs a different answer.
Prompt-Side Leakage
This is the obvious one. A user pastes source code, a contract, a patient record, or a credential into a prompt. The data leaves your perimeter instantly.
Volume tells the story here. Netskope’s Cloud and Threat Report 2026 found that data sent to SaaS generative AI apps grew sixfold in a year, from roughly 3,000 to 18,000 prompts per month in the median organization. Around 3% of AI users generate an average of 223 data policy violations each month.
The Personal Account Problem
Enterprise AI agreements typically promise that your prompts will not train the vendor’s models. Consumer accounts frequently promise the opposite, or say nothing at all.
Encouragingly, the trend is improving. Infosecurity Magazine reported that personal-account usage among workplace AI users fell from 78% to 47% across a single year. Nevertheless, 47% is still nearly half your workforce operating outside contractual protection.
Agentic AI and MCP Widen the Channel
Chatbots read what you paste. Agents read what they can reach, which is a much larger set.
Netskope recorded downstream data policy violations doubling from 12 to 31 per week in the median organization, with top-quartile organizations climbing from 72 to 206. The report attributes that growth to agentic AI and to a fourfold increase in Model Context Protocol traffic. We covered the security implications of autonomous agents in our analysis of the agentic AI vulnerability exposed in ServiceNow and the malicious npm package that stole files from an AI user directory.
Model Inversion and Memorization
The subtlest channel runs in reverse. Attackers query a model to reconstruct the data it was trained or fine-tuned on.
NIST’s Generative AI Profile, AI 600-1, names data memorization explicitly, warning that models can leak, generate, or infer sensitive information about individuals. IBM prices the average model inversion breach at $6 million — higher than a conventional breach, because the exposed asset is usually the training corpus itself.
Third-Party and Supply Chain Exposure
The fifth channel is not yours at all. Your vendors, contractors, and managed providers use AI too, and their shadow AI becomes your exposure the moment they touch your data.
Consider a design partner summarizing your specifications in a consumer chatbot, or an outsourced support team pasting customer tickets into a free translator. No control you deploy internally will catch either one. Only contract language and vendor assessment will.
Third-party risk already dominates breach reporting, and AI widens it. Our coverage of the Ericsson service provider breach and the GlassWorm supply chain takedown shows how quickly a partner’s weakness becomes your incident. Add AI clauses to your standard agreements now, before renewal cycles make it awkward.
The Compliance Clock Is Already Running
Regulation caught up with shadow AI faster than most enterprises expected, and one date in particular lands this month.
Under the EU AI Act implementation timeline, most remaining provisions of the Act began applying on 2 August 2026. Member states must now maintain at least one national AI regulatory sandbox. A further milestone follows on 2 August 2027, when Article 6(1) obligations and legacy general-purpose model compliance take effect. If you process EU data or serve EU customers, ungoverned AI is no longer only a security problem.
Three frameworks now define what “reasonable care” looks like, and auditors increasingly expect at least one.
For the threat side, OWASP’s GenAI LLM Top 10 for 2026, released on 3 August 2026, and the companion Top 10 for Agentic Applications give engineering teams a concrete checklist. MITRE ATLAS supplies the adversary tactics catalogue, while CISA’s artificial intelligence resources and the UK NCSC machine learning principles translate all of it into operational guidance.
Why Blocking Shadow AI Never Works
Every organization tries the block first. Almost every organization abandons it within two quarters.
The reason is simple. Blocking a domain does not remove the need that drove the employee there. It relocates the activity to a phone, a home laptop, or a personal browser profile, where you have no visibility at all. Consequently, you trade a monitored risk for an invisible one.
The World Economic Forum’s Global Cybersecurity Outlook 2026 frames the same tension at a macro level, describing accelerating AI adoption alongside widening capability gaps. Stanford HAI’s AI Index puts it more bluntly still, documenting a widening gap between what AI can do and how prepared organizations are to manage it.
So the goal is not zero AI. The goal is zero ungoverned AI. Those are very different targets, and only one of them is achievable.
A Seven-Step Shadow AI Governance Program
Here is the sequence we use with clients. It works because it starts with visibility and ends with an alternative, rather than starting with a ban.
- Discover before you decide. Inventory AI usage from egress logs, SaaS management tooling, browser extension reports, and expense data. Include AI features inside tools you already own, since that category hides the most exposure.
- Classify by data sensitivity, not by tool popularity. A niche tool touching patient records outranks a popular one touching marketing copy. Rank by what the tool can reach.
- Fix access controls first. Recall that 97% of AI-related breaches involved missing access controls. Scope every AI integration to least privilege, use short-lived credentials, and log every call. Our zero trust content security approach applies directly.
- Publish a short, readable AI policy. Two pages beats twenty. State clearly what data may go into which tier of tool, name the approved options, and explain the approval route. A policy nobody reads governs nothing.
Steps Five to Seven: Replace, Monitor, Repeat
- Provide a genuinely good sanctioned option. This is the step that actually reduces shadow AI. If the approved tool is slower or weaker than the free one, employees will keep choosing the free one. Our Microsoft SaaS and DaaS and security as a service practices exist to close that quality gap.
- Monitor prompts and outputs, not just domains. Domain blocking sees destinations. Content inspection sees data. Pair data loss prevention with Exodus ARIA ADR, endpoint detection and response and Exodus Transparent Encryption.
- Re-run discovery every quarter. Shadow AI is not a project with an end date. New tools appear weekly, and vendors add AI features to existing products constantly.
For the infrastructure underneath this program, see our guides to enterprise IT infrastructure services and next-gen network security solutions.
What Good Looks Like in the First 90 Days
Programs stall when the first milestone is too far away, so keep the opening quarter deliberately small.
In weeks one to three, run discovery and produce a single list of every AI tool touching company data. Do not judge anything yet. Completeness matters far more than accuracy at this stage.
In weeks four to six, fix access controls on the ten highest-risk integrations. Scope permissions down, rotate long-lived credentials, and turn on logging. This is the step that moves the risk number most.
In weeks seven to nine, publish the two-page policy and name the approved tools. Announce it in plain language, and explain the approval path in a single sentence.
In weeks ten to twelve, stand up monitoring and book the next discovery run. Then report to leadership using one number: the share of AI usage now inside governed channels.
That final metric is the one worth tracking every quarter. It rises as your program works, and unlike breach counts, it does not require something to go wrong before it tells you anything.
Five Questions to Put to Every AI Vendor
Procurement language is your cheapest control, and these five questions surface most of what matters.
- Do you train on our data by default, and can we contractually opt out? Get the answer in the contract, not in a marketing page.
- What is your data retention period, and can we set it to zero? Retention you cannot configure is retention you cannot govern.
- Which sub-processors see our data, and where do they operate? This drives your residency and EU AI Act position.
- How do you scope and log agent permissions? If the answer is vague, assume the permissions are broad.
- Will you support post-quantum key exchange, and on what timeline? Data captured today stays readable later, a point we cover in Harvest Now, Decrypt Later.
Ask these of your existing vendors too, not only new ones. Most AI functionality in your estate arrived through renewals rather than through fresh procurement.
Shadow AI Risk by Sector
Exposure varies with the data you hold and the rules you answer to.
Healthcare. Protected health information pasted into a consumer chatbot is a reportable disclosure in most jurisdictions. Clinical staff face heavy documentation loads, so the pull toward AI summarization is strong. Sanctioned tooling matters more here than anywhere else.
Financial services. Model risk management already governs algorithms in this sector, and shadow AI sits squarely outside it. Add customer PII exposure and the audit questions get pointed quickly. Our look at why big cybersecurity budgets still fail covers the spending-versus-control mismatch.
Manufacturing and engineering. Intellectual property carries the highest per-record cost in shadow AI breaches. A single design document in a prompt can outweigh a year of security spending. Third-party exposure compounds it, as the Ericsson service provider breach showed.
Legal and professional services. Privilege does not survive a prompt sent to an unvetted third party. Client confidentiality obligations make this the sharpest risk of all.
Public sector and defense suppliers. Procurement rules increasingly require documented AI governance. Our reporting on the Pentagon’s supply-chain risk designation for an AI vendor shows how fast that scrutiny is tightening.
How ibm/SEIMless Helps Enterprises Govern Shadow AI
We are vendor-agnostic by design, and since 2001 we have selected technology on fit rather than on partnership incentives. With every vendor now claiming AI governance capability, that independence matters more than it used to.
Shadow AI is fundamentally a visibility and identity problem, so we treat it as a network problem. Discovery runs across your wide area network, SD-WAN and business class internet egress points. Enforcement runs through Exodus NxtGen Firewall, zero trust content security and EDR.
Data protection layers underneath. Exodus Transparent Encryption and our Exodus Quantum-Resistant Networking portfolio protect data at rest and data in motion, while Exodus Key Management tracks the credentials your AI integrations depend on.
Finally, the sanctioned alternative has to be good. Our cloud services, Microsoft Azure, telecom services and document management practices give employees capable approved tooling, which is the only durable way to shrink the shadow.
Frequently Asked Questions
What is shadow AI in simple terms?
Shadow AI is any AI tool, model, agent, or AI feature that handles company data without security review or approval. It includes consumer chatbots, employee-built agents, browser extensions, and AI features switched on inside software you already license.
How common is shadow AI in 2026?
IBM found shadow AI involved in 43% of studied security incidents in its 2026 report, more than double the prior year. Separately, Netskope found that 44% of workplace AI users touch personal, unmanaged AI applications.
Is shadow AI worse than shadow IT was?
In one respect, yes. Shadow IT typically moved data to an unapproved location, whereas shadow AI can move data into a system that may retain it, learn from it, or expose it through later queries. The data does not simply sit somewhere new.
Can we just block AI tools at the firewall?
Blocking alone rarely works. Employees move the activity to personal devices where you have no visibility, so you exchange a monitored risk for an invisible one. Discovery plus a good sanctioned alternative outperforms blocking every time.
What does the EU AI Act require from us?
Most remaining provisions of the Act began applying on 2 August 2026, with further obligations arriving on 2 August 2027. If you handle EU data, you need documented AI inventories, risk classification, and oversight.
Where should we start if we have done nothing yet?
Run discovery, fix AI access controls, and publish a two-page policy. Those three steps take weeks rather than quarters and remove most of the immediate exposure.
The Bottom Line
Shadow AI is not a passing phase, and it will not resolve itself. Adoption is running ahead of governance in almost every organization, and the 2026 data now prices that gap precisely: 43% of incidents, a record $4.99 million average breach cost, and 97% of AI-related breaches traced to missing access controls.
The organizations that handle this well are not the ones with the strictest policies. They are the ones that see what is running, control what it can reach, and give people an approved tool worth using. Visibility first, identity second, alternatives third.
Ready to find out what is actually running on your network? Get started with ibm/SEIMless or contact our team for a shadow AI discovery and governance assessment. You can also review our reports, browse our partners, read the FAQs, or explore distributor opportunities.
Further Reading: 20 Authoritative Sources
- Cost of a Data Breach Report 2026 — IBM
- Cost of a Data Breach: Shadow AI and Governance Findings — IBM Think
- Data Breach Investigations Report 2026 — Verizon Business
- As Data Breaches Grow Costlier, Ungoverned AI Creates New Risks — Cybersecurity Dive
- Netskope AI Report 2026 — Netskope Threat Labs
- Gen AI Data Violations More Than Double — Help Net Security
- Personal LLM Accounts Drive Shadow AI Data Leak Risks — Infosecurity Magazine
- AI Risk Management Framework — NIST
- AI RMF Generative AI Profile, NIST AI 600-1 — NIST
- Cybersecurity Framework 2.0 — NIST
- ISO/IEC 42001 Artificial Intelligence Management System — ISO
- EU AI Act Implementation Timeline — EU AI Act
- OWASP GenAI LLM Top 10 2026 — OWASP GenAI Security Project
- OWASP Top 10 for Agentic Applications 2026 — OWASP GenAI Security Project
- MITRE ATLAS — MITRE
- Artificial Intelligence Resources — CISA
- Machine Learning Principles — UK National Cyber Security Centre
- AI Safety Working Group — Cloud Security Alliance
- Global Cybersecurity Outlook 2026 — World Economic Forum
- AI Index Report — Stanford HAI
Complete ibm/SEIMless Resource Index
Quantum-Resistant Networking
NxT-Gen Network Security Solutions
Wide Area Networking and Connectivity
Cloud Services
Microsoft SaaS and DaaS
Telecom and PBX Services
Document Management
Company Pages
Blog Categories
All Blog Posts: Quantum and Post-Quantum
All Blog Posts: Cybersecurity and Threat Intelligence
All Blog Posts: Networking, Infrastructure and Managed Services
All Blog Posts: Barcode, Inventory and Data Operations
All Blog Posts: AI, Cloud and Industry Analysis