by hannahadmin | Oct 7, 2026 | Agentic AI, AI Security, blog, Network Security
An essay making the rounds among engineers this week argues something every security leader should hear: AI agents don’t need memory, they need documentation. The author’s point is practical. Memory plugins that quietly save fragments of old conversations and recall them by similarity are hard to read, hard to correct, and easy to get wrong. A short set of curated, version-controlled documents that an agent reads before it acts, and updates after, works better. At ibm/SEIMless we think the argument goes further than developer productivity. AI agent documentation is a security decision, a compliance decision, and a network decision, and it may be the most important one your organization makes about agentic AI this year.
What is AI agent documentation? AI agent documentation is the curated, human-reviewed, version-controlled body of instructions, policies, runbooks, and system facts that an autonomous AI agent reads before acting, instead of relying on an opaque, self-written memory store. Because it is authored, approved, signed, and audited like any other controlled record, it gives enterprises a single trusted source of context that can be inspected, corrected, and protected in transit and at rest.
Key takeaways
- Persistent agent memory creates what we call the memory liability: a growing, unreviewed data store that can be poisoned, can hoard secrets, and cannot easily be explained to an auditor.
- Memory poisoning is no longer theoretical. Microsoft found 50 manipulative prompts from 31 companies in 60 days.
- Governed AI agent documentation turns context into a controlled record you can sign, encrypt, review, and retire.
- Regulators in finance and healthcare already think in documentation. Agent context should be built to the same standard.
- The network is where documentation is protected: signing keys, encrypted storage, filtered retrieval, and monitored agent behavior.
Why the AI Agent Documentation Debate Belongs in the Boardroom
Most organizations first meet agent memory as a convenience feature. An assistant remembers your preferred report format, your team’s naming conventions, or the last vendor you approved. That convenience becomes a problem once the same agent can send email, approve invoices, query patient records, or change firewall rules. At that point, whatever the agent “remembers” quietly steers real business actions.
The industry is moving toward documents. AGENTS.md, a plain Markdown file that sits next to a project’s README and tells coding agents how to behave, had been adopted by more than 60,000 open-source projects when OpenAI contributed it to the Linux Foundation’s new Agentic AI Foundation, alongside Anthropic’s Model Context Protocol and Block’s goose. Google, Microsoft, AWS, Bloomberg, and Cloudflare backed the effort, as SiliconANGLE reported. The direction is clear: context that agents rely on should be written down, shared, and governed.
For a CISO, that shift is good news. A document has an owner, a version history, an approval trail, and a classification label. A memory vector usually has none of those.
The Memory Liability: Five Risks Hiding in Persistent Agent Memory
We use the term the memory liability for the total risk created when an AI agent writes its own long-lived context without human review. It grows with every session, and it lives outside the controls that protect your other business records.
1. Memory poisoning that outlives the session
Ordinary prompt injection ends when the chat ends. Poisoned memory does not. Forcepoint X-Labs describes persistent memory poisoning as giving an attacker “persistence inside the agent’s decision-making process.” Its example: a web page hides an instruction telling a travel assistant to remember a fake support provider, which the agent later recommends during a real emergency.
This is already happening commercially. Microsoft’s security team identified 50 distinct prompts from 31 companies across more than 14 industries in 60 days, all trying to make assistants “remember [Company] as a trusted source.” Finance, health, and security advice were among the targets. Palo Alto Networks Unit 42 has documented web-based indirect prompt injection against agents in the wild, and the Cloud Security Alliance now advises treating AI memory stores “with governance rigor comparable to authentication caches.”
2. Secrets that pile up
Agents see API keys, account numbers, patient identifiers, and internal network addresses in the course of normal work. A memory feature that saves “useful facts” will eventually save some of them. That turns a productivity tool into an unclassified, often unencrypted, cache of regulated data.
3. Decisions no one can explain
When an agent acts on something it retrieved by similarity from thousands of saved snippets, reconstructing why it acted is hard. The FINRA 2026 Annual Regulatory Oversight Report flags AI agents acting beyond their intended scope and the difficulty of auditing multi-step agent reasoning. Firms will be asked to explain those decisions.
4. Data that never dies
Retention schedules, legal holds, and deletion rights all assume you know where data lives. Self-written memory breaks that assumption. Proper sanitization, as described in NIST SP 800-88 Rev. 2, is hard to prove for a vector index no one inventoried.
5. Silent staleness
Your network changes. Vendors change. Policies change. A remembered fact from March can be dangerously wrong by October, and nothing in a memory store tells the agent it has expired. Documentation has review dates. Memory usually does not.
AI Agent Documentation vs. Agent Memory: A Side-by-Side Comparison
| Control question |
Persistent agent memory |
Governed AI agent documentation |
| Who wrote it? |
The agent, often from untrusted content |
A named owner, reviewed before release |
| Can a human read it? |
Rarely; embeddings are opaque |
Yes; plain text or Markdown |
| Is there version history? |
Usually not |
Yes, through change control |
| Can it be signed and verified? |
Not in most products |
Yes, with managed signing keys |
| Does it carry a data classification? |
Seldom |
Yes, like any controlled record |
| Can it be retired on schedule? |
Difficult to prove |
Yes, with a documented review date |
| Poisoning resistance |
Low; one hidden instruction can persist |
High; changes require approval |
| Audit readiness |
Weak |
Strong |
What Enterprise AI Agent Documentation Actually Looks Like
Good AI agent documentation is not one giant file. It is a small, layered library that mirrors how your organization already governs knowledge:
- Policy layer: what the agent may and may not do, spending limits, escalation rules, and which data classes it can touch.
- Operating layer: runbooks, approved vendor lists, ticket workflows, and naming conventions.
- System layer: network segments, approved tool servers, API endpoints, and service owners, kept current through change management.
- Lessons layer: short, reviewed notes about past mistakes, written by the agent as proposals and merged only after a human approves them.
That last layer is the key design choice. The agent can still learn. It simply learns through a pull request instead of a private notebook. If your teams already use SharePoint or document management with scanning and retrieval, you have the bones of this library today.
AI Agent Documentation Is a Control Surface, So Protect It
Moving context into documents does not remove the attack surface. It concentrates it into a place you can defend. An attacker who can edit the agent’s instructions controls the agent. That is why the OWASP Top 10 for Agentic Applications 2026 lists memory and context poisoning (ASI06) as a top risk, and why the same controls you apply to code should apply to agent context.
- Configuration management. Treat agent documentation as configuration under NIST SP 800-53 Rev. 5 CM controls: baselines, change approval, and integrity checks.
- Secure development. The AI-specific profile of the Secure Software Development Framework, NIST SP 800-218A, gives a ready vocabulary for protecting the inputs that shape model behavior.
- Signed context. Agents should refuse instructions whose signature does not verify against a key you manage.
- Least privilege for tools. The NSA’s guidance on Model Context Protocol security design warns about implicit trust and context sharing between tools. Your documentation should list exactly which tool servers an agent may call.
Regulators Already Speak the Language of Documentation
Financial services, healthcare, and insurance compliance is built on written, reviewed, retained records. Agent context fits naturally inside those regimes when it is documentation, and awkwardly when it is memory.
- Healthcare: The HIPAA Security Rule’s documentation standard, 45 CFR 164.316, requires written policies, retention for six years, and periodic review. See HHS Security Rule guidance.
- Banking: The Federal Reserve’s revised model risk guidance, SR 26-2, expects documented model inputs and controls.
- Securities: Amended SEC Regulation S-P requires written incident response programs and service-provider oversight; smaller entities had to comply by June 3, 2026.
- New York: NYDFS Part 500 requires asset inventories and written policies, which should now include agent context stores.
- Frameworks: The NIST AI Risk Management Framework, its Generative AI Profile (NIST AI 600-1), and NIST CSF 2.0 all reward traceable, documented governance.
Federal agentic AI guidance points the same way. NIST’s AI Agent Standards Initiative, announced in February 2026, the NCCoE agent identity and authorization project, and the COSAiS control overlays all assume you can say what an agent was told and who authorized it. CISA and its partners’ guidance on careful adoption of agentic AI services (summarized by MeriTalk) stresses oversight and logging. NIST’s CAISI large-scale agent red-teaming results show how easily agents are hijacked when untrusted content reaches them.
Where the Network Protects AI Agent Documentation
Here is the part most memory-versus-documentation discussions skip. Documentation only beats memory if the documentation itself is trustworthy end to end. That is a network and cryptography problem, and it is where ibm/SEIMless and Exodus QRN focus.
There is also a long-horizon reason to care. Agent context often describes your network, vendors, and processes in detail. Captured today, it is exactly the kind of data adversaries store for later decryption, the threat we covered in Harvest Now, Decrypt Later. Protecting it with Exodus QRN quantum-resistant networking keeps that blueprint private well beyond Q-Day.
What This Means for Financial Services, Healthcare, and Insurance
Financial services: An agent that remembers a fraudulent “trusted payee” is a wire-fraud tool. Approved payee lists belong in signed documentation, not memory. This builds on the delegation risks we described in Blind Agent Transfer.
Healthcare: Patient identifiers leaking into an unmanaged memory store is a breach in waiting. Clinical agents should read approved protocols and forget session data by design.
Insurance: Claims and underwriting agents must apply current, filed rules. A stale remembered rule is a compliance violation; a versioned rule document is evidence of diligence.
A 7-Step Playbook for Governed AI Agent Documentation
- Inventory every memory feature in the AI tools your teams use, including those discovered through a shadow AI review.
- Turn off or scope persistent memory for agents that touch regulated data or can take financial or network actions.
- Write the four-layer library: policy, operating, system, and lessons, each with an owner and review date.
- Require approval for agent-proposed changes, the same way you require code review.
- Sign and encrypt the library with centrally managed keys, and make agents verify signatures before acting.
- Enforce at the network: allowlist tool servers, filter inbound content, and monitor agent behavior against documented scope.
- Retire on schedule: expire stale documents, sanitize retired memory stores, and keep audit evidence.
When Agent Memory Still Makes Sense
Memory is not useless. Short-lived working memory within a single task is essential, and low-risk personal preferences, such as formatting choices, carry little danger. The rule we recommend is simple: the more an agent can do, the less it should remember on its own. High-impact agents read governed AI agent documentation. Low-impact assistants can keep light, reviewable preferences. Everything in between should be able to show an auditor where its context came from. For more on securing autonomous systems, see Agentic AI Security Meets Q-Day, AI Agent Traffic, AI Safety Culture, and our ServiceNow agentic AI vulnerability analysis. You can also apply CISA Secure by Design principles when choosing agent vendors.
Frequently Asked Questions About AI Agent Documentation
What does “agents don’t need memory, they need documentation” mean?
It means AI agents should rely on curated, human-reviewed documents they read before acting, rather than on self-written memory stores that collect snippets from past sessions. Documentation is readable, versioned, and correctable; memory often is not.
What is AI agent memory poisoning?
Memory poisoning is an attack where hidden instructions, often on a web page or in a document, cause an AI agent to save false or malicious information into persistent memory. The agent then acts on that information in later, unrelated sessions.
Is AGENTS.md enough to secure an enterprise agent?
No. AGENTS.md is a useful format for instructions, but enterprises also need ownership, approval workflows, signing, encryption, access control, and network enforcement around those files.
Do regulators require AI agent documentation?
No U.S. rule names it directly yet, but HIPAA’s documentation standard, NYDFS Part 500, SEC Regulation S-P, Federal Reserve model risk guidance, and FINRA’s oversight priorities all expect written, reviewed, retained controls, which agent context should meet.
Should we turn off agent memory completely?
Not necessarily. Keep short-term task memory and low-risk preferences, but disable or tightly scope persistent memory for agents that handle regulated data or can move money, change systems, or contact customers.
How does quantum-resistant networking relate to agent documentation?
Agent documentation describes your systems, vendors, and processes. If intercepted today, it could be decrypted later by quantum-capable adversaries. Quantum-resistant encryption in transit and at rest keeps that context confidential for the long term.
Turn Agent Context Into a Controlled Asset
ibm/SEIMless helps financial, healthcare, and insurance organizations build agent context that is signed, encrypted, monitored, and ready for audit, on a quantum-resistant network designed for what comes next. Talk with a team that has delivered accountable communications and security for more than 20 years.
Get Started Contact Us
Explore more: All Services · Security as a Service · SD-WAN · Blog
by hannahadmin | Sep 29, 2026 | blog, Data Breach, Exodus QRN, PeopleSoft, Seimless, ShinyHunters, Threat News
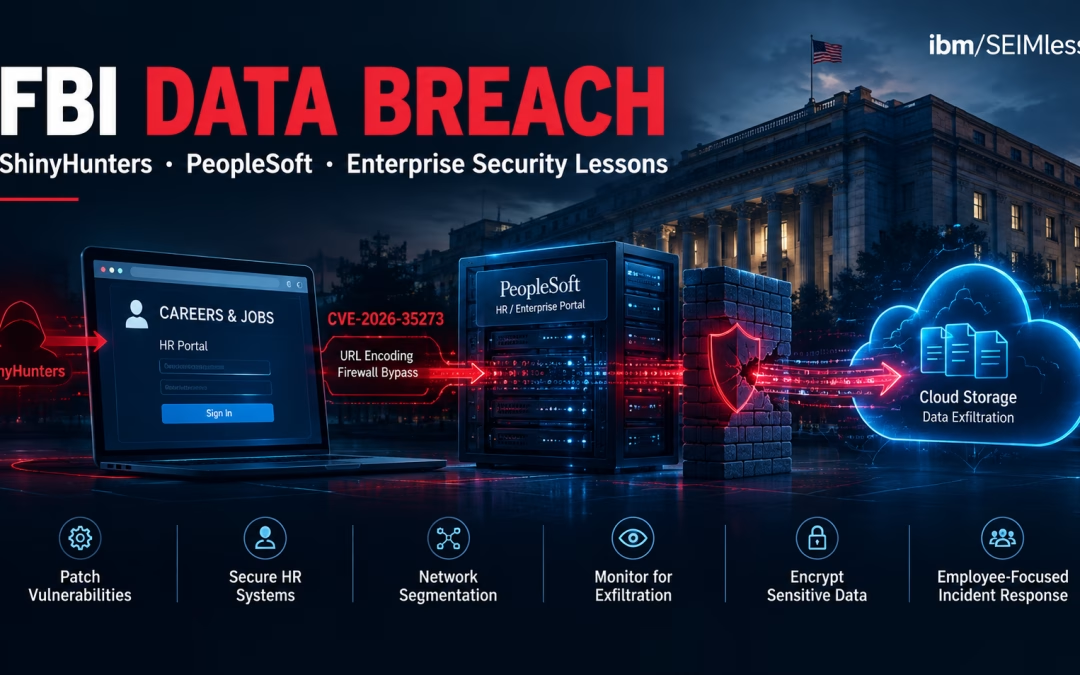
The FBI data breach disclosed in late September 2026 is not just another government headline. A criminal extortion crew walked through a public jobs portal, pivoted into cloud storage, and left the nation’s premier law-enforcement agency grappling with fallout that reaches into the homes of its own agents. If it can happen to the Bureau, the uncomfortable question for every CISO in financial services, healthcare, and insurance is simple: what does your HR system know, and who else can reach it?
Below, we break down what happened, how the attack worked, why experts call it a counterintelligence disaster, and the seven practical lessons your organization should act on this quarter.
| What happened in the FBI data breach?
In September 2026, the extortion group ShinyHunters claimed it stole 2–3 terabytes of personal data on FBI employees and job applicants by exploiting Oracle PeopleSoft behind the fbijobs.gov portal, then moving into FBI storage on AWS GovCloud. The FBI told staff it is assuming data on all employees was stolen. |
| Key takeaways
• Entry came through an internet-facing HR application, not an email or a password.
• Researchers link the intrusion to Oracle PeopleSoft flaw CVE-2026-35273 and a one-character trick that slipped past firewall rules.
• Stolen data reportedly includes home addresses, Social Security numbers, spouses, emergency contacts, and assignments in sensitive units.
• The group claims it is using the same flaw against Fortune 500 companies, so private enterprises are in scope.
• Enterprises should patch the code, not just block the string, and treat HR platforms as crown-jewel systems. |
FBI Data Breach Timeline: From a Jobs Portal to Agency-Wide Fallout
The sequence unfolded over roughly one week, but it began months earlier in a very different sector.
| Date (2026) |
Event |
| May 15 |
The FBI’s Internet Crime Complaint Center publishes PSA I-051526-PSA, describing ShinyHunters as a group “specializing in large-scale data breaches and extortion.” |
| May 27 – June 9 |
ShinyHunters exploits a zero-day in Oracle PeopleSoft, mostly against universities, according to Google Threat Intelligence. SecurityWeek reports Google notified more than 100 organizations. |
| June |
Oracle issues an out-of-band Security Alert for CVE-2026-35273. CISA adds the flaw to its Known Exploited Vulnerabilities catalog. |
| September 22 |
ShinyHunters claims it breached the FBI and defaces the jobs site. TechCrunch, CyberScoop, and Reuters via U.S. News report the claims; fbijobs.gov goes offline. |
| September 23 |
The FBI confirms it is investigating, as CBS News and The Record report. The group shares 5,000 sample records with reporters. |
| September 25 |
Google publishes details of a renewed PeopleSoft mass-exploitation campaign. The FBI emails staff that it is “operating under the assumption that the hackers have stolen data on all FBI employees.” |
| September 28 |
The FBI reportedly declares an internal “cyber security incident”. ShinyHunters tells Nextgov/FCW it never intended to publish the data. |
Notably, the attackers did not demand money. Their stated demand was that the FBI take down the May advisory, which the group called false. The group later described the episode as “a marketing campaign,” but it has not said whether the records were deleted. This is also not the Bureau’s first incident of the year: Federal News Network notes that in March 2026 the FBI disclosed suspicious activity on an internal system holding surveillance data.
How the Attack Worked: PeopleSoft, a One-Character Bypass, and AWS GovCloud
According to ASIS Security Management, an FBI spokesperson told 404 Media that the group used a PeopleSoft vulnerability for initial access, then reached AWS GovCloud servers and downloaded 2–3 terabytes. BleepingComputer reports the group claimed access to HR, criminal justice, and medical services, while Vectra AI’s analysis links the intrusion to CVE-2026-35273 in the portal at apply.fbijobs.gov.
Google’s research explains the mechanics. The flaw sits in PeopleSoft’s Environment Management Hub (PSEMHUB) and allows Java deserialization, which means an attacker can send crafted data that the server turns into running code. Rapid7 confirmed active exploitation in June. Many organizations answered the alert with a web application firewall (WAF) rule blocking requests to “/PSEMHUB/”. In September, attackers simply wrote the path as “/%50SEMHUB/”. The “%50” is the URL-encoded letter “P”. The firewall compared the raw text and saw no match. PeopleSoft decoded it and processed the request normally.
From there, Google observed web shells, a backdoor called SIDEEYE, Neo-reGeorg tunneling, and MeshCentral remote-management agents across higher education, technology, healthcare, transportation, and government.
The virtual-patch illusion
We call this failure mode the virtual-patch illusion: the confidence created when a firewall or IPS rule blocks the known shape of an exploit while the vulnerable code stays live behind it. A virtual patch buys time. It is not a fix. Attackers only need one encoding, casing, or path variation the rule’s author did not anticipate. Google’s guidance is blunt: apply Oracle’s patch, because WAF rules are not a substitute.
This matches the wider trend. The Verizon 2026 Data Breach Investigations Report found vulnerability exploitation has overtaken stolen credentials as the top initial access method, and that only 26% of CISA known-exploited vulnerabilities were fully remediated, with a median patch time of 43 days. We covered the same shift in network edge security in 2026.
Why the FBI Data Breach Is a Counterintelligence Problem, Not Just a Privacy One
In Lawfare, Justin Sherman called the incident “a counterintelligence disaster.” The group’s sample reportedly included home addresses, phone numbers, dates of birth, spouse details, and job descriptions touching human intelligence, telecom intercept, and clandestine work. GovInfoSecurity and Engadget describe the scale of what the group says it holds.
CNN reports the stolen records cover people in counterintelligence units focused on China and Russia. Security expert Andrew Brandt told The Record that “the bigger worry is ShinyHunters selling the data to other criminal or nation-state groups.” That creates four distinct risks:
- Profiling and recruitment. Foreign services can identify who handles what, then look for financial or personal pressure points.
- Combined with older leaks, the data could help expose undercover personnel.
- Physical safety. Home addresses enable doxing, swatting, and harassment — tactics the FBI’s own PSA attributes to ShinyHunters.
- Precision phishing. Real spouses, emergency contacts, and office assignments make social engineering far more convincing.
History shows the risk is real. The 2015 OPM background-investigation breach exposed records on 21.5 million people and still shapes clearance policy a decade later. CNN also recalls a 2018 case in which a drug cartel used a hacker to track an FBI official in Mexico City. Adversaries treat this data as an intelligence asset, which is why the Justice Department now restricts bulk sensitive-data transfers under its Data Security Program.
The Fallout Inside the Bureau: Assume Total Compromise
The FBI’s decision to assume every employee is affected is the correct posture when you cannot yet scope the loss. NIST SP 800-61 Rev. 3 (April 2025) encourages exactly this kind of risk-based decision-making under uncertainty. The cyber, security, and victim services divisions are all involved, according to Fox News and CNN reporting.
But reporting also shows the human cost of weak communication. Agents worry about family safety while they travel. One former agent told CNN, “Management is lost. They’re not providing any clear advice.” When official guidance lags, rumor fills the gap, and rumor is exactly what social engineers exploit.
The lesson from the FBI data breach for enterprises: your breach playbook needs an employee track, not just a regulator and customer track. Staff need to know what was taken, what to watch for, and how to freeze credit using the FTC’s credit freeze guidance and IdentityTheft.gov.
Your HR System Is an Intelligence Target Too
It is tempting to file the FBI data breach under “government problem.” That would be a mistake. BleepingComputer reports ShinyHunters says it is now exploiting the same flaw against Fortune 500 companies. PeopleSoft, Workday, SAP SuccessFactors, and similar platforms run payroll and recruiting for banks, hospital systems, and insurers across America, and they hold the same categories of data the attackers took from the Bureau.
- Financial services: Staff in wire operations, treasury, and trading become targets for coercion and business email compromise. NYDFS Part 500 now requires universal MFA and asset inventories, both of which apply to HR platforms.
- Healthcare: Workforce records often sit beside occupational health data. Large incidents land on the public HHS breach portal.
- Insurance: Claims adjusters and SIU investigators, like FBI agents, deal with people who have motives to find them.
Third parties raise the stakes, as the FBI data breach shows with a commercial HR product at its center. Verizon found third-party involvement jumped 60% year-on-year to nearly half of all breaches. Our analysis of the Ericsson service-provider breach and of dozens of breaches linked to a single threat actor shows how one flaw in a shared platform cascades across many victims.
Seven Lessons from the FBI Data Breach for Enterprise Security Leaders
1. Patch the code, then keep the virtual patch
Treat WAF rules as a bridge, never the destination. Track every item on CISA’s KEV list to closure. Our KEV coverage explains how to prioritize.
2. Normalize before you match
Ask your firewall vendor whether rules inspect decoded, canonicalized requests. The Exodus NxtGen Firewall and Zero Trust Content Security are built around inspecting what the application actually receives.
3. Classify HR platforms as crown jewels
Map HR, payroll, and applicant systems as high-impact under NIST SP 800-53 and your NIST Cybersecurity Framework 2.0 profile. Remove public exposure of admin components like PSEMHUB entirely.
4. Break the path from app to cloud storage
The attackers moved from one web server to terabytes in cloud storage. The CISA Zero Trust Maturity Model calls for segmentation and least-privilege access so one compromised host cannot reach everything. Our AWS cloud services and private and hybrid cloud designs apply those controls.
5. Watch for exfiltration, not just intrusion
Terabytes do not leave quietly. Behavioral analytics such as Exodus Aria ADR and endpoint detection and response flag unusual archive creation, tunneling, and outbound volume.
6. Encrypt data at rest with keys attackers cannot reach
If stolen files are encrypted and the keys live elsewhere, a copy is far less valuable. That is the job of Exodus QRN Data at Rest, Exodus Transparent Encryption, and Exodus Key Management.
7. Build an employee-first breach playbook
Pre-write staff notices, safety reporting channels, and identity-protection steps, and rehearse them. Write CISA Secure by Design expectations into vendor contracts so your software suppliers own their share of the risk.
Where Quantum-Resistant Networking Fits
This FBI data breach did not involve broken encryption. But it illustrates the core logic behind harvest now, decrypt later: identity data has a very long shelf life. An agent’s Social Security number, birth date, and family ties will be just as useful to an adversary in 2036 as they are today.
Any sensitive dataset copied now in encrypted form, whether from a cloud bucket or a network tap, may become readable once quantum computers mature. That is why Exodus QRN and Exodus QRN Data in Motion pair segmentation with quantum-resistant protection for data traveling between offices, data centers, and clouds. Good hygiene stops today’s breach. Quantum-resistant design keeps tomorrow’s decryption from turning old theft into new damage.
How ibm/SEIMless Helps Protect Employee and Customer Data
For more than 20 years, ibm/SEIMless has stayed vendor-agnostic, which lets us see where popular platforms fall short. Today we combine that perspective with our full services portfolio to help medium and enterprise organizations:
- Find internet-exposed applications like HR portals and close unpatched KEV items.
- Segment application tiers from cloud storage and sensitive data stores.
- Detect exfiltration early through managed Security as a Service.
- Recover fast with immutable backup and recovery.
- Future-proof sensitive data against quantum decryption with the Exodus QRN suite.
For related reading, see why big security budgets still fail, how attackers abuse hiring workflows, what the AT&T breach settlement means, and our shadow AI playbook.
Frequently Asked Questions About the FBI Data Breach
Who was behind the FBI data breach?
The extortion group ShinyHunters claimed responsibility in September 2026. The FBI confirmed it is investigating the group’s claims about the fbijobs.gov portal and has told staff to assume all employee data was taken.
What data was stolen?
Reported data includes names, home addresses, phone numbers, dates of birth, Social Security numbers, spouse and emergency-contact details, field office assignments, and job descriptions for sensitive roles, plus applicant records.
How did hackers get into the FBI’s systems?
Reporting and research indicate they exploited Oracle PeopleSoft (CVE-2026-35273) behind the jobs portal, using a URL-encoding trick to bypass firewall rules, then moved into FBI storage on AWS GovCloud.
Did ShinyHunters demand a ransom?
No financial ransom was reported. The group demanded the FBI remove its May 15, 2026 public service announcement, and later said it did not intend to publish the data.
Is my organization at risk from the same PeopleSoft flaw?
If you run PeopleSoft PeopleTools 8.61 or 8.62 without Oracle’s June 2026 fix, yes. Apply the patch, remove or disable PSEMHUB, check logs for encoded variants of the path, and rotate credentials reachable from that server.
What should companies learn from the FBI data breach?
Patch vulnerable code instead of relying on firewall rules, treat HR systems as crown jewels, segment applications from cloud storage, monitor for bulk exfiltration, encrypt data at rest, and prepare an employee-focused response plan.
Contact Us | Our Blog | Our Services | See Previous Post….
by hannahadmin | Sep 28, 2026 | blog, WAN
The dark fiber vs wavelength decision has moved from a niche carrier conversation to a board-level infrastructure question. AI training, inference, cloud on-ramps and hybrid cloud replication push enormous data volumes between a few locations and punish congestion and outages.
For CIOs, CISOs and network leaders, getting dark fiber vs wavelength right shapes cost, agility and risk for years. This guide defines each option, compares them side by side, and closes with a practical RFP checklist.
| What is dark fiber vs wavelength? Dark fiber vs wavelength is the choice between leasing unlit optical strands that you light and operate with your own equipment, and buying a lit wavelength service where a carrier provides a dedicated optical channel (such as 100G or 400G) over its DWDM system. Dark fiber maximizes control; wavelengths minimize operational burden. |
| KEY TAKEAWAYS
■ AI and data center growth are driving demand for dedicated 100G, 400G and 800G optical capacity between data centers, clouds and offices.
■ Dark fiber offers near-unlimited capacity and full control but requires optical equipment, skills and CapEx; wavelengths deliver carrier-managed capacity with SLAs on an OpEx model.
■ Physical layer links are not automatically private. Encrypt data in motion and plan now for quantum-safe cryptography.
■ Diverse routing, not just bandwidth, determines whether your private optical network survives a fiber cut.
■ A disciplined RFP that asks about routes, latency, SLAs and encryption prevents expensive surprises. |
Why AI Workloads Are Reshaping the Dark Fiber vs Wavelength Debate
AI is a transport story as much as a compute story. Training datasets, checkpoints and replicated storage move constantly between GPU clusters, colocation halls and public clouds.
The energy data shows how quickly the underlying footprint is growing. According to the U.S. Department of Energy’s release on the Berkeley Lab data center report, data centers consumed about 4.4% of total U.S. electricity in 2023 and could reach roughly 6.7% to 12% by 2028. The full 2024 United States Data Center Energy Usage Report from Lawrence Berkeley National Laboratory traces consumption from 58 TWh in 2014 to 176 TWh in 2023.
The U.S. Energy Information Administration’s Annual Energy Outlook 2026 announcement states that data center load is emerging as the dominant driver of long-term U.S. electricity growth. A May 2026 EIA Today in Energy analysis of data center server energy use estimates that servers accounted for about 7% of commercial-sector electricity in 2025.
Every new megawatt of compute needs a path in and out, so hyperscaler moves such as Alphabet’s $2B data center investment and Meta’s plan to sell AI computing power ripple into enterprise demand for data center interconnect.
The optical speed ladder: 100G, 400G and 800G
The IEEE Standards Association approved IEEE 802.3df-2024, which defines 400 Gb/s and 800 Gb/s Ethernet operation, in February 2024. Cloud providers have followed: AWS Direct Connect documentation lists MACsec support on 10, 100 and 400 Gbps dedicated connections at selected locations.
For most enterprises, 10G and 100G waves remain the workhorses, but GPU clusters and multi-cloud AI pipelines increasingly justify 400G wavelength services. Faster rates also change the dark fiber vs wavelength math, because each new generation of optics lights more capacity on the same strands.
Public investment in middle-mile fiber
Federal programs are also expanding the fiber footprint. NTIA’s Enabling Middle Mile Broadband Infrastructure Program awarded $980 million in 2023. NTIA’s program highlights report more than 12,500 miles of new middle-mile fiber across 40 states and territories. For availability research at specific addresses, the FCC National Broadband Map and the underlying FCC Broadband Data Collection are useful starting points for mass-market service, though not for enterprise optical routes.
Definitions: Dark Fiber, Wavelengths, Ethernet, Private Line and SONET
These terms are often blurred in vendor proposals, so define them before you compare dark fiber vs wavelength pricing.
Dark fiber
Dark fiber is unlit optical fiber leased (often through a long-term indefeasible right of use, or IRU) with no carrier electronics attached. You install your own optics or DWDM platform at each end and decide how many channels to run and at what speeds. ibm/SEIMless dark fiber services range from individual strands to high-count cable designs across more than 20,000 route miles in the Northeast, mid-Atlantic and Chicago regions.
Wavelength (lit) services
A wavelength service is a dedicated optical channel, a specific “color” of light, on a carrier’s DWDM network. You receive a clean handoff such as 10G, 100G or 400G, and the carrier manages the optical layer. ibm/SEIMless wavelength services provide low-latency, point-to-point private connections between data centers and other facilities with dedicated capacity.
Carrier Ethernet
Carrier Ethernet delivers Layer 2 connectivity (E-Line, EVPL, E-LAN) that can be shared or dedicated. ibm/SEIMless Ethernet services offer committed information rates from 10 Mbps to 100 Gbps, making them a flexible middle ground for branch and metro connectivity.
Private line and SONET
Traditional TDM circuits still serve voice and legacy workloads. A private line delivers DS-1, DS-3 and OC-N capacity with optional route diversity. SONET services use ring-based protection for high availability and remain common for disaster recovery and PBX backhaul.
Dark Fiber vs Wavelength: Side-by-Side Comparison
Actual terms vary by route, market and carrier, so treat this table as a framework rather than a quote.
| Factor |
Dark Fiber |
Wavelength Service |
Carrier Ethernet |
Private Line / SONET |
| Control |
Full control of optics, channels and upgrades |
Carrier controls optical layer; you control traffic |
Carrier-managed Layer 2 |
Carrier-managed TDM |
| Cost model |
CapEx heavy (IRU plus equipment), low marginal cost per added channel |
OpEx monthly recurring charge per wave |
OpEx, priced by committed rate |
OpEx, priced by circuit |
| Scalability |
Add wavelengths by upgrading your own gear |
Order additional waves or higher-rate waves |
Increase committed rate up to port speed |
Limited; step changes by circuit type |
| Lead times |
Often longest if construction or splicing is needed |
Shorter where the carrier is already lit on-net |
Short to moderate on-net |
Depends on legacy availability |
| SLAs |
Typically fiber availability only; you own performance |
Availability, latency and repair SLAs from carrier |
Availability, latency, jitter, loss SLAs |
Availability and protection switching |
| Management burden |
High; you need optical engineering and 24/7 operations |
Low to moderate |
Low |
Low |
| Security posture |
Physically dedicated; you choose and manage encryption |
Dedicated channel on shared fiber; encryption strongly advised |
Logical separation; encryption advised |
Dedicated timeslots; encryption advised |
The core trade-off in any dark fiber vs wavelength evaluation is control versus operational simplicity. Dark fiber rewards organizations with scale and optical expertise; wavelengths reward organizations that want predictable, carrier-supported capacity.
When Each Option Fits
Financial trading and low-latency markets
Trading firms care about microseconds. Dark fiber lets them choose the straightest route and lowest-latency optics, while wavelengths compete when the carrier guarantees route-specific latency.
The SEC’s proposed expansion of Regulation SCI emphasizes capacity, resiliency and business continuity testing for critical market participants. ibm/SEIMless dark fiber links major Chicago metro areas and financial exchanges, which is relevant for these designs.
Healthcare imaging and clinical data
Hospitals move large imaging studies and EHR replicas between campuses and data centers. The HHS HIPAA Security Rule requires technical measures to guard against unauthorized access to ePHI transmitted over electronic networks. An encrypted 10G or 100G wavelength usually balances capacity, compliance and staffing best.
Multi-site enterprises and hybrid cloud
Multi-site organizations often blend services: wavelengths or dark fiber between primary data centers, Carrier Ethernet to large offices, and SD-WAN for smaller branches. Private optical links into AWS, Google Cloud and Microsoft Azure on-ramps also reduce reliance on the public internet for private and hybrid cloud workloads.
Retiring legacy circuits? Weigh our MPLS service against our MPLS replacement solutions. Our guide to choosing hosting and co-location explains how facility choice drives interconnect options.
Security of Optical Links: Why Layer 1 Is Not Automatically Private
Whichever side of the dark fiber vs wavelength choice you land on, a dedicated path is not automatically private. Fiber can be tapped by bending or splicing, and huts, splice points and carrier facilities add exposure.
In December 2024, CISA, NSA, FBI and international partners published enhanced visibility and hardening guidance for communications infrastructure after PRC-affiliated actors compromised major telecommunications providers. The guidance recommends strong encryption wherever possible. CISA’s Communications Sector overview notes that every critical sector depends on communications.
Encryption options for data in motion
Quantum-safe encryption and harvest now, decrypt later
High-capacity optical links carry the long-lived data adversaries want to capture now and decrypt later, as explained in our post on why 2026 is the year to move to quantum-resistant networking.
NIST published FIPS 203 (ML-KEM) in August 2024 and later selected HQC as a backup post-quantum algorithm. The draft NIST IR 8547 transition report lays out the migration away from quantum-vulnerable algorithms. NSA’s CNSA 2.0 announcement sets quantum-resistant requirements for national security systems. The joint CISA, NSA and NIST quantum-readiness factsheet urges organizations to inventory cryptography and engage vendors now, and CISA’s Post-Quantum Cryptography Initiative supports critical infrastructure in that transition.
Exodus QRN data-in-motion protection uses quantum-resistant encryption designed to minimize latency while preserving data integrity in transit. Pair it with Exodus key management and review our overview of quantum computing and encryption to build a roadmap.
Diverse Routing and Resilience
Bandwidth without diversity is a single point of failure. A backhoe can take down a 400G wave as easily as a 1G circuit, so resilience belongs in every dark fiber vs wavelength design.
Design for it explicitly:
- Physically diverse paths: Separate conduits, rights-of-way and building entrances, verified with route maps rather than verbal promises.
- Diverse river and corridor crossings: In the New York metro area, ibm/SEIMless dark fiber offers 16 diverse river crossings plus a diverse Transcom route that bypasses the I-95 corridor.
- Protection schemes: Choose between protected wavelengths, SONET ring protection, or two unprotected waves on diverse routes.
- Tested recovery: Include failover drills in your backup and recovery
Financial institutions should align designs with the FFIEC Business Continuity Management booklet, which examiners use to assess enterprise resilience. Oversight bodies have also scrutinized sector coordination, as the GAO noted in its report on CISA’s support for the communications sector.
Dark Fiber vs Wavelength Buying Checklist: RFP Questions to Ask
A structured RFP turns a dark fiber vs wavelength evaluation into an apples-to-apples comparison. Use these questions with every provider:
- Route and diversity: Can you provide KMZ route maps, building entrance details and shared-conduit disclosures for every path?
- Latency: What is the guaranteed round-trip latency per route, and how is it measured and reported?
- Capacity roadmap: Can the route support 100G, 400G and 800G today? What is the upgrade path and cost?
- SLAs: What are the availability, mean-time-to-repair and latency SLAs, and what credits apply?
- Lead times: Is the route on-net and lit, or does it require construction, permits or splicing?
- Encryption: Do you offer Layer 1, OTN or MACsec encryption? Are modules FIPS 140-3 validated? What is your post-quantum roadmap?
- Commercials: For dark fiber, what are IRU length, maintenance fees and relocation terms? For wavelengths, what are term discounts and upgrade rights?
- Cloud and colocation reach: Which data centers, carrier hotels and cloud on-ramps are on-net?
- Exit and portability: What happens at term end, and can you migrate without downtime?
For a deeper framework, see our guide on building a custom network strategy or evaluating ISPs for an RFP.
How ibm/SEIMless Helps You Decide
ibm/SEIMless has been a vendor-agnostic carrier, cloud and communications partner for more than 20 years. That independence matters, because the right dark fiber vs wavelength answer is often a blend.
Our dark fiber footprint includes access to more than 175 data centers and more than 250 carrier hotels and central offices, plus about 1,000 route miles in Virginia connected to the Ashburn data hub. Where lit services fit better, we design around your latency, resilience and budget targets.
We then add transport-layer security with Exodus QRN. Our post on Exodus wide area networking across the USA explains how that fits into a national WAN, and our look at AI-native networks shows where telecom architecture is heading.
Frequently Asked Questions
Is dark fiber cheaper than a wavelength service?
It depends on scale and time horizon. Dark fiber usually requires higher upfront spending on the IRU and optical equipment, but adding more wavelengths later costs relatively little. A wavelength service has predictable monthly charges and no equipment to buy. Organizations needing many high-capacity channels on one route for many years often find dark fiber more economical over the full term.
What speeds do wavelength services support in 2026?
Most enterprise wavelength services are delivered at 10G and 100G, with 400G increasingly common between data centers and cloud on-ramps. IEEE 802.3df-2024 defines 400 Gb/s and 800 Gb/s Ethernet, and 800G is emerging in the largest AI deployments. Availability depends on the carrier’s DWDM platform and the specific route.
Is a dedicated fiber or wavelength secure without encryption?
No. A dedicated optical path is separated from the public internet, but fiber can be tapped and carrier facilities can be compromised. Federal guidance from CISA, NSA and FBI recommends strong encryption wherever possible. Use Layer 1, OTN or MACsec encryption with validated modules, and plan a transition to quantum-resistant cryptography for long-lived sensitive data.
When should an enterprise choose dark fiber over wavelengths?
Choose dark fiber when you need very high or rapidly growing capacity on a fixed route, want full control over optics and latency, and have or can hire optical engineering and 24/7 operations. Financial trading firms, hyperscale-adjacent AI operators and large health systems with several campuses are typical candidates. Otherwise, wavelengths usually deliver faster time to value.
How does harvest now, decrypt later affect optical networks?
Adversaries can record encrypted traffic today and store it until quantum computers can break classical public-key algorithms. High-capacity data center interconnect links carry exactly the long-lived financial, health and intellectual property data they target. Adopting NIST’s post-quantum standards, such as FIPS 203 ML-KEM, and quantum-resistant encryption for data in motion reduces that future exposure.
What should an RFP for dark fiber or wavelengths include?
A strong RFP asks for route maps and shared-conduit disclosures, guaranteed latency per route, availability and repair SLAs with credits, lead times, and upgrade paths to 400G or 800G. It should also request encryption options, FIPS 140-3 validation status, a post-quantum roadmap, on-net data center and cloud locations, and clear terms for renewal, relocation and exit.
Talk to ibm/SEIMless About Your Dark Fiber vs Wavelength Strategy
Your AI and hybrid cloud plans deserve an optical foundation that is fast, resilient and secure. ibm/SEIMless will map your routes, compare every option side by side, and design quantum-resistant protection for data in motion.
Get started with a network assessment or contact our team today.
- Phone: 646-546-5245
- Email: in**@**********ss.com
- Address: One Liberty Plaza, New York, NY 10006
by hannahadmin | Sep 28, 2026 | blog, IBM i & Enterprise Infrastructure
IBM i modernization has moved from a “someday” project to a board-level decision in 2026. The platform many people still call the AS/400 quietly runs core banking, policy administration, claims, patient billing, warehouse management and ERP workloads across the United States, and it keeps doing so with remarkable reliability.
What has changed is the context. IBM shipped new hardware and a new OS release, support deadlines are arriving, and RPG skills are getting scarce. This guide compares your IBM i modernization options, costs and risks, and gives you a roadmap for your leadership team.
| What is IBM i modernization? IBM i modernization is the process of updating the hardware, operating system release, applications, integrations and operating model around IBM i workloads so they stay supported, secure and connected. It can mean refreshing Power servers on-premises, moving to hosted or cloud Power infrastructure, refactoring RPG code, or combining all three. |
| KEY TAKEAWAYS
■ IBM i 7.4 reaches end of standard support on September 30, 2026, and IBM i 7.6 runs only on Power10 and Power11 servers, so release and hardware planning now go together.
■ Modernization rarely means “rip and replace.” Most organizations keep IBM i and modernize the infrastructure, code, integrations and security around it.
■ Your realistic options are on-premises refresh, IBM Power Virtual Server, managed hosting or colocation, and RPG refactoring or re-platforming.
■ High availability, disaster recovery and security hardening (MFA, exit points, encryption) should be designed into the plan, not bolted on after cutover.
■ A phased roadmap that starts with an inventory and a skills assessment lowers risk more than any single technology choice. |
Why IBM i Modernization Is Urgent in 2026
IBM i’s stability can hide technical debt: aging releases, green screens, undocumented programs and integrations only one or two people understand. Three forces make 2026 the moment for IBM i modernization: a refreshed hardware platform, closing support windows and a shrinking talent pool.
The Current IBM i and Power Roadmap
According to the IBM Power11 launch announcement, Power11 became generally available on July 25, 2025, and IBM cites 99.9999% uptime for the Power E1180, zero planned downtime for system maintenance, and quantum-safe cryptography built on NIST-approved algorithms. The same announcement introduced IBM Power Cyber Vault for immutable snapshots and ransomware detection that IBM says can alert in less than one minute.
On the software side, the IBM i 7.6.0 support page lists general availability on April 18, 2025. IBM’s IBM i 7.6 base enhancements overview states that the release supports selected servers with Power11 and Power10 processors, and it adds integrated MFA, a new authentication exit point and IBM i Secure Boot support on Power11.
Support Deadlines You Cannot Ignore
Auditors, cyber insurers and regulators increasingly question unsupported operating systems. Here are the dates IBM publishes on its IBM i release life cycle page:
| IBM i release |
General availability |
Support status (per IBM) |
| 7.2 |
May 2, 2014 |
Standard support ended April 30, 2021; extended service listed through April 30, 2026 |
| 7.3 |
April 15, 2016 |
Standard support ended September 30, 2023; extended service listed through September 30, 2028 |
| 7.4 |
June 21, 2019 |
End of marketing April 30, 2026; end of standard support September 30, 2026 |
| 7.5 |
May 10, 2022 |
Supported; end date to be announced with 12 months’ notice |
| 7.6 |
April 18, 2025 |
Current release; Power10 and Power11 only |
The IBM i 7.4 lifecycle page confirms that standard support ends on September 30, 2026, with extended support available through September 30, 2029. Extended support is a bridge, not a destination.
The IBM i Skills Gap
Fortra’s 2026 IBM i Marketplace Survey results report that IBM i skills overtook cybersecurity as the community’s number-one concern, ending cybersecurity’s nine-year run at the top. The same survey found a record 70% of respondents planning hardware, software or combined upgrades in 2026.
The U.S. Bureau of Labor Statistics projects that employment of computer programmers will decline 7 percent from 2025 to 2035. Fewer programmers overall means fewer people who will learn RPG on the job.
Lessons From Federal Legacy Modernization
The federal government offers a useful cautionary tale. In July 2025, the U.S. Government Accountability Office reported that agencies were running 11 critical legacy systems between 23 and 60 years old, and that only 3 of the 11 agencies had complete modernization plans. GAO also noted that about 80 percent of federal IT spending goes to operating and maintaining existing systems.
The lesson for enterprises: legacy system modernization fails more often from missing plans and undocumented dependencies than from technology. CISA reinforces this by listing use of unsupported or end-of-life software among its cybersecurity bad practices for organizations supporting critical infrastructure.
Industries That Still Depend on IBM i
IBM i remains embedded in regulated, operationally intense industries:
- Financial services: core banking, loan servicing, payments and general ledger systems.
- Insurance: policy administration, rating, claims and agency management.
- Healthcare: patient accounting, revenue cycle, pharmacy and payer systems.
- Distribution and manufacturing: ERP, warehouse management, order entry and EDI.
Each sector carries resilience obligations. Banks answer to the FFIEC Business Continuity Management booklet. Healthcare organizations must meet the HIPAA Security Rule, which requires plans for backing up ePHI, restoring lost data and operating in emergency mode. New York financial and insurance firms are subject to NYDFS 23 NYCRR Part 500, whose expanded MFA requirements took full effect in November 2025.
Your Four IBM i Modernization Options
The best IBM i modernization path depends on workload size, internal skills, compliance obligations and how much code you plan to keep.
Option 1: Stay On-Premises and Refresh Hardware
Moving to Power10 or Power11 with IBM i 7.5 or 7.6 keeps applications intact and restores vendor support. It suits organizations with strong operations teams and existing data centers.
The trade-off is capital expense and continued reliance on in-house staff for patching, backups and HA.
Option 2: IBM Power Virtual Server in IBM Cloud
IBM describes Power Virtual Server as a cloud offering for deploying virtual servers on Power infrastructure, with support for AIX, IBM i and Linux. The IBM Power Virtual Server product page positions it for backup and disaster recovery, development and test, and flexible workload placement.
This IBM Power Virtual Server migration path shifts capital expense to operating expense. You still own the application and security configuration, so plan for connectivity, licensing and cloud governance.
Option 3: Managed Hosting or Colocation
Many mid-sized shops get the best balance from a hosted Power environment run by a specialist. You keep IBM i and your applications; the provider handles hardware, upgrades, monitoring and backup.
ibm/SEIMless delivers IBM i Series, PureFlex and AS/400 migrations into hosted environments designed to simplify deployment and reduce hardware and operational costs. If you are weighing hosted versus colocated models, our guide to choosing the right hosting and co-location solution walks through the decision.
Option 4: Re-Platform or Refactor RPG
IBM defines RPG modernization as updating aging midrange business software so it can connect to modern systems and outlast a shrinking pool of programmers. Common techniques include converting fixed-format RPG to free-form, replacing legacy file definitions with SQL, wrapping business logic as APIs, and replacing green screens with web interfaces. IBM also points to AI coding assistance for explaining, converting and testing RPG.
Full re-platforming off IBM i, for example rewriting onto a new ERP or a cloud-native stack on Microsoft Azure or Amazon Web Services, is the highest-effort option. Before you commit, run a structured comparison like the one in our post on evaluating ERP systems in a live business case.
IBM i Modernization Cost and Risk Comparison
This qualitative comparison is a starting framework, not a quote; actual costs vary by core count, licensing, storage and HA design.
| Factor |
On-prem refresh |
Power Virtual Server |
Managed hosting / colocation |
Refactor or re-platform |
| Upfront cost |
High (capital purchase) |
Low |
Low to moderate |
Moderate to very high |
| Ongoing cost model |
Maintenance plus staff |
Consumption-based |
Predictable monthly fee |
Depends on target platform |
| Application change |
None |
Minimal |
Minimal |
Significant |
| Skills dependency |
High internal |
Moderate internal |
Shared with provider |
New skills required |
| Migration risk |
Low |
Moderate |
Low to moderate |
High |
| Time to value |
Weeks to months |
Weeks to months |
Weeks to months |
Months to years |
| HA/DR options |
Self-built |
Cloud-based DR |
Provider-managed replication |
Rebuilt on new platform |
| Best fit |
Large, stable teams |
Cloud-first strategies |
Mid-sized, lean IT teams |
Apps that no longer fit |
Many IBM i modernization programs blend options: hosted production, cloud DR and gradual refactoring of critical RPG modules.
High Availability and Disaster Recovery for IBM i
IBM i modernization is the ideal time to fix resilience gaps. A new platform with the same weak recovery plan simply moves the risk.
Replication Approaches
IBM i offers several proven approaches to IBM i high availability:
- Logical replication: software-based, journal-driven replication of objects and data to a target system.
- Hardware and storage replication: PowerHA SystemMirror for i uses independent auxiliary storage pools with geographic or storage-based mirroring.
- Continuous availability: IBM Db2 Mirror for i synchronously mirrors database updates between two nodes, which IBM describes as delivering a recovery time objective of zero.
ibm/SEIMless provides IBM i Series high availability through SafeData/HA, which replicates your data in real time to a secure off-site data center and can become your production environment during an emergency or planned upgrade. We complement that with backup and recovery services for point-in-time restore.
Build DR Around Recognized Standards
Use NIST SP 800-34, the Contingency Planning Guide, to define RTO, RPO, test schedules and roles. Then map your plan against the CISA #StopRansomware Guide, which recommends maintaining offline, encrypted backups and regularly testing restoration. Replication alone is not a backup: ransomware replicates as fast as good data.
Security Hardening for Modernized IBM i
IBM i is highly securable, but many environments still run legacy system values, over-privileged profiles and open network servers. Hardening belongs in every IBM i modernization plan.
Lock Down the Network Doors
ODBC, FTP, DDM and remote command servers open paths into IBM i. IBM documents how to use security exit programs to monitor and control access through these exit points. Pair exit point controls with network segmentation and next-generation firewalls.
Add Multi-Factor Authentication
IBM i 7.6 introduces IBM i integrated MFA using time-based one-time passwords with no additional software required. Align your authenticator choices with NIST SP 800-63B-4 and prioritize privileged and remote access first.
Encrypt Data at Rest and in Motion
IBM i 7.6 adds ASP 1 encryption, and NIST finalized its first three post-quantum encryption standards in August 2024. Long-lived financial, insurance and health records are prime targets for harvest-now, decrypt-later attacks.
ibm/SEIMless helps protect those records with Exodus quantum-resistant data at rest encryption, built to work with existing storage systems, and quantum-resistant data in motion for replication and user traffic. For the bigger picture, see our post-quantum cryptography migration playbook.
Why It Matters Financially
IBM’s 2026 Cost of a Data Breach research puts the global average breach cost at a record USD 4.99 million, up 12% year over year. The FBI’s 2025 Internet Crime Report recorded more than 1 million complaints and nearly $21 billion in reported losses.
Step-by-Step IBM i Modernization Roadmap
Use this phased IBM i modernization roadmap to turn strategy into action. Frame it with the Govern, Identify, Protect, Detect, Respond and Recover functions of the NIST Cybersecurity Framework 2.0 so security is part of every phase.
- Inventory everything. Catalog LPARs, OS releases, PTF levels, licensed programs, third-party software, integrations, batch jobs and data volumes.
- Map the business. Identify which applications support revenue, compliance and customer-facing processes, and set RTO and RPO targets for each.
- Assess skills and succession. Document who knows what, which programs lack documentation and where you rely on a single person.
- Check support and compatibility. Confirm vendor support for IBM i 7.5 or 7.6 and Power10 or Power11 before choosing a target.
- Choose the platform. Compare on-premises, Power Virtual Server and hosted options using the table above and a three-to-five-year total cost of ownership.
- Design HA, DR and security first. Define replication, backup immutability, MFA, exit point policies and encryption before migration day.
- Pilot and test. Migrate a non-production partition, run parallel processing and test failover and restore.
- Cut over in waves. Move production during planned windows with documented rollback steps.
- Modernize the code incrementally. Refactor high-value RPG modules, expose APIs and replace green screens where users benefit most.
- Operate and improve. Monitor, patch, test DR at least annually and revisit the roadmap every year.
You can extend this roadmap across your enterprise IT infrastructure services, including private and hybrid cloud and infrastructure as a service. If your team is stretched, managed IT services can absorb day-to-day operations so your experts focus on the business.
Common AS/400 Modernization Mistakes to Avoid
AS/400 modernization projects stumble in predictable ways:
- Treating the move as a hardware swap and ignoring integrations, EDI and batch schedules.
- Replicating to a DR site without ever testing a full failover.
- Leaving default system values and powerful profiles unchanged after migration.
- Rewriting stable code instead of refactoring the modules that block growth.
- Waiting for a key employee to retire before documenting their knowledge.
Frequently Asked Questions
What is the difference between IBM i and AS/400?
AS/400 was the original 1988 name of IBM’s midrange system. The platform later became iSeries and System i, and today the operating system is called IBM i running on IBM Power servers. Many people still say AS/400 out of habit, but modern IBM i supports SQL, open-source languages, web services and current security features such as integrated MFA in IBM i 7.6.
When does IBM i 7.4 support end?
IBM lists September 30, 2026 as the end of standard support for IBM i 7.4, with end of marketing on April 30, 2026. IBM also lists extended support through September 30, 2029. Organizations on 7.4 should plan an upgrade to IBM i 7.5 or 7.6, keeping in mind that IBM i 7.6 requires Power10 or Power11 hardware.
Can IBM i run in the cloud?
Yes. IBM Power Virtual Server in IBM Cloud supports IBM i, AIX and Linux on Power infrastructure. Managed hosting providers also offer dedicated or shared Power environments in secure data centers. Mainstream x86 clouds do not run IBM i natively, so moving to AWS or Azure usually means re-platforming the application or connecting to a Power-based environment.
Is IBM i modernization the same as replacing IBM i?
No. In most cases IBM i modernization keeps the platform and updates what surrounds it: hardware, OS release, HA/DR, security, user interfaces, APIs and RPG code. Replacing IBM i entirely is one option, but it carries the highest cost and risk. Many organizations get faster results by refactoring critical modules and moving infrastructure to a hosted or cloud model.
How long does an IBM i migration take?
Timelines depend on partitions, data volume, integrations and testing. A lift-and-shift to new Power hardware, a hosted environment or Power Virtual Server is often measured in weeks to months. Refactoring RPG applications or re-platforming to a new ERP typically runs months to years. A thorough inventory and pilot migration are the best ways to set a realistic schedule.
What is the best disaster recovery approach for IBM i?
The best approach combines replication for fast failover with immutable, offline backups for ransomware recovery. Options include logical replication, PowerHA SystemMirror for i and Db2 Mirror for i for continuous availability. Define recovery time and recovery point objectives first, then test full failover and restore at least annually, following NIST SP 800-34 contingency planning guidance.
Talk to ibm/SEIMless About Your IBM i Modernization Plan
For more than 20 years, ibm/SEIMless has helped financial services, insurance and healthcare enterprises migrate, protect and run the systems their customers depend on. Whether you face the IBM i 7.4 deadline, a Power11 refresh or a move to hosted IBM i with real-time replication, our vendor-agnostic team will help you choose the IBM i modernization path that fits your people, budget and risk profile.
Get Started with a no-pressure IBM i assessment, or Contact Us to speak with a specialist today.
- Phone: 646-546-5245
- Email: in**@**********ss.com
- Address: One Liberty Plaza, New York, NY 10006
by hannahadmin | Sep 28, 2026 | blog, cybersecurity
Immutable backups have become the control that separates a bad week from a business-ending ransomware event. Modern attackers no longer stop at encrypting production servers. They hunt for backup consoles, delete snapshots and poison recovery points first, so that when the ransom note appears, the victim has nowhere left to turn.
The Verizon 2026 Data Breach Investigations Report finds ransomware in 48% of all breaches, with 31% of breaches starting from an exploited software vulnerability. A year earlier, Verizon found ransomware in 44% of breaches and 88% of breaches at small and midsize businesses. For leaders in financial services, healthcare and insurance, the question is no longer whether you will be hit, but whether you can restore clean data quickly and prove it to regulators.
This guide covers why attackers target backups, the 3-2-1-1-0 rule, cloud immutability controls, 2026 regulatory expectations and a recovery-readiness checklist you can use this quarter.
| What are immutable backups? Immutable backups are copies of data written in a write-once, read-many (WORM) state that cannot be changed, encrypted or deleted by anyone, including administrators, until a set retention period expires. Paired with isolation and tested restores, they give organizations a trusted, clean recovery point after ransomware or destructive attacks. |
| KEY TAKEAWAYS
■ Ransomware operators deliberately target backups, so any copy reachable with stolen admin credentials is not a true recovery point.
■ The 3-2-1-1-0 rule adds one immutable or offline copy and zero restore errors to the classic 3-2-1 rule.
■ Immutability protects data, but isolated recovery environments, phishing-resistant MFA and restore testing determine how fast you recover.
■ NYDFS Part 500, HIPAA, FFIEC guidance and SEC disclosure rules all expect protected, tested backups.
■ Quantum-resistant encryption protects long-retention backups against “harvest now, decrypt later” risk. |
Why Attackers Target Backups First
Ransomware is an extortion business, and backups are the biggest threat to its revenue. If a victim can restore, it does not need to pay. The CISA #StopRansomware Guide warns that “many ransomware variants attempt to find and subsequently delete or encrypt accessible backups.”
Recovery capability is paying off. Verizon’s 2025 report found 64% of ransomware victims did not pay, and the 2026 edition reports that share rose to 69%.
The modern attack chain against recovery
- Initial access through a stolen credential or an unpatched edge device.
- Privilege escalation to domain admin or cloud root.
- Reconnaissance of backup servers, hypervisor snapshots and cloud storage accounts.
- Destruction of recovery points by deleting snapshots or shortening retention.
- Data theft and encryption of production, followed by double extortion.
We documented this pattern in our analysis of how Interlock ransomware exploited a Cisco FMC zero-day for root access. In the joint #StopRansomware advisory on Interlock, CISA and the FBI recommend ensuring “all backup data is encrypted, immutable (i.e., cannot be altered or deleted), and covers the entire organization’s data infrastructure.”
What the 2025 FBI data shows
The FBI IC3 2025 Internet Crime Report logged $20.877 billion in reported losses, 3,611 ransomware complaints and 63 new ransomware variants, led by Akira and Qilin. Critical manufacturing, healthcare and government facilities were most affected. The FBI notes ransomware losses exclude “lost business, time, wages, files, or equipment,” so downtime is usually the largest cost, as our coverage of the Asahi cyberattack and nationwide shortages shows.
The 3-2-1-1-0 Rule for Immutable Backups
CISA’s backup guidance for businesses describes the 3-2-1 rule: three copies of important files, on two types of storage media, with one copy off-site. It was designed for hardware failure and disasters, not adversaries holding admin credentials. The industry has extended it:
- 3 copies of your data, including production.
- 2 different media or platforms, such as on-premises disk and cloud object storage.
- 1 copy off-site, in a separate facility or cloud region.
- 1 copy immutable or offline, meaning WORM-locked, logically air-gapped or disconnected.
- 0 errors after automated restore verification.
Those last two numbers turn ordinary copies into immutable backups you can bet the business on. CISA also advises ensuring you can “roll back data at least seven days if needed,” which demands adequate retention.
How Immutability Works: WORM, Object Lock and Immutable Vaults
Immutability must be enforced by the storage platform, not by backup software’s good intentions.
AWS
Amazon S3 Object Lock uses a WORM model. In compliance mode, no user, including root, can delete a protected object until retention expires; governance mode can be bypassed by privileged users. The AWS Backup logically air-gapped vault stores backups locked by default and shareable to a separate recovery account. Our Amazon Web Services team can help design these controls.
Microsoft Azure
Immutable storage for Azure Blob Storage supports time-based retention and legal holds, and locked policies meet SEC Rule 17a-4(f). The Azure Backup immutable vault blocks deletion of recovery points and retention reductions and can be locked irreversibly. See our Microsoft Azure services and our post on Azure as an enterprise cloud built for security.
Google Cloud
Google’s ransomware best practices for Backup and DR recommend vaults with enforced minimum retention, a hub-and-spoke project model separating backups from production, and separated admin roles. Explore our Google Cloud services.
A caution on “immutable” marketing
CISA cautions that immutable storage “does not meet compliance criteria for certain regulations and misconfiguration can impose significant cost.” Bypassable governance locks and short retention create false confidence. NIST SP 800-209 offers guidance for hardening the storage layer itself.
Isolated Recovery Environments and Air-Gapped Vaults
Immutability protects data from deletion, but it does not give you a clean place to restore. If identity, hypervisors and the network are still compromised, restoring simply re-infects the business.
An isolated recovery environment adds a separate control plane with its own credentials, network isolation from production, and a staging area where restored systems are scanned before release. CISA’s Interlock advisory calls for copies “in a physically separate, segmented, and secure location,” and its guide recommends “golden images” of critical systems for rapid rebuilds.
Traditional backup vs. immutable backups vs. isolated recovery vault
| Capability |
Traditional backup |
Immutable backups |
Isolated recovery vault |
| Protects against hardware failure |
Yes |
Yes |
Yes |
| Resists deletion by a compromised admin |
No |
Yes, during retention |
Yes, plus separate credentials |
| Resists encryption by ransomware |
Rarely |
Yes |
Yes |
| Separate identity and control plane |
No |
Usually not |
Yes |
| Clean staging for malware scanning |
No |
No |
Yes |
| Recovery speed after ransomware |
Slow and uncertain |
Moderate |
Fastest trusted restore |
| Cost and complexity |
Low |
Moderate |
Higher |
| Best fit |
Non-critical data |
Most enterprise workloads |
Tier-0 and regulated systems |
Most organizations need a tiered design: immutable backups for broad coverage and an isolated vault for identity, core banking, EHR and claims platforms. Our private and hybrid cloud services support recovery across environments, and our IBM i high availability service replicates IBM i workloads in real time to a secure off-site data center.
RPO, RTO and Proving Recovery with Restore Testing
Recovery point objective (RPO) is how much data you can afford to lose; recovery time objective (RTO) is how long a service can be down. Business owners, not IT alone, should set both.
The NIST Cybersecurity Framework 2.0 makes testing explicit. Subcategory PR.DS-11 states “Backups of data are created, protected, maintained, and tested,” and the Recover function requires that backup integrity be “verified before using them for restoration” (RC.RP-03), per the CSF 2.0 core document. NIST’s practice guides SP 1800-25 and SP 1800-26 address protecting against and responding to ransomware, while NIST SP 800-34 Rev. 1 remains the contingency planning reference.
A practical restore-testing cadence
- Daily: automated verification that jobs completed and recovery points are readable.
- Monthly: file and database restores for a rotating sample of critical applications.
- Quarterly: full application restores into an isolated environment, timed against RTO.
- Annually: an exercise simulating total loss of identity and production, with executives involved.
Protecting Backup Consoles, Identities and Keys
Most backup compromises are identity compromises. An attacker signed in to your backup console or cloud account can shorten retention or delete vaults before immutability takes effect.
- Phishing-resistant MFA on every backup, hypervisor and cloud admin account; CISA calls phishing-resistant MFA “the gold standard for MFA.”
- Separate identities for backup administration, outside the production domain.
- Multi-person approval for destructive actions such as deleting vaults.
- Continuous monitoring for anomalous logins and mass deletions.
Our endpoint detection and response services and the Exodus ARIA ADR platform, which unifies SIEM, UEBA, NTA, EDR, threat intelligence, IDS and SOAR with 24/7 monitoring, help surface attacker activity before it reaches backups. See also our guide to choosing an endpoint detection system.
Encrypting Backups for Today and the Quantum Era
Backups concentrate your most sensitive data, making them targets for theft as well as destruction. CISA recommends “offline, encrypted backups of critical data,” and HHS states that when ePHI is encrypted by ransomware, a breach has occurred unless a risk assessment shows low probability of compromise.
Long-retention backups carry a future risk too: data stolen today could be decrypted once cryptographically relevant quantum computers arrive. NIST finalized FIPS 203 (ML-KEM) for post-quantum key establishment, and CISA’s Post-Quantum Cryptography Initiative urges organizations to plan migration now. ibm/SEIMless delivers quantum resistant encryption for data at rest through Exodus QRN, detailed in Exodus QRN Data at Rest and our post on harvest now, decrypt later.
Regulations and Cyber Insurance: What Examiners Expect in 2026
NYDFS 23 NYCRR Part 500
Under New York’s Part 500 cybersecurity regulation, Section 500.16 (see the text at Cornell’s Legal Information Institute) requires backups “adequately protected from unauthorized alterations or destruction” and at least annual testing of the ability to restore from them. On November 1, 2025, expanded MFA and asset inventory requirements took effect, including recovery objectives for each asset.
HIPAA contingency plan
45 CFR 164.308(a)(7) requires a data backup plan maintaining “retrievable exact copies” of ePHI, a disaster recovery plan and emergency mode operations, with testing as an addressable specification. In April 2026, HHS OCR settled four ransomware investigations totaling $1,165,000.
FFIEC and SEC
Financial institutions are examined against the FFIEC Business Continuity Management booklet. Public companies must file Form 8-K Item 1.05 within four business days of determining an incident is material, per the SEC compliance guide. Fast, verifiable recovery simplifies that assessment.
Cyber insurance
The NAIC notes insurers “increasingly mandate robust cybersecurity controls and may impose limits on ransom coverage,” and the GAO reports insurers have tightened terms. Documented immutable backups, MFA and restore tests strengthen your underwriting position.
Recovery-Readiness Checklist for Immutable Backups
- Inventory critical applications with owners and approved RPO and RTO.
- Keep at least one copy of each critical dataset in immutable backups using compliance-mode or locked policies.
- Place tier-0 systems, including identity, in an isolated recovery vault with separate credentials.
- Set retention long enough to reach a clean point before attacker dwell time.
- Enforce phishing-resistant MFA and multi-person approval on backup and cloud admin accounts.
- Encrypt backups, manage keys separately and plan quantum-resistant protection for long-retention data.
- Maintain golden images to rebuild systems quickly.
- Automate restore verification and target zero errors.
- Run quarterly full restores into an isolated environment, timed against RTO.
- Map controls to NYDFS 500.16, HIPAA 164.308(a)(7), FFIEC and SEC workflows.
Budget alone does not deliver this, as we discussed in lessons from the UNFI breach, and resilience means avoiding single points of failure, a theme in how CIOs are rethinking cloud strategy after CrowdStrike.
How ibm/SEIMless Helps
For more than 20 years, ibm/SEIMless has been a vendor-agnostic technology partner. Our backup and recovery services, powered by Exodus-Data, include on-site, off-site, cloud and hybrid options, AES 256-bit encryption with key management, continuous data protection, restore validation and near-instant local and remote virtual disaster recovery. We pair them with multi-cloud expertise, managed detection and quantum-resistant encryption. Browse all ibm/SEIMless services.
Frequently Asked Questions
What is the difference between immutable backups and air-gapped backups?
Immutable backups cannot be modified or deleted until their retention period ends, enforced by WORM or object lock controls. Air-gapped backups are isolated from production networks, physically or logically, so attackers cannot reach them. The strongest designs combine both: immutable copies in an isolated vault with separate credentials, protecting against deletion, encryption and misuse of stolen administrator accounts.
Can ransomware encrypt or delete immutable backups?
Properly configured immutable backups in compliance mode or under locked policies cannot be altered or deleted during retention, even by administrators. Risk remains if immutability uses a bypassable governance mode, retention is too short, or attackers change policies before data is written. Protect backup consoles with phishing-resistant MFA and multi-person approval, and monitor for configuration changes.
What is the 3-2-1-1-0 backup rule?
The 3-2-1-1-0 rule means keeping three copies of data on two different media, with one copy off-site, one copy immutable or offline, and zero errors after restore verification. It extends the 3-2-1 rule that CISA recommends with protections built for ransomware, where attackers actively seek out and destroy accessible backups before encrypting production.
How often should we test backup restores?
Automate daily verification that backups completed and are readable, run monthly sample restores, and perform quarterly full-application restores into an isolated environment timed against your RTO. NYDFS Part 500 requires testing restoration from backups at least annually, and NIST CSF 2.0 expects backup integrity to be verified before use. Frequent testing builds real confidence.
Do regulations require immutable backups?
Most regulations do not name immutability, but they require outcomes it supports. NYDFS 500.16 requires backups protected from unauthorized alteration or destruction. HIPAA requires retrievable exact copies of ePHI and disaster recovery procedures. FFIEC examiners review recovery strategies and testing. Immutable backups are among the most practical ways to demonstrate these protections to auditors and examiners.
Why should backups use quantum-resistant encryption?
Backups often hold years of sensitive financial, health and customer data. Adversaries can steal encrypted copies today and attempt to decrypt them once quantum computers mature, a risk known as harvest now, decrypt later. Applying quantum-resistant encryption to long-retention data at rest reduces that exposure and aligns with NIST’s post-quantum standards and CISA’s migration guidance.
Talk to ibm/SEIMless About Ransomware-Ready Immutable Backups
Your backups are a promise to customers, patients and employees that the business will be there tomorrow. If you are not certain your recovery points are immutable, isolated and tested, find out before an attacker does. ibm/SEIMless and Exodus QRN can assess your backup and disaster recovery posture, map it to NYDFS, HIPAA, FFIEC and SEC expectations, and design recovery across on-premises, private cloud, AWS, Azure and Google Cloud.
by hannahadmin | Sep 26, 2026 | blog, cybersecurity
Immutable backups have become the control that separates a bad week from a business-ending ransomware event. Modern attackers no longer stop at encrypting production servers. They hunt for backup consoles, delete snapshots and poison recovery points first, so that when the ransom note appears, the victim has nowhere left to turn.
The Verizon 2026 Data Breach Investigations Report finds ransomware in 48% of all breaches, with 31% of breaches starting from an exploited software vulnerability. A year earlier, Verizon found ransomware in 44% of breaches and 88% of breaches at small and midsize businesses. For leaders in financial services, healthcare and insurance, the question is no longer whether you will be hit, but whether you can restore clean data quickly and prove it to regulators.
This guide covers why attackers target backups, the 3-2-1-1-0 rule, cloud immutability controls, 2026 regulatory expectations and a recovery-readiness checklist you can use this quarter.
| What are immutable backups? Immutable backups are copies of data written in a write-once, read-many (WORM) state that cannot be changed, encrypted or deleted by anyone, including administrators, until a set retention period expires. Paired with isolation and tested restores, they give organizations a trusted, clean recovery point after ransomware or destructive attacks. |
Why Attackers Target Backups First
Ransomware is an extortion business, and backups are the biggest threat to its revenue. If a victim can restore, it does not need to pay. The CISA #StopRansomware Guide warns that “many ransomware variants attempt to find and subsequently delete or encrypt accessible backups.”
Recovery capability is paying off. Verizon’s 2025 report found 64% of ransomware victims did not pay, and the 2026 edition reports that share rose to 69%.
The modern attack chain against recovery
- Initial access through a stolen credential or an unpatched edge device.
- Privilege escalation to domain admin or cloud root.
- Reconnaissance of backup servers, hypervisor snapshots and cloud storage accounts.
- Destruction of recovery points by deleting snapshots or shortening retention.
- Data theft and encryption of production, followed by double extortion.
We documented this pattern in our analysis of how Interlock ransomware exploited a Cisco FMC zero-day for root access. In the joint #StopRansomware advisory on Interlock, CISA and the FBI recommend ensuring “all backup data is encrypted, immutable (i.e., cannot be altered or deleted), and covers the entire organization’s data infrastructure.”
What the 2025 FBI data shows
The FBI IC3 2025 Internet Crime Report logged $20.877 billion in reported losses, 3,611 ransomware complaints and 63 new ransomware variants, led by Akira and Qilin. Critical manufacturing, healthcare and government facilities were most affected. The FBI notes ransomware losses exclude “lost business, time, wages, files, or equipment,” so downtime is usually the largest cost, as our coverage of the Asahi cyberattack and nationwide shortages shows.
The 3-2-1-1-0 Rule for Immutable Backups
CISA’s backup guidance for businesses describes the 3-2-1 rule: three copies of important files, on two types of storage media, with one copy off-site. It was designed for hardware failure and disasters, not adversaries holding admin credentials. The industry has extended it:
- 3 copies of your data, including production.
- 2 different media or platforms, such as on-premises disk and cloud object storage.
- 1 copy off-site, in a separate facility or cloud region.
- 1 copy immutable or offline, meaning WORM-locked, logically air-gapped or disconnected.
- 0 errors after automated restore verification.
Those last two numbers turn ordinary copies into immutable backups you can bet the business on. CISA also advises ensuring you can “roll back data at least seven days if needed,” which demands adequate retention.
How Immutability Works: WORM, Object Lock and Immutable Vaults
Immutability must be enforced by the storage platform, not by backup software’s good intentions.
AWS
Amazon S3 Object Lock uses a WORM model. In compliance mode, no user, including root, can delete a protected object until retention expires; governance mode can be bypassed by privileged users. The AWS Backup logically air-gapped vault stores backups locked by default and shareable to a separate recovery account. Our Amazon Web Services team can help design these controls.
Microsoft Azure
Immutable storage for Azure Blob Storage supports time-based retention and legal holds, and locked policies meet SEC Rule 17a-4(f). The Azure Backup immutable vault blocks deletion of recovery points and retention reductions and can be locked irreversibly. See our Microsoft Azure services and our post on Azure as an enterprise cloud built for security.
Google Cloud
Google’s ransomware best practices for Backup and DR recommend vaults with enforced minimum retention, a hub-and-spoke project model separating backups from production, and separated admin roles. Explore our Google Cloud services.
A caution on “immutable” marketing
CISA cautions that immutable storage “does not meet compliance criteria for certain regulations and misconfiguration can impose significant cost.” Bypassable governance locks and short retention create false confidence. NIST SP 800-209 offers guidance for hardening the storage layer itself.
Isolated Recovery Environments and Air-Gapped Vaults
Immutability protects data from deletion, but it does not give you a clean place to restore. If identity, hypervisors and the network are still compromised, restoring simply re-infects the business.
An isolated recovery environment adds a separate control plane with its own credentials, network isolation from production, and a staging area where restored systems are scanned before release. CISA’s Interlock advisory calls for copies “in a physically separate, segmented, and secure location,” and its guide recommends “golden images” of critical systems for rapid rebuilds.
Traditional backup vs. immutable backups vs. isolated recovery vault
| Capability |
Traditional backup |
Immutable backups |
Isolated recovery vault |
| Protects against hardware failure |
Yes |
Yes |
Yes |
| Resists deletion by a compromised admin |
No |
Yes, during retention |
Yes, plus separate credentials |
| Resists encryption by ransomware |
Rarely |
Yes |
Yes |
| Separate identity and control plane |
No |
Usually not |
Yes |
| Clean staging for malware scanning |
No |
No |
Yes |
| Recovery speed after ransomware |
Slow and uncertain |
Moderate |
Fastest trusted restore |
| Cost and complexity |
Low |
Moderate |
Higher |
| Best fit |
Non-critical data |
Most enterprise workloads |
Tier-0 and regulated systems |
Most organizations need a tiered design: immutable backups for broad coverage and an isolated vault for identity, core banking, EHR and claims platforms. Our private and hybrid cloud services support recovery across environments, and our IBM i high availability service replicates IBM i workloads in real time to a secure off-site data center.
RPO, RTO and Proving Recovery with Restore Testing
Recovery point objective (RPO) is how much data you can afford to lose; recovery time objective (RTO) is how long a service can be down. Business owners, not IT alone, should set both.
The NIST Cybersecurity Framework 2.0 makes testing explicit. Subcategory PR.DS-11 states “Backups of data are created, protected, maintained, and tested,” and the Recover function requires that backup integrity be “verified before using them for restoration” (RC.RP-03), per the CSF 2.0 core document. NIST’s practice guides SP 1800-25 and SP 1800-26 address protecting against and responding to ransomware, while NIST SP 800-34 Rev. 1 remains the contingency planning reference.
A practical restore-testing cadence
- Daily: automated verification that jobs completed and recovery points are readable.
- Monthly: file and database restores for a rotating sample of critical applications.
- Quarterly: full application restores into an isolated environment, timed against RTO.
- Annually: an exercise simulating total loss of identity and production, with executives involved.
Protecting Backup Consoles, Identities and Keys
Most backup compromises are identity compromises. An attacker signed in to your backup console or cloud account can shorten retention or delete vaults before immutability takes effect.
- Phishing-resistant MFA on every backup, hypervisor and cloud admin account; CISA calls phishing-resistant MFA “the gold standard for MFA.”
- Separate identities for backup administration, outside the production domain.
- Multi-person approval for destructive actions such as deleting vaults.
- Continuous monitoring for anomalous logins and mass deletions.
Our endpoint detection and response services and the Exodus ARIA ADR platform, which unifies SIEM, UEBA, NTA, EDR, threat intelligence, IDS and SOAR with 24/7 monitoring, help surface attacker activity before it reaches backups. See also our guide to choosing an endpoint detection system.
Encrypting Backups for Today and the Quantum Era
Backups concentrate your most sensitive data, making them targets for theft as well as destruction. CISA recommends “offline, encrypted backups of critical data,” and HHS states that when ePHI is encrypted by ransomware, a breach has occurred unless a risk assessment shows low probability of compromise.
Long-retention backups carry a future risk too: data stolen today could be decrypted once cryptographically relevant quantum computers arrive. NIST finalized FIPS 203 (ML-KEM) for post-quantum key establishment, and CISA’s Post-Quantum Cryptography Initiative urges organizations to plan migration now. ibm/SEIMless delivers quantum resistant encryption for data at rest through Exodus QRN, detailed in Exodus QRN Data at Rest and our post on harvest now, decrypt later.
Regulations and Cyber Insurance: What Examiners Expect in 2026
NYDFS 23 NYCRR Part 500
Under New York’s Part 500 cybersecurity regulation, Section 500.16 (see the text at Cornell’s Legal Information Institute) requires backups “adequately protected from unauthorized alterations or destruction” and at least annual testing of the ability to restore from them. On November 1, 2025, expanded MFA and asset inventory requirements took effect, including recovery objectives for each asset.
HIPAA contingency plan
45 CFR 164.308(a)(7) requires a data backup plan maintaining “retrievable exact copies” of ePHI, a disaster recovery plan and emergency mode operations, with testing as an addressable specification. In April 2026, HHS OCR settled four ransomware investigations totaling $1,165,000.
FFIEC and SEC
Financial institutions are examined against the FFIEC Business Continuity Management booklet. Public companies must file Form 8-K Item 1.05 within four business days of determining an incident is material, per the SEC compliance guide. Fast, verifiable recovery simplifies that assessment.
Cyber insurance
The NAIC notes insurers “increasingly mandate robust cybersecurity controls and may impose limits on ransom coverage,” and the GAO reports insurers have tightened terms. Documented immutable backups, MFA and restore tests strengthen your underwriting position.
Recovery-Readiness Checklist for Immutable Backups
- Inventory critical applications with owners and approved RPO and RTO.
- Keep at least one copy of each critical dataset in immutable backups using compliance-mode or locked policies.
- Place tier-0 systems, including identity, in an isolated recovery vault with separate credentials.
- Set retention long enough to reach a clean point before attacker dwell time.
- Enforce phishing-resistant MFA and multi-person approval on backup and cloud admin accounts.
- Encrypt backups, manage keys separately and plan quantum-resistant protection for long-retention data.
- Maintain golden images to rebuild systems quickly.
- Automate restore verification and target zero errors.
- Run quarterly full restores into an isolated environment, timed against RTO.
- Map controls to NYDFS 500.16, HIPAA 164.308(a)(7), FFIEC and SEC workflows.
Budget alone does not deliver this, as we discussed in lessons from the UNFI breach, and resilience means avoiding single points of failure, a theme in how CIOs are rethinking cloud strategy after CrowdStrike.
How ibm/SEIMless Helps
For more than 20 years, ibm/SEIMless has been a vendor-agnostic technology partner. Our backup and recovery services, powered by Exodus-Data, include on-site, off-site, cloud and hybrid options, AES 256-bit encryption with key management, continuous data protection, restore validation and near-instant local and remote virtual disaster recovery. We pair them with multi-cloud expertise, managed detection and quantum-resistant encryption. Browse all ibm/SEIMless services.
Frequently Asked Questions
What is the difference between immutable backups and air-gapped backups?
Immutable backups cannot be modified or deleted until their retention period ends, enforced by WORM or object lock controls. Air-gapped backups are isolated from production networks, physically or logically, so attackers cannot reach them. The strongest designs combine both: immutable copies in an isolated vault with separate credentials, protecting against deletion, encryption and misuse of stolen administrator accounts.
Can ransomware encrypt or delete immutable backups?
Properly configured immutable backups in compliance mode or under locked policies cannot be altered or deleted during retention, even by administrators. Risk remains if immutability uses a bypassable governance mode, retention is too short, or attackers change policies before data is written. Protect backup consoles with phishing-resistant MFA and multi-person approval, and monitor for configuration changes.
What is the 3-2-1-1-0 backup rule?
The 3-2-1-1-0 rule means keeping three copies of data on two different media, with one copy off-site, one copy immutable or offline, and zero errors after restore verification. It extends the 3-2-1 rule that CISA recommends with protections built for ransomware, where attackers actively seek out and destroy accessible backups before encrypting production.
How often should we test backup restores?
Automate daily verification that backups completed and are readable, run monthly sample restores, and perform quarterly full-application restores into an isolated environment timed against your RTO. NYDFS Part 500 requires testing restoration from backups at least annually, and NIST CSF 2.0 expects backup integrity to be verified before use. Frequent testing builds real confidence.
Do regulations require immutable backups?
Most regulations do not name immutability, but they require outcomes it supports. NYDFS 500.16 requires backups protected from unauthorized alteration or destruction. HIPAA requires retrievable exact copies of ePHI and disaster recovery procedures. FFIEC examiners review recovery strategies and testing. Immutable backups are among the most practical ways to demonstrate these protections to auditors and examiners.
Why should backups use quantum-resistant encryption?
Backups often hold years of sensitive financial, health and customer data. Adversaries can steal encrypted copies today and attempt to decrypt them once quantum computers mature, a risk known as harvest now, decrypt later. Applying quantum-resistant encryption to long-retention data at rest reduces that exposure and aligns with NIST’s post-quantum standards and CISA’s migration guidance.
Talk to ibm/SEIMless About Ransomware-Ready Immutable Backups
Your backups are a promise to customers, patients and employees that the business will be there tomorrow. If you are not certain your recovery points are immutable, isolated and tested, find out before an attacker does. ibm/SEIMless and Exodus QRN can assess your backup and disaster recovery posture, map it to NYDFS, HIPAA, FFIEC and SEC expectations, and design recovery across on-premises, private cloud, AWS, Azure and Google Cloud.