by hannahadmin | Sep 18, 2026 | Compliance, Exodus QRN, PQC, Quantum Security, Seimless
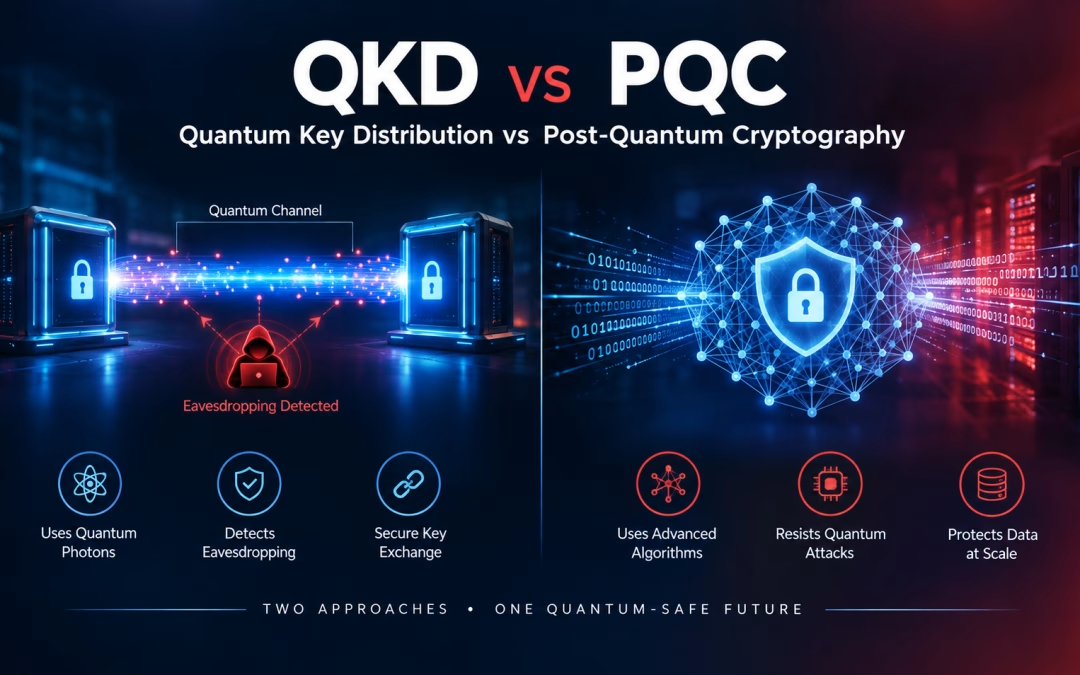
Every quantum-security conversation eventually reaches the same fork in the road: QKD vs PQC. Do you protect your network with quantum physics — quantum key distribution over dedicated fiber — or with new mathematics, the post-quantum cryptography algorithms NIST standardized in 2024? For years, vendors on both sides blurred the answer. In 2026, the U.S. government stopped blurring it. The National Security Agency, the Pentagon, and the Office of Management and Budget have all chosen post-quantum cryptography as the foundation of the federal migration, and the Pentagon has formally barred QKD as a security mechanism for its systems.
That doesn’t make quantum networking a dead end. The same White House that set the PQC deadlines is funding quantum networks for sensing, timing, and distributed computing. For CIOs and CISOs in financial services, healthcare, insurance, and the defense supply chain, the practical question is not which camp wins. It is what to build first, what to buy with confidence, and what to hold as an option. This guide answers the QKD vs PQC question the way regulators now expect you to answer it.
Quick answer — QKD vs PQC: Quantum key distribution (QKD) uses the physics of single photons to share encryption keys over a dedicated optical link and detect eavesdropping. Post-quantum cryptography (PQC) uses new math problems — such as NIST’s ML-KEM and ML-DSA — that run in software and hardware on existing networks and resist attack by quantum computers. U.S. policy treats PQC as the required foundation. QKD, where it is used at all, is a supplementary layer on specific links and never a substitute for PQC authentication.
QKD vs PQC in Plain Terms: Two Very Different Answers to Q-Day
Both technologies exist because of one threat. A cryptographically relevant quantum computer running Shor’s algorithm would break RSA and elliptic-curve cryptography, the public-key math that protects nearly every VPN, TLS session, and digital signature in use today. Adversaries already collect encrypted traffic to decrypt later, the harvest now, decrypt later strategy that makes this a present-day risk.
How quantum key distribution works
QKD sends key material encoded in the quantum states of photons. Because measuring a quantum state disturbs it, an eavesdropper on the line introduces detectable errors. The two endpoints compare samples, discard compromised bits, and keep a shared secret. The idea is elegant: security rests on physics rather than on an assumption that a math problem is hard. As the U.S. Department of Energy explains in its primer on quantum networks, these systems rely on superposition, no-cloning, and entanglement.
How post-quantum cryptography works
PQC replaces vulnerable algorithms with ones built on problems that neither classical nor quantum computers are known to solve efficiently. In August 2024, NIST finalized its first three PQC standards: FIPS 203 (ML-KEM) for key establishment, and FIPS 204 (ML-DSA) and FIPS 205 (SLH-DSA) for digital signatures. In March 2025, NIST selected HQC as a backup key-establishment algorithm based on different math. PQC is software and firmware. It runs over the fiber, MPLS, broadband, and wireless links you already own.
What the NSA Says About QKD — and Why It Matters to Every Buyer
The clearest statement in the QKD vs PQC debate comes from the NSA. Its public guidance on quantum key distribution and quantum cryptography says the agency does not recommend QKD for National Security Systems and does not anticipate certifying or approving QKD security products unless its limitations are overcome. The NSA lists five of them:
- A partial solution. QKD produces keys but does not authenticate who is on the other end. You still need classical or post-quantum signatures to prevent a man-in-the-middle.
- Special-purpose hardware. QKD requires dedicated fiber or free-space optical equipment. It cannot be delivered as a software update or a network service.
- Cost and insider risk. Distance limits force “trusted relays,” secured facilities where keys exist in the clear and insiders become part of the threat model.
- Hard to validate. Real-world security depends on engineering, not theory. Hardware flaws can open side channels the physics never anticipated.
- Denial of service. The same sensitivity that detects eavesdropping lets an attacker disrupt the link simply by disturbing it.
The NSA concludes that post-quantum cryptography is the more cost-effective and easily maintained solution. For regulated enterprises, that statement matters beyond defense. Banking, healthcare, and insurance examiners anchor their expectations to NIST and NSA guidance, so a security architecture that cannot be mapped to those references is harder to defend in an audit.
The Pentagon Drew a Hard Line on QKD vs PQC
Defense leadership has gone further than advice. A November 18, 2025 DoD CIO memorandum, Preparing for Migration to Post Quantum Cryptography, states that components shall not use quantum confidentiality technologies — naming QKD, solutions that combine QKD with other key establishment, and quantum communications or networking — as a means of achieving confidentiality, authentication, or key distribution.
The Department of War then made the position permanent in its Post-Quantum Cryptography Strategy, announced in a June 23, 2026 release. The strategy repeats that QKD and quantum networking will not be used to achieve security, and adds a line every vendor should read twice: solutions that lack PQC authentication — migrating confidentiality only — will not be considered fully PQC. Its deadlines are blunt. All systems must support PQC by December 31, 2030 or be phased out, and all systems must use PQC by December 31, 2031. DefenseScoop reported that the strategy describes insecure communications in a quantum era as an “existential threat” to military operations.
If you sell to the defense industrial base, this is not an abstract debate. QKD does not count toward your PQC obligations, and a QKD-first architecture could be one you have to re-engineer.
OMB M-26-15 and Executive Order 14412: The Civilian Clock Is Running
On the civilian side, Executive Order 14412, signed June 22, 2026, set the federal PQC calendar we analyzed in our Executive Order 14412 deadline guide. Two days later, OMB issued Memorandum M-26-15, Execution of the Migration to Post-Quantum Cryptography. It gives agencies 120 days — roughly October 22, 2026 — to submit PQC migration plans, calls for TLS 1.3 support by January 2, 2030, and targets completion of prioritized migrations by December 31, 2030.
Notice what the memo does not contain: any reference to quantum key distribution. The execution guidance is built entirely on NIST’s lattice-based and hash-based algorithms. The joint CISA, NSA, and NIST quantum-readiness factsheet takes the same path, focusing on inventory, vendor engagement, and PQC roadmaps. For federal contractors and the regulated industries that follow federal guidance, the QKD vs PQC decision has effectively been made for the compliance baseline.
Quantum Networking Isn’t Dead — Washington Is Funding It for Other Jobs
Here is the nuance most QKD vs PQC articles miss. The companion order, Executive Order 14413, Ushering in the Next Frontier of Quantum Innovation, directs agencies to prioritize research, testing, and evaluation of quantum sensing and quantum networking. Commerce is tasked with quantum-network-enhanced timing, Energy with networking for distributed quantum computing, and NASA with space applications.
The National Science Foundation describes the same direction in its June 2026 feature on quantum networks: linked sensors, GPS-free positioning, and pooled quantum processors, supported by regional test beds and quantum repeater research. So the federal message is consistent once you see it clearly. Quantum networks are a strategic technology for measurement and computation. For protecting data today, the government’s answer is post-quantum cryptography.
As FedTech Magazine’s 2026 federal QKD guide summarizes, CISA remains focused on the PQC migration and the DoD CIO’s post-quantum director has said QKD “does not meet our security requirements.” Infrastructure — dedicated links, endpoint hardware, and repeaters — remains the core obstacle for dispersed networks.
QKD vs PQC Side by Side: An Enterprise Comparison
| Factor |
Quantum Key Distribution (QKD) |
Post-Quantum Cryptography (PQC) |
| Security basis |
Physics of photons; security depends heavily on hardware engineering |
Math problems believed hard for quantum and classical computers |
| Authentication |
None on its own — needs signatures |
Built in (ML-DSA, SLH-DSA) |
| Infrastructure |
Dedicated fiber or free-space optics; trusted relays over distance |
Runs on existing networks, devices, and clouds |
| Standards status |
Not approved for NSS; barred as a security mechanism in DoD |
NIST FIPS 203, 204, 205 final; HQC in progress |
| Compliance credit |
Does not satisfy federal PQC mandates |
Required under EO 14412, M-26-15, and DoW strategy |
| Scale and cost |
Point-to-point; high cost per link |
Scales like software; cost driven by inventory and upgrades |
| Best fit today |
Research, specialized dedicated links, defense-in-depth where policy allows |
Every enterprise WAN, data center, cloud, and endpoint |
PQC has real costs too. Keys and signatures are larger — an ML-KEM-768 encapsulation key is 1,184 bytes versus 32 bytes for X25519 — which affects handshakes, constrained devices, and certificate chains. That is why crypto-agility, not a one-time swap, is the goal. Our certificate lifecycle management guide covers the operational side.
Where QKD Can Still Add Value — Honestly Scoped
The QKD vs PQC framing implies a winner-takes-all choice. It isn’t. Outside the Department of War’s systems and National Security Systems, an organization may choose to add physics-based key exchange as an extra layer — for example, between two owned data centers linked by dark fiber or wavelength services. Used this way, QKD is defense-in-depth on top of PQC, never a replacement for it.
Ask three questions before spending on it:
- Is PQC authentication already in place on this link? If not, fix that first. Keys without authenticated endpoints are an open door.
- Who controls the trusted nodes? Any relay where keys exist in the clear becomes a crown-jewel facility.
- What happens during an outage? If an attacker can force the link down, your failover path must be PQC-protected, not legacy RSA.
A PQC-First Roadmap for Financial, Healthcare, and Insurance Networks
For most enterprises, resolving QKD vs PQC comes down to sequencing. We recommend a five-step path aligned with the federal timeline and our post-quantum cryptography migration playbook:
- Inventory your cryptography. Identify every protocol, certificate, key, and library — including in medical devices, branch appliances, and third-party SaaS.
- Protect data in transit first. Harvest-now attacks target traffic, so start with quantum-resistant tunnels for data in motion across your WAN and SD-WAN, and plan the exit from legacy links through MPLS replacement.
- Centralize key management. Crypto-agility depends on knowing where keys live and rotating them on demand. Exodus Key Management provides centralized generation, distribution, storage, and rotation.
- Secure stored data. Long-retention records — loan files, patient histories, claims — need protection for data at rest and database-level transparent encryption.
- Evaluate QKD last, and only where policy permits. Treat it as an optional layer on specific dedicated links once PQC coverage is proven.
How Exodus QRN Resolves the QKD vs PQC Dilemma
ibm/SEIMless spent two decades as a vendor-agnostic integrator before becoming an OEM, and that history shapes how Exodus QRN approaches quantum security. The platform is built around crypto-agility — the memory, compute, and flexibility to add post-quantum algorithms as standards mature — with quantum random number generation for high-quality key entropy and centralized encryption and policy management across physical, virtual, and cloud environments.
Where a client has the dedicated optical infrastructure and a policy environment that allows it, quantum key distribution can be layered in. But our design principle mirrors federal guidance: post-quantum cryptography carries the compliance and authentication load, and nothing depends on QKD alone. Paired with the Exodus NxtGen Firewall and zero-trust content security, Exodus QRN protects today’s traffic while keeping your options open for tomorrow’s quantum networks. You can read more about the architecture in our Exodus QRN infrastructure overview.
We believe security is ultimately about people: patients whose records must stay private for decades, families whose savings depend on trusted banking rails, and teams who deserve infrastructure that won’t be obsolete before it is paid off. Choosing well now protects all of them.
QKD vs PQC: Frequently Asked Questions
What is the main difference in QKD vs PQC?
QKD uses the physics of photons to share keys over dedicated optical links. PQC uses new mathematical algorithms, standardized by NIST, that run on existing networks and devices and resist quantum attacks.
Does the NSA approve quantum key distribution?
No. The NSA does not recommend QKD for National Security Systems and does not anticipate certifying QKD security products unless its limitations — authentication, hardware, trusted relays, validation, and denial of service — are resolved.
Can the Department of War or its contractors use QKD for security?
Not as a security mechanism. The DoD CIO’s November 2025 memo and the 2026 DoW PQC Strategy state that QKD and quantum networking will not be used to achieve confidentiality, authentication, or key distribution.
Does QKD satisfy Executive Order 14412 or OMB M-26-15?
No. The federal migration is built on NIST PQC algorithms. OMB M-26-15 does not mention QKD, and agency migration plans are due about 120 days after June 24, 2026.
Is quantum key distribution completely obsolete?
No. Executive Order 14413 prioritizes quantum networking for sensing, timing, and distributed computing. Where policy allows, QKD can add defense-in-depth on dedicated links, but only on top of PQC.
Where should an enterprise start with post-quantum security?
Start with a cryptographic inventory, then protect data in transit with quantum-resistant networking, centralize key management, and secure long-retention data at rest. Evaluate QKD only after PQC coverage is in place.
Contact Us | Our Blog | Our Services | See Previous Post…
Related reading: The Impact of Quantum Computing on IPsec · IBM and Cisco’s Quantum Networking Partnership · Why Quantum-Resistant Networking Is a Business Necessity · All ibm/SEIMless insights
by hannahadmin | Sep 17, 2026 | blog, Quantum Security, Seimless, telecom, Zero Trust
Medical device cybersecurity has always been a race between patching and exposure. Now it has a second clock. The infusion pump, patient monitor, or imaging system a hospital buys this year may still be in clinical use in the late 2030s. By then, the RSA and elliptic-curve cryptography protecting it is scheduled to be retired. Healthcare leaders who plan only for today’s threats are buying devices that will fall short of tomorrow’s standards before they are fully paid off.
This guide explains the gap, what regulators already require, and how hospitals and manufacturers can close it. It starts from a simple belief we hold at ibm/SEIMless: protecting patient data is protecting people.
What is medical device cybersecurity? Medical device cybersecurity is the practice of protecting connected clinical devices, and the patient data and care they support, from unauthorized access, tampering, and disruption across the device’s full lifecycle, from design through retirement.
What is the cryptographic lifespan gap? The cryptographic lifespan gap is the number of years a device stays in clinical service after the encryption it relies on has been deprecated. For most connected devices bought in 2026, that gap is already more than zero.
Why Medical Device Cybersecurity Now Has a Quantum Deadline
In August 2024, NIST published its first three post-quantum standards: FIPS 203 (ML-KEM), FIPS 204 (ML-DSA), and FIPS 205 (SLH-DSA). In March 2025 it selected HQC as a backup encryption algorithm. Its draft transition plan, NIST IR 8547, proposes deprecating quantum-vulnerable algorithms after 2030 and disallowing them after 2035.
Federal policy has since set dates. Executive Order 14412, signed June 22, 2026, gives federal systems until December 31, 2030 to adopt post-quantum key establishment. We covered those milestones in our Executive Order 14412 deadline guide. The NSA’s CNSA 2.0 FAQ goes further on firmware. It urges signing systems to move first, because the code that checks a signature is often hard to update once a product ships.
That last point is the heart of the medical device cybersecurity problem. Enterprise laptops are replaced every few years. Clinical equipment is not.
The Cryptographic Lifespan Gap, Explained
Here is the arithmetic. A connected device bought in 2026 and kept for 10 to 15 years stays in service until 2036–2041. If the 2030 and 2035 dates in NIST’s draft hold, that device will spend years running cryptography that federal standards no longer accept.
| Device purchased |
Likely retirement |
Years past 2030 deprecation |
Years past 2035 disallowance |
| 2020 |
2030–2035 |
0–5 |
0 |
| 2026 |
2036–2041 |
6–11 |
1–6 |
| 2029 |
2039–2044 |
9–14 |
4–9 |
These ranges are illustrative, not a prediction for any single product. The pattern is the point: the later a hospital waits to demand post-quantum readiness, the wider the gap it signs up for.
An FDA-commissioned white paper from MITRE, Managing Legacy Medical Device Cybersecurity Risks, makes the same point. It warns that devices being purchased today can already meet the definition of a legacy device. It also notes a mismatch between how long hospitals keep equipment and how long manufacturers support it.
Why patient data makes “harvest now, decrypt later” worse
Attackers do not need a quantum computer today to benefit from one later. They can record encrypted traffic now and decrypt it once the math breaks. We explain the tactic in Harvest Now, Decrypt Later, and the underlying math in Shor’s algorithm explained.
Health data is an ideal target. A credit card can be canceled. A diagnosis, a genetic result, or a psychiatric history cannot. Data that stays sensitive for a patient’s lifetime needs protection that lasts just as long.
What the FDA Already Requires for Medical Device Cybersecurity
The FDA has steadily raised the bar. Since March 29, 2023, section 524B of the FD&C Act has required makers of “cyber devices” to include cybersecurity information in premarket submissions. The FDA’s cybersecurity FAQ defines a cyber device as one that includes sponsor-validated software, can connect to the internet, and could be vulnerable to cyber threats.
Manufacturers must now:
- Submit a plan to monitor, identify, and address postmarket vulnerabilities.
- Provide a software bill of materials (SBOM) covering commercial, open-source, and off-the-shelf components.
- Make updates and patches available to the device and related systems.
The FDA’s premarket guidance, Cybersecurity in Medical Devices: Quality Management System Considerations and Content of Premarket Submissions, was updated on February 3, 2026 to align with the new Quality Management System Regulation. It lists cryptography among its recommended security controls. It also names secure and timely updatability and patchability as a core security objective. The agency’s postmarket guidance adds that networked devices need continual maintenance for their entire life.
Where the rules stop
None of these documents sets a date for post-quantum algorithms in medical devices. And as the GAO noted in GAO-24-106683, the 524B requirements do not reach back to devices already on the market before March 2023 unless a maker files a new submission. That leaves the installed base, which is most of what hospitals actually run, outside the new rules.
The Legacy Fleet Hospitals Already Own
Healthcare delivery organizations inherit the gap whether they planned for it or not. The FBI warned in a 2022 private industry notification that unpatched and outdated medical devices give attackers openings into hospital networks. The Health Sector Coordinating Council’s Managing Legacy Technology Security (HIC-MaLTS) guide describes the same shared burden between makers and providers.
The risk is not theoretical. In January 2025, the FDA issued a safety communication on certain Contec and Epsimed patient monitors. It pointed to CISA advisory ICSMA-25-030-01, which described hidden functionality and patient data being sent outside the care environment. The FDA’s advice was to cut the monitors off from the internet.
When the fix for a device is “disconnect it,” the network becomes the only control left. That is exactly where post-quantum protection can be added without waiting for firmware.
The stakes are high. An analysis of 2025 OCR data counted 710 large healthcare breaches exposing more than 61.5 million people’s records. Every one is listed on the HHS OCR breach portal. We saw the downstream damage in the Change Healthcare hack.
Why Post-Quantum Cryptography Is Hard on Medical Devices
If swapping algorithms were easy, the gap would close on its own. Four constraints make it hard.
1. Bigger keys and signatures
Post-quantum keys and signatures are much larger than the ones they replace. Per the FIPS 203 and 204 parameter sets:
| Function |
Classical (today) |
Post-quantum (NIST) |
| Key exchange public key |
X25519: 32 bytes |
ML-KEM-768: 1,184 bytes |
| Digital signature |
ECDSA P-256: about 64 bytes |
ML-DSA-65: 3,309 bytes |
On a battery-powered wearable or a low-memory controller, those extra bytes cost power, bandwidth, and storage.
2. Firmware roots of trust
Many devices verify updates with a key burned into hardware. If that check only understands RSA or ECDSA, no software update can teach it a new algorithm. This is why CNSA 2.0 favors the stateful hash-based signatures in NIST SP 800-208 (LMS and XMSS) for firmware signing now.
3. Validation and re-submission
Changing cryptography can mean new testing under the Cryptographic Module Validation Program and, for some changes, a new FDA submission. Our look at certificate lifecycle management and the FIPS 140-2 sunset covers why validation queues matter.
4. Protocols built for another era
Clinical networks still carry older protocols, flat VLANs, and vendor remote-access tunnels. We examined similar weak points in quantum computing’s impact on IPsec and why SD-WAN is not ready for next-generation attacks.
Regulatory Pressure Beyond the FDA
Medical device cybersecurity sits inside a wider compliance picture for providers:
A Medical Device Cybersecurity Roadmap for Hospitals
Hospitals cannot rewrite vendor firmware. They can control what surrounds it. A practical sequence:
- Inventory every connected device and its cryptography. Record the protocol, algorithm, certificate, and end-of-support date. A cryptographic bill of materials (CBOM) turns this into a living record.
- Score each device by its lifespan gap. Rank devices by planned retirement date, data sensitivity, and whether their cryptography can be updated.
- Segment clinical networks. Put devices in tightly scoped zones with zero trust policies, so a compromised monitor cannot reach the EHR.
- Wrap device traffic in quantum-resistant tunnels. Protect the paths between clinical zones, data centers, clouds, and remote sites so recorded traffic stays safe.
- Centralize key management. Rotate and govern keys in one place, rather than on thousands of endpoints.
- Watch device behavior. Flag devices that suddenly talk to unknown destinations, as in the Contec case.
- Protect the data at rest. Encrypt and back up the imaging archives and clinical data that devices feed.
- Write post-quantum language into contracts. Make readiness a buying requirement, not a wish.
Six questions to ask every device manufacturer
- Which algorithms does the device use for key exchange, signing, and storage today?
- Can those algorithms be changed by a field update, or are they fixed in hardware?
- What is your published roadmap for ML-KEM, ML-DSA, or LMS/XMSS support?
- Will you provide a CBOM alongside the SBOM?
- What is the end-of-support date, and what happens to security updates after it?
- Does the device support hybrid classical plus post-quantum modes during the transition?
What Manufacturers Should Build Into the Next Submission
For device makers, medical device cybersecurity is now a design decision with a long tail. The strongest submissions will show:
- Crypto-agility by design. Algorithms isolated behind interfaces so they can be swapped without a hardware change.
- Quantum-safe roots of trust. LMS or XMSS firmware signing, with ML-DSA as validated modules fit the device.
- Hybrid key exchange. Classical plus ML-KEM during the transition, so security never drops below today’s level.
- Honest lifecycle dates. End-of-support timelines that match how long hospitals actually keep equipment.
- A CBOM next to the SBOM. Buyers increasingly need to see cryptography, not just components.
How ibm/SEIMless Helps Close the Medical Device Cybersecurity Gap
Our view is simple: the fastest way to protect devices you cannot change is to protect the network around them. That is the thinking behind our Exodus QRN quantum-resistant networking suite.
Because this protection runs at the network layer, it does not depend on a device maker shipping new firmware. Hospitals can start with their highest-risk paths this quarter, then extend coverage as budgets allow. For the full migration picture, see our post-quantum cryptography migration playbook and network edge security in 2026. For AI-driven clinical workflows, our analysis of blind agent transfer applies to healthcare just as much as finance.
Medical Device Cybersecurity FAQ
What is medical device cybersecurity?
Medical device cybersecurity is the protection of connected clinical devices, and the patient data and care they support, from unauthorized access, tampering, and disruption across the device’s full lifecycle, from design through retirement.
Does the FDA require post-quantum cryptography in medical devices?
Not by a specific date. Section 524B requires cybersecurity information, an SBOM, and a vulnerability plan for cyber devices, and FDA guidance recommends strong, updatable cryptography. It does not yet set a deadline for post-quantum algorithms.
What is the cryptographic lifespan gap?
It is the number of years a device stays in clinical use after the encryption it relies on has been deprecated. A device bought in 2026 and kept 10 to 15 years may run six or more years past NIST’s proposed 2030 deprecation date.
Can hospitals protect legacy medical devices that cannot be updated?
Yes, with compensating controls. Segmentation, zero trust policies, behavior monitoring, and quantum-resistant encryption of network paths protect device traffic without changing device firmware.
Why is health data a target for harvest-now, decrypt-later attacks?
Health information stays sensitive for a patient’s lifetime. Attackers can record encrypted traffic today and decrypt it once quantum computers can break RSA and elliptic-curve cryptography.
What should hospitals ask device manufacturers about quantum readiness?
Ask which algorithms the device uses, whether they can be updated in the field, the vendor’s roadmap for ML-KEM, ML-DSA, or LMS/XMSS, whether a CBOM is available, and the end-of-support date.
Protect Patients Before Q-Day Arrives
Every connected device in your hospital carries a patient’s trust. ibm/SEIMless and Exodus QRN help healthcare, financial, and insurance organizations close the medical device cybersecurity gap at the network layer, without waiting on firmware. Let’s map your highest-risk device paths together.
Contact Us | Our Blog | Our Services | See Previous Post
by hannahadmin | Aug 21, 2026 | blog, cybersecurity, QRN, Seimless, telecom, wide area networking
Agentic AI security has moved from a research topic to a boardroom line item in under twelve months. At the same time, the countdown to Q-Day keeps ticking. Most enterprises still treat these as two separate projects, run by two separate teams, on two separate budgets. That separation is the mistake. Autonomous attackers and quantum-vulnerable encryption are not parallel risks. They are the same risk, arriving from two directions, and they will meet inside your network.
At ibm/SEIMless, we have spent more than two decades helping firms build networks that survive the next threat rather than the last one. This guide explains what changed, why it matters now, and what a defensible roadmap looks like for 2026 and beyond.
What Agentic AI Security Actually Means in 2026
Traditional AI security focused on the model. Teams worried about prompt injection, hallucination, and data leakage inside a chat window. Agentic AI security is a different discipline entirely, because agents do not just answer. They act.
An agentic system plans, calls tools, writes and runs code, authenticates to APIs, and chains dozens of steps together without a human in the loop. So every credential the agent holds becomes an attack path. Every tool it can reach becomes a lateral movement option.
The OWASP GenAI Security Project published its Top 10 for Agentic Applications on 9 December 2025. The list reads less like an AI document and far more like a network security document. Agent identity spoofing, tool misuse, privilege compromise, and cascading multi-agent failures all appear. In other words, agentic AI security is network security wearing a new label.
That framing matters for one practical reason. If the risk lives in identity, credentials, and traffic, then the controls belong in your network architecture — not only in your AI governance policy. Our NxT-Gen Network Security Solutions practice was built on exactly that principle.
The First Documented AI-Orchestrated Campaign Changed the Conversation
For years, autonomous attack scenarios lived in threat modeling slide decks. Then they left the slide deck.
On 13 November 2025, Anthropic published its account of disrupting the first reported AI-orchestrated cyber espionage campaign. The operators, tracked as GTG-1002, manipulated an AI coding agent into running reconnaissance, vulnerability discovery, exploitation, and data exfiltration across roughly thirty target companies. Technology companies, financial institutions, chemical manufacturers, and government agencies all appeared on the target list.
The headline figure is the one that should reset your planning assumptions. The AI performed an estimated 80 to 90 percent of the campaign. Human operators intervened at only four to six critical decision points.
Congress noticed. The Congressional Research Service now maintains a standing brief titled “Agentic Artificial Intelligence and Cyberattacks,” most recently updated on 6 July 2026. Regulators, insurers, and auditors now read the same material your board reads.
Meanwhile, the pattern keeps repeating at smaller scale. Our coverage of the agentic AI security vulnerability exposed in ServiceNow, the malicious npm package that stole files from a Claude AI user directory, and the GlassWorm malware takedown all describe the same underlying shift. Attackers now automate the boring parts of intrusion, and the boring parts were the parts that used to give defenders time.
Why Speed Is the Real Weapon in Agentic AI Security
Autonomous tooling does not invent new exploits. Instead, it removes the human bottleneck. A campaign that once took a skilled team three weeks now takes an agent three hours.
Detection windows shrink accordingly. If your mean time to detect is measured in days, an agentic adversary has already finished. As a result, controls that depend on human triage speed are quietly obsolete, which is why we pair Exodus ARIA ADR with endpoint detection and response rather than relying on either alone.
Q-Day, Harvest Now Decrypt Later, and the Cryptographic Clock
Now consider the second front.
Q-Day describes the moment a cryptographically relevant quantum computer can break the RSA and elliptic-curve cryptography that protects almost every enterprise session today. The Cloud Security Alliance’s Q-Day Clock research places that moment as plausibly feasible around 2030.
However, the deadline that matters is not 2030. It is today. Adversaries already capture encrypted traffic and store it, waiting for the decryption capability to arrive. Security teams call this Harvest Now, Decrypt Later, and we covered the business impact in depth in Harvest Now, Decrypt Later.
Ask a simple question about your own data. How long does it need to stay secret? Patient records, financial contracts, engineering drawings, legal discovery, and government correspondence all carry secrecy lifetimes measured in decades. Therefore, anything you transmit today with classical encryption is already exposed to a decryption event ten years out.
The standards exist. NIST finalized FIPS 203, FIPS 204, and FIPS 205 on 13 August 2024, then selected HQC as a backup key encapsulation mechanism on 11 March 2025. You can read the current status directly on the NIST Post-Quantum Cryptography project page. For a plain-English explanation of the underlying mathematics, see our post on how quantum computers break encryption.
Adoption, by contrast, lags badly. The same Cloud Security Alliance research found that only about 5 percent of firms had deployed quantum-safe encryption as of May 2025.
Where Agentic AI Security and Quantum Risk Converge
Here is the thesis. These two threats do not simply coexist. They multiply.
Harvesting Becomes Cheap and Continuous
Harvest Now, Decrypt Later used to demand patient, well-resourced adversaries. Someone had to find valuable flows, set up collection, and hold access for years. Agentic tooling collapses that cost. An AI agent can map a network, spot long-lived sensitive flows, and stage theft around the clock.
In short, the pool of actors able to run a decade-long harvest just grew sharply. Our guidance on protecting data in motion and data at rest addresses both halves of that exposure.
Machine Identity Explodes the Key Estate
Every agent needs credentials. Those credentials depend on keys. Each key then becomes another item in a cryptographic inventory that most organizations cannot even enumerate today.
Most teams already struggle to track human identities. Now add thousands of non-human identities that spin up, authenticate, and disappear within minutes. So agentic AI security and post-quantum migration share one need: knowing where your keys are. That is precisely the problem Exodus Key Management exists to solve.
Crypto-Agility Stops Being Optional
Crypto-agility means you can swap algorithms without rebuilding applications. In the past, teams put it off, because algorithm changes came once a decade.
That assumption no longer holds. Between the NIST standards, NSA CNSA 2.0 requirements, and vendor timelines, most firms will change cryptographic primitives more than once before 2032. Moreover, AI-assisted code breaking may shorten those cycles further. A design that hard-codes one cipher has a shelf life.
Your Overlay Is Only as Strong as Its Handshake
Software-defined networking encrypts site-to-site traffic, and most teams consider that box ticked. Look closer, though. Many overlays still negotiate keys with classical Diffie-Hellman.
An attacker capturing that traffic today can decrypt it after Q-Day, no matter how modern the overlay looks. We examined this gap in Today’s Software-Defined Networks Are Not Future-Ready and in SD-WAN Not Ready for Next Generation Attacks. If you run SD-WAN or are evaluating MPLS replacement solutions, the handshake deserves an audit before the roadmap does.
Agentic AI Security Cuts Both Ways for Defenders
The picture is not one-sided. Autonomy cuts both ways, and defenders can automate correlation, triage, and containment just as effectively.
Modern networks already use machine learning to spot anomalies that no analyst would catch at three in the morning. We explored that shift in AI-Native Networks: The Future of Telecommunications and in How LLMs Will Improve Network Security. Furthermore, our piece on AI leading the next generation of defense covers the operational side of that argument.
The difference comes down to preparation. Attackers use autonomy when it suits them. Defenders must use it on purpose, with governance, logging, and clear escalation paths. Organizations that build that discipline into agentic AI security now will absorb the next wave far better than those retrofitting later.
What Executive Order 14412 Changes for Private Enterprises
On 22 June 2026, the White House signed Executive Order 14412, “Securing the Nation Against Advanced Cryptographic Attacks”. The order appeared in the Federal Register on 25 June 2026. A companion order, “Ushering in the Next Frontier of Quantum Innovation,” targets deployable quantum capability by 2028.
The federal timeline is now concrete:
- 30 days: every agency names a post-quantum cryptography migration lead.
- 90 days: OMB issues guidance covering High Value Asset inventories and transition plans.
- 180 days: NIST launches a migration pilot, and CISA publishes guidance on minimum cryptographic bill of materials elements.
- 270 days: the FAR Council proposes amended contractor disclosure rules.
- 31 December 2030: High Value Assets use post-quantum cryptography for key establishment.
- 31 December 2031: the same systems use post-quantum cryptography for digital signatures.
Three Ways the Order Reaches Private Networks
Private enterprises are not directly bound. Nevertheless, three mechanisms will pull you in anyway.
First, procurement. Federal contract language flows down to subcontractors and suppliers, and the FAR rulemaking makes that explicit. Second, the cryptographic bill of materials concept will become a standard due-diligence question, much as software bills of materials did. Third, insurers and auditors follow federal benchmarks when they define reasonable care.
CISA’s Post-Quantum Cryptography Initiative and the NSA’s CNSA 2.0 FAQ remain the clearest public statements of expectation. Notably, CNSA 2.0 pushes new national security system acquisitions toward quantum-resistant algorithms from January 2027. Our earlier reporting on U.S. lawmakers urging action on the quantum threat traced how this policy momentum built.
Industry is moving on its own schedule too. Cloudflare reports that more than two-thirds of browser traffic to its network already uses post-quantum encryption. The Quantum Insider’s August 2026 timeline survey shows Google and Cloudflare targeting 2029, Microsoft targeting 2033, and SWIFT planning a post-quantum SwiftNet release for 2027.
What the Convergence Means Sector by Sector
Risk is never evenly distributed. Your exposure depends on how long your data stays valuable and how quickly your operations must respond.
Healthcare. Patient records carry a legal and practical secrecy lifetime of decades. So healthcare providers sit at the very top of the Harvest Now, Decrypt Later risk list. Meanwhile, connected clinical devices give autonomous attackers an unusually soft internal surface.
Financial services. Transaction records, credit files, and contract archives all outlive current encryption. SWIFT plans a post-quantum SwiftNet release for 2027, so the migration pressure is already contractual rather than theoretical. Our analysis of why big cybersecurity budgets still fail explains why spending alone will not close this gap.
Manufacturing and supply chain. Engineering drawings and process data retain competitive value for twenty years or more. In addition, third-party exposure keeps growing, as the Ericsson service provider breach showed.
Government and public sector. Executive Order 14412 applies directly, and the flow-down reaches every supplier. Our reporting on the Pentagon’s supply-chain risk designation for an AI vendor shows how quickly AI procurement scrutiny is tightening.
Critical communications. Outages and intrusions compound each other. Recent incidents such as the AT&T 911 outage show how thin the safety margin has become for vital services.
A Seven-Step Roadmap for Agentic AI Security and Quantum Readiness
You do not need two programs. You need one program with two outputs. Here is the sequence we use with clients.
- Build a combined inventory. Catalog cryptographic assets and non-human identities in the same exercise. Both questions share one answer set. Where are the keys, who holds them, and what do they protect?
- Classify by secrecy lifetime. Rank data by how long it must stay confidential. Anything above ten years moves to the front of the queue immediately.
- Audit your handshakes. Check what your VPNs, overlays, and management planes actually negotiate. Marketing material and packet captures often disagree.
- Govern agents like privileged users. Give every agent a scoped identity, a short-lived key, and a full audit trail. Above all, remove standing access. Our work on zero trust content security applies directly here.
- Protect the two data states separately. Data in motion and data at rest fail differently, so plan them as distinct workstreams. Exodus Transparent Encryption and our EXODUS QRN data-at-rest guidance cover the second.
- Shorten detection to machine speed. Automated attacks require automated response. Human triage remains essential for judgement, yet it cannot be the first line.
- Rewrite procurement language now. Ask every vendor for post-quantum support, key inventories, and agent governance. This costs nothing today and saves enormous rework later.
For a deeper build sequence, see our companion pieces on post-quantum cryptography migration and enterprise IT infrastructure services.
How ibm/SEIMless Approaches Agentic AI Security and Quantum-Resistant Networking
We are vendor-agnostic by design. Since 2001, we have selected technology on fit rather than on partnership incentives, which matters more than ever now that every vendor claims quantum readiness.
Our Exodus Quantum-Resistant Networking portfolio addresses the cryptographic layer through key management, data in motion, data at rest, and edge enforcement through QR-Edge and Exodus PIET. On the detection side, Exodus NxtGen Firewall, Exodus ARIA ADR, and EDR close the response-time gap that agentic attackers exploit.
Underneath sits the transport itself. Whether you run Ethernet, MPLS, wavelength services, dark fiber, private line, or wireless, the encryption question follows the circuit. Our cloud services, Microsoft SaaS and DaaS, telecom services, and document management practices extend the same standard across the rest of the estate.
Frequently Asked Questions
Is agentic AI security different from traditional AI security?
Yes. Traditional AI security protects a model and its outputs. Agentic AI security protects an autonomous system that holds credentials, calls tools, and takes actions across your network, so the controls resemble identity and network security far more than content moderation.
Do we need to fix quantum risk before agentic AI risk?
Neither one waits for the other. Start both with the same inventory exercise, because the underlying question — where your keys and identities live — is identical for both programs.
Does Executive Order 14412 apply to private companies?
Not directly. However, its requirements reach private firms through federal procurement flow-downs, contractual due diligence, and the benchmarks that auditors and insurers adopt.
What is a realistic first ninety days?
Complete a cryptographic and non-human identity inventory, classify data by secrecy lifetime, audit your overlay handshakes, and update procurement language. Those four steps cost little and unlock everything that follows.
How does quantum-resistant networking differ from post-quantum cryptography?
Post-quantum cryptography describes the algorithms. Quantum-resistant networking describes the architecture that deploys, rotates, and governs those algorithms across live enterprise traffic.
The Bottom Line
Two clocks are running. One counts down to autonomous attackers operating faster than your response process. The other counts down to the day today’s captured traffic becomes readable. They are converging, and the organizations that treat them as one program will finish years ahead of those that do not.
Agentic AI security and quantum-resistant networking share the same foundation: know your keys, govern your identities, and build architecture you can change. Everything else is implementation detail.
Ready to start? Get started with ibm/SEIMless or contact our team for a cryptographic and agent-governance readiness assessment. You can also review our reports, browse our partners, read the FAQs, or explore distributor opportunities.
Complete ibm/SEIMless Resource Index
Quantum-Resistant Networking
NxT-Gen Network Security Solutions
Wide Area Networking and Connectivity
Cloud Services
Contact Us | Our Blog | Our Services | See Previous Post
by hannahadmin | Aug 11, 2026 | cybersecurity, QRN, Seimless, telecom
Every encrypted message your enterprise sends today could already be sitting in an adversary’s archive, waiting for the day a quantum computer can crack it open. That is the uncomfortable reality behind “harvest now, decrypt later,” and it is why post-quantum cryptography migration has moved from a research-lab curiosity to an urgent boardroom priority in 2026. For organizations that depend on telecom, cloud, PBX, and networked infrastructure, the question is no longer if you will migrate to quantum-resistant encryption — it is how fast and how safely you can do it.
At ibm/SEIMless, we help enterprises answer that question with confidence. This guide breaks down what post-quantum cryptography migration actually involves, why the deadlines are closer than most leaders realize, and the practical steps you can take now to protect your data, your customers, and your reputation.
What Is Post-Quantum Cryptography Migration?
Post-quantum cryptography (PQC) refers to a new generation of encryption algorithms designed to withstand attacks from both classical and quantum computers. Post-quantum cryptography migration is the structured process of replacing today’s vulnerable public-key algorithms — RSA, ECC, and Diffie-Hellman — with these quantum-resistant standards across every system that stores or transmits sensitive data.
The urgency comes from a simple mathematical truth. A sufficiently powerful quantum computer running Shor’s algorithm could break the public-key cryptography that secures virtually all modern digital communication — from VPN tunnels and TLS sessions to PBX signaling and cloud storage. In August 2024, the U.S. National Institute of Standards and Technology (NIST) released the first three finalized post-quantum encryption standards, formally opening the migration era for every enterprise on the planet.
The New Standards Driving Migration
The finalized standards give security teams a concrete target. Rather than waiting for perfect certainty, organizations now have federally vetted algorithms to build around:
- FIPS 203 (ML-KEM) — derived from CRYSTALS-Kyber, the primary standard for general encryption and key establishment. You can review the full FIPS 203 specification on the NIST CSRC portal.
- FIPS 204 (ML-DSA) — derived from CRYSTALS-Dilithium, the primary standard for digital signatures.
- FIPS 205 (SLH-DSA) — derived from SPHINCS+, a backup signature standard built on a different mathematical foundation for added resilience.
NIST’s ongoing work, documented on its Post-Quantum Cryptography Standardization project page, continues to evaluate additional algorithms to ensure cryptographic diversity. The message from NIST leadership has been unambiguous: begin integrating these standards immediately, because full integration takes years, not months.
Why “Harvest Now, Decrypt Later” Changes the Timeline
The single most misunderstood aspect of the quantum threat is timing. Many executives assume they can wait until a cryptographically relevant quantum computer exists before acting. That assumption is dangerous.
Adversaries are already capturing and storing encrypted traffic today — financial records, health data, intellectual property, government communications — with the intent of decrypting it once quantum capability matures. This is the “harvest now, decrypt later” (HNDL) attack model. Any data with a shelf life longer than the expected arrival of quantum computers is effectively at risk right now. For a hospital, a bank, or a defense contractor, that shelf life can stretch across decades.
This is precisely why federal guidance has accelerated. The Cybersecurity and Infrastructure Security Agency (CISA), together with the NSA and NIST, published a joint Quantum-Readiness: Migration to Post-Quantum Cryptography resource urging organizations to start now. Their companion factsheet on quantum readiness lays out the first concrete steps for critical-infrastructure operators.
The Regulatory Clock Is Already Ticking
Post-quantum cryptography migration is not just best practice — it is increasingly a compliance mandate.
The National Security Agency’s Commercial National Security Algorithm Suite 2.0 (CNSA 2.0) sets firm transition timelines for national security systems, with full adoption of quantum-resistant algorithms expected by 2035 and earlier milestones for software and firmware signing. In the legislative arena, the Quantum Computing Cybersecurity Preparedness Act — signed into law in December 2022 — requires federal agencies to inventory their cryptographic systems and prioritize migration, a standard that inevitably flows down to contractors and private-sector partners.
For hands-on implementation, the NIST National Cybersecurity Center of Excellence (NCCoE) maintains a dedicated Migration to Post-Quantum Cryptography project that offers reference architectures and playbooks. Broader national strategy and research coordination are tracked through the U.S. National Quantum Initiative at quantum.gov. Even industry bodies have weighed in: the Cloud Security Alliance’s analysis of the finalized FIPS 203, 204, and 205 standards frames the finalization as a defining moment for the quantum-safe future.
A Practical Post-Quantum Cryptography Migration Roadmap
Migration can feel overwhelming, but it becomes manageable when broken into disciplined phases. Here is the roadmap ibm/SEIMless uses to guide enterprises toward crypto-agility.
1. Build a Cryptographic Inventory
You cannot protect what you cannot see. Start by discovering every place cryptography lives in your environment — TLS certificates, VPNs, PBX signaling, database encryption, cloud APIs, IoT devices, and third-party integrations. This inventory becomes the master map for your entire migration.
2. Prioritize by Data Sensitivity and Longevity
Rank systems by the value and shelf life of the data they protect. Long-lived secrets — trade secrets, personal health information, legal records — move to the front of the line because they are the prime targets of harvest-now-decrypt-later campaigns.
3. Achieve Crypto-Agility
Crypto-agility is the ability to swap cryptographic algorithms without re-architecting your systems. Building this flexibility now means you can adopt new standards as they evolve, rather than facing a painful forklift upgrade with each change. Our quantum computing and encryption resources explain how crypto-agility fits into a modern security stack.
4. Protect Data in Motion and Data at Rest
A complete migration secures information wherever it lives. That means quantum-resistant protection for data in motion as it travels across your network, and for data at rest in storage and backups. Strong key management ties the two together and remains the backbone of any resilient encryption program.
5. Layer Quantum-Safe Networking with Zero Trust
Post-quantum algorithms are strongest when combined with a defense-in-depth architecture. Pairing PQC with a zero trust security model and a next-generation firewall ensures that even if one layer is challenged, your data stays protected. For distributed enterprises, quantum-safe SD-WAN extends this protection across every branch, remote worker, and cloud connection.
How ibm/SEIMless Makes Quantum-Safe Migration Seamless
Migrating an entire enterprise to post-quantum cryptography is a journey, and you should not walk it alone. ibm/SEIMless delivers end-to-end Quantum Resistant Networking built on the same NIST-aligned standards driving federal migration — combined with the telecom, cloud, and PBX expertise your operations already rely on.
Because we integrate quantum-safe encryption directly into your networking, cloud infrastructure, and voice communications, you gain protection without the complexity of stitching together a dozen vendors. Our approach is grounded in a simple conviction: the technology that protects an organization’s data is ultimately protecting the people who trust that organization. Security done right is a form of care.
Explore our full range of managed security and networking services, or learn more about who we are and why enterprises across the country choose us as their quantum-safe partner.
The Cost of Waiting Far Outweighs the Cost of Acting
Post-quantum cryptography migration is the defining cybersecurity project of this decade. The standards are final, the federal timelines are set, and the harvest-now-decrypt-later threat is active today. Organizations that begin their migration now will move deliberately, protect their most valuable data, and meet compliance deadlines with room to spare. Those that wait risk a chaotic, expensive scramble — or worse, a breach of data they thought was safe years ago.
The future of secure networking is quantum-resistant, and it is being built right now.
Ready to Future-Proof Your Encryption?
Do not let your enterprise become a target of harvest-now-decrypt-later. The ibm/SEIMless team will help you inventory your cryptography, build a phased migration roadmap, and deploy quantum-resistant protection across your entire network. Get started with a quantum-readiness consultation today, or contact our specialists to secure your digital future — before someone else decides your timeline for you.
Contact Us | Our Blog | Our Services | See Previous Post…