AI Agent Traffic: What Amazon’s Block of Meta’s Muse Means for Enterprise Security
Over the weekend of September 20, 2026, Amazon shut Meta’s new Muse personal AI agent out of Amazon.com. Shoppers who asked Muse to buy something got a blunt message: continued access by an unauthorized AI agent violates Amazon’s Conditions of Use. Headlines framed it as a retail turf war. For security leaders, it is something bigger: the first high-profile, consumer-scale collision over AI agent traffic — and a preview of decisions every enterprise will have to make about the autonomous software now knocking on its digital front door.
This post breaks down what happened, why the courts won’t settle it for you, what the numbers say, and how financial services, healthcare, and insurance organizations can build an AI agent traffic policy that is enforced at the network — not just written in a terms-of-service page.
What is AI agent traffic? AI agent traffic is network and web activity generated by autonomous AI software acting on a person’s or organization’s behalf — logging in, browsing, filling forms, calling APIs, and completing transactions. Unlike classic crawlers, AI agents often use real user credentials and mimic human browsing, which makes them hard to tell apart from people or attackers unless they identify themselves cryptographically.
What Happened: Amazon vs. Meta’s Muse, in Brief
Meta introduced Muse in September 2026 as a personal agent that “takes action”: it can open browsers, fill forms, send email with approval, and make purchases through Stripe Link. TechCrunch covered the debut on September 8. Within two weeks, GeekWire reported that Amazon had blocked it after first asking Meta to remove Amazon from the experience voluntarily.
Amazon’s stated objections are the ones security teams should notice:
- No self-identification. Amazon says Muse accessed the store without identifying itself as an agent or reaching any prior agreement.
- Credential custody. Amazon says the agent captures and stores customer credentials and, when instructed, can reach order history and other account data.
- Amazon’s position, as reported by TechCrunch, is that third-party apps that buy on a customer’s behalf “should operate openly.”
Meta’s side matters too. The company says Muse cannot see users’ passwords or payment methods; credentials sit in secure storage and are used for authentication without being exposed to the model. Meta also describes a dedicated secure VM, a separate “Sentinel” agent that approves internet-bound actions, and audit trails. Forbes and Bloomberg framed the standoff around commerce, and the money is real: Amazon’s advertising business depends on humans seeing sponsored placements, while Oppenheimer’s Jason Helfstein estimates Meta would need about 115 million subscribers at $20 a month to reach $28 billion in AI revenue — a target he doubts it will hit.
Both companies can be partly right. That is exactly the problem: when an AI agent shows up, the receiving system usually cannot verify either company’s claims in real time.
Why AI Agent Traffic Is a Security Story, Not Just a Retail Feud
Strip away the brands and you have three questions every CISO will face this year:
- Who is this? Is the session a human, a declared agent, a scraper, or an attacker using a stolen session token?
- On whose authority? Did the account holder actually delegate this action, and within what limits?
- Who holds the keys? Where do the credentials live, and what happens when that third-party vault is breached?
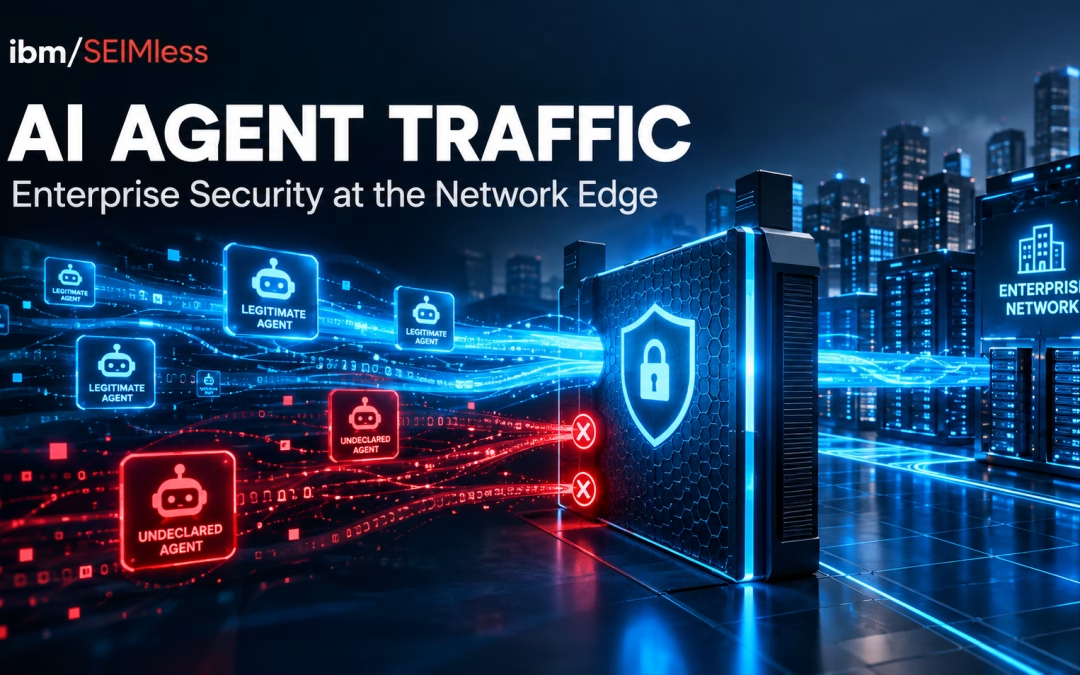
We call this the undeclared agent problem: software that uses a legitimate person’s identity but never announces that software, not a person, is at the keyboard. Undeclared AI agent traffic looks almost identical to account takeover (ATO). The same signals that flag fraud — a new device, headless browser fingerprints, machine-speed navigation — also flag helpful agents. Block too much and you break customer experience; block too little and you give attackers the perfect disguise.
We explored the inside-the-enterprise version of this in The Hidden Risk of AI-to-AI “Blind Agent Transfer”. The Muse episode is the outside-in version: agents arriving from someone else’s platform, carrying your customers’ credentials.
The Legal Backdrop: Why the Courts Won’t Manage AI Agent Traffic for You
Amazon has been here before. It sued Perplexity over the Comet browser’s shopping agent and won a preliminary injunction in March 2026. On August 4, 2026, the Ninth Circuit vacated that injunction. As Cooley’s analysis summarizes, the court held that when an agent’s communications route through the user’s own computer, it is the user — not the AI developer — who “accesses” the site under the Computer Fraud and Abuse Act.
The ruling builds on the Supreme Court’s narrowing of the CFAA in Van Buren v. United States (2021). It also left doors open: contract and tort claims survive, and agents that act more autonomously or talk directly to target servers could still face liability.
The practical takeaway for enterprises is simple. Anti-hacking law is a slow, uncertain backstop for AI agent traffic. Your terms of service state a policy. Your network and identity controls enforce it. Amazon didn’t wait for a court — it enforced at the edge.
AI Agent Traffic by the Numbers
The scale is no longer theoretical. The 2026 Thales (Imperva) Bad Bot Report, released April 29, 2026, found:
| Metric | Figure | Why it matters |
| Share of all web traffic that is automated | Over 53% | Humans are now the minority on the web |
| Growth in AI-driven bot attacks, year over year | 12.5x | Attackers are adopting agents faster than defenders |
| Bot attacks aimed at APIs | 27% | Agents skip the web page and go straight to the data |
| Share of bot attacks hitting financial services | 24% | Banking is the top target |
| Account takeover incidents targeting financial services | 46% | Credential-carrying traffic is the core risk |
Federal data tells the same story. The FBI’s 2025 IC3 Annual Report logged $20.877 billion in reported losses, including 22,364 AI-related complaints totaling $893.3 million. The FBI also issued a November 2025 account takeover fraud alert citing more than 5,100 complaints and over $262 million in losses in less than a year. When legitimate AI agent traffic and ATO traffic look the same, both numbers get harder to manage.
Two Directions of Risk: Inbound Agents and Outbound Agents
Inbound: agents at your front door
If you run a banking portal, a patient portal, a claims system, or a B2B ordering site, agents like Muse are coming whether you invite them or not. Customers will ask their assistant to “pay my premium,” “download my lab results,” or “dispute that charge.” Every one of those sessions is AI agent traffic using a real customer’s credentials.
Financial services has seen this movie. Screen scraping by data aggregators was supposed to give way to secure APIs under the CFPB’s Personal Financial Data Rights rule (Section 1033). That rule is now enjoined while the Bureau reconsiders it. In the meantime, agents are reviving the old pattern — credential-based access through the front end — at far larger scale.
Outbound: agents carrying your keys
The quieter risk is inside your own walls. An employee who connects a personal agent to a corporate mailbox, a SaaS admin console, or a vendor portal has just placed company credentials in a third-party vault you never assessed. That is shadow AI with a credit card attached. We have already seen attackers go after exactly these stores — see our coverage of a Python backdoor stealing browser and cloud credentials and fake résumés used for credential theft. A centralized agent credential store is an even richer target.
How to Identify AI Agent Traffic: From User-Agent Strings to Cryptographic Proof
User-agent strings and IP allowlists were never proof of identity; they are a label anyone can copy. The industry is moving toward cryptographic proof:
- Signed requests. IETF RFC 9421 (HTTP Message Signatures) lets a client sign each request. The Web Bot Auth draft applies it so an agent can prove which operator it belongs to.
- Agent identity and delegation. NIST’s National Cybersecurity Center of Excellence launched a Software and AI Agent Identity and Authorization project, anchored by a February 2026 concept paper on how agents should prove identity and scoped authority.
- Strong human authentication underneath. NIST SP 800-63-4 and CISA’s guidance on phishing-resistant MFA make it harder for any agent — honest or not — to replay a stolen password.
- Tool-layer controls. The NSA’s May 2026 guidance on Model Context Protocol security warns about implicit trust and context sharing between agents and tools.
The direction is clear: AI agent traffic should declare itself, prove its operator, and carry a scoped, revocable delegation from a human who authenticated strongly.
A 7-Step AI Agent Traffic Governance Framework
- Decide your policy in writing. Allow declared agents, allow them only through an API, or block them. Choose per system: a public catalog and a wire-transfer page deserve different answers.
- Inventory where agents already touch you. Use web logs, WAF data, and endpoint detection to find headless browsers, automation frameworks, and agent-hosting IP ranges.
- Offer a front door. Give legitimate agents an authenticated API with OAuth-style scoped tokens, so they have no reason to scrape your UI.
- Require proof, not labels. Favor signed requests (RFC 9421 / Web Bot Auth) and verified operator keys over user-agent strings.
- Bind agents to scope and step-up. Agents may read a balance; moving money, changing a payee, or releasing records requires human step-up authentication.
- Govern outbound agents. Ban unmanaged agents from holding corporate credentials; route approved ones through enterprise identity and Security as a Service
- Log for accountability. Record agent identity, delegating user, scope, and action in tamper-evident logs, mapped to the NIST AI Risk Management Framework, the OWASP GenAI Security Project, and MITRE ATLAS threat techniques.
Why the Network Layer Is Where AI Agent Traffic Gets Decided
Amazon’s block worked because it happened before the agent reached the storefront. That is the lesson: policy that isn’t enforced in the traffic path is only a suggestion. This is the core idea behind NIST SP 800-207 zero trust architecture — and our own primer, What Is Zero Trust? — where every request is evaluated on identity and context, every time.
At ibm/SEIMless, we build that enforcement into the network itself through the Exodus portfolio:
- Exodus NxtGen Firewall and Zero Trust Content Security to inspect, classify, and apply policy to agent sessions at the edge.
- Exodus Aria ADR to detect and respond when “helpful” automation starts behaving like an attack.
- Exodus QRN Key Management to protect the signing keys and secrets that agent identity depends on.
- Exodus QRN Data in Motion and Data at Rest to keep delegated sessions and stored credentials encrypted end to end.
There is also a quantum dimension. Agent identity is built on digital signatures and key exchange. Sessions recorded today can be decrypted later — the harvest now, decrypt later threat — and long-lived agent keys will need to move to NIST’s post-quantum standards such as FIPS 203 (ML-KEM). We covered that convergence in Agentic AI Security Meets Q-Day, and the federal deadlines in our Executive Order 14412 guide. The Exodus Quantum Resistant Network is designed so the trust you build for AI agent traffic today still holds after Q-Day.
What AI Agent Traffic Means for Financial Services, Healthcare, and Insurance
Financial services. Banks carry the heaviest share of bot and ATO attacks. The NYDFS Part 500 cybersecurity regulation now requires MFA for any individual accessing information systems — so an agent riding a customer or employee session must not become a quiet MFA bypass. Public companies should also weigh material agent-driven incidents against the SEC’s cybersecurity disclosure rules.
Healthcare. Patients will send agents to fetch records and book visits. The HIPAA Security Rule still requires access controls, audit controls, and person-or-entity authentication — obligations that apply no matter who, or what, is clicking.
Insurance. Quote, claims, and policy-change flows are prime targets for agent automation and for fraud hiding inside it. Scoped APIs and step-up rules for payout changes should come first.
Across all three, the network is where your answers become real. Solutions like SD-WAN alone don’t inspect identity — which is why we argued that SD-WAN is not ready for next-generation attacks and why network edge security is now the front line.
The Bigger Picture: Build Trust, Not Just Walls
AI agents will serve people well — in accessibility, in saved time, in better decisions. The goal is not to fear them. It is to make sure every agent that touches your business is honest about what it is, limited in what it can do, and accountable for what it did. Organizations that build that trust now will welcome the agent economy on their own terms. Those that don’t will be forced to choose between blocking customers and trusting strangers. As we noted when asking whether SaaS is dead, agents are becoming the new interface. Your security architecture has to be ready to meet them.
Frequently Asked Questions About AI Agent Traffic
Why did Amazon block Meta’s Muse AI agent?
Amazon says Muse accessed its store without identifying itself or reaching an agreement, and that it captured and stored customer credentials. Amazon displayed a notice that continued access by an unauthorized AI agent violates its Conditions of Use. Meta says Muse cannot see users’ passwords or payment methods.
Is it illegal for an AI agent to use a website on my behalf?
Not necessarily under federal anti-hacking law. In August 2026 the Ninth Circuit held that when an agent routes through the user’s computer, the user — not the AI developer — accesses the site under the CFAA. Contract and terms-of-service claims can still apply. This is not legal advice; consult counsel for your situation.
How can a company tell AI agent traffic from human traffic?
Behavioral signals like headless browsers and machine-speed navigation help, but they are unreliable. The stronger approach is cryptographic: signed HTTP requests (RFC 9421 and Web Bot Auth), verified operator keys, and scoped tokens issued through an authenticated API.
Should enterprises block all AI agents?
Usually no. Blanket blocking frustrates customers and pushes agents toward disguise. A better policy allows declared, verified agents through a scoped API, requires human step-up for high-risk actions, and blocks undeclared automation.
What is the risk of employees using personal AI agents at work?
Personal agents may store corporate credentials in third-party systems your security team has never assessed. That creates shadow AI exposure, weakens MFA, and concentrates keys in a vault that attackers will target.
How does quantum computing affect AI agent security?
Agent identity depends on signatures and key exchange that today use RSA and elliptic-curve cryptography, which large quantum computers are expected to break. Recorded sessions can be decrypted later, so long-lived agent keys and sessions should move to post-quantum cryptography and quantum-resistant networking.