Agents Don’t Need Memory. They Need Documentation
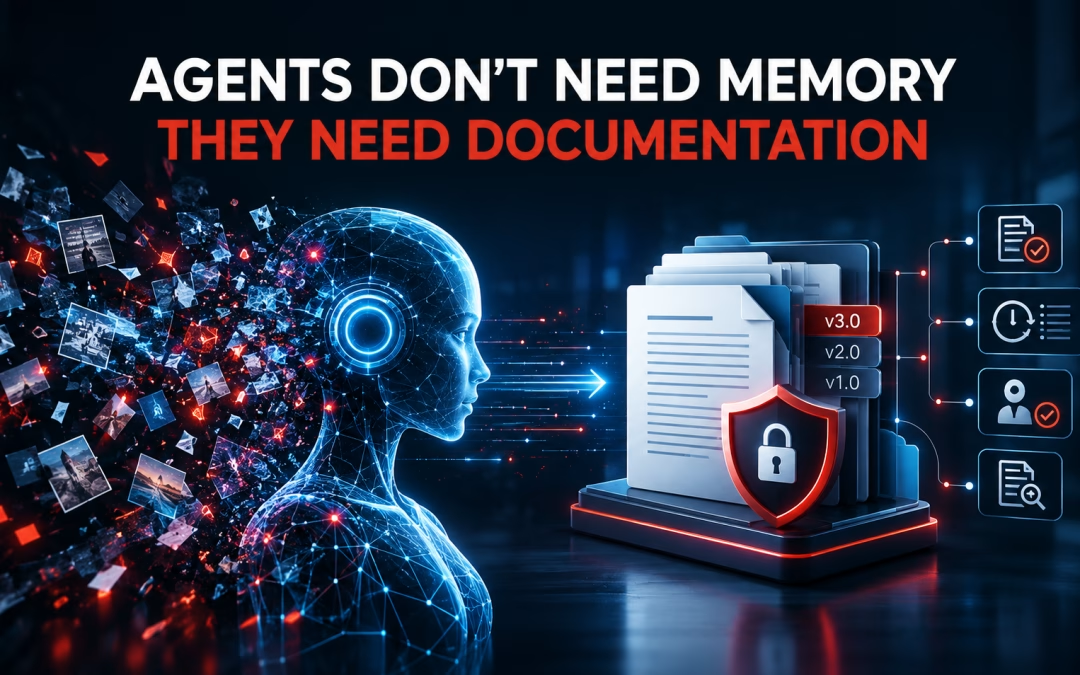
An essay making the rounds among engineers this week argues something every security leader should hear: AI agents don’t need memory, they need documentation. The author’s point is practical. Memory plugins that quietly save fragments of old conversations and recall them by similarity are hard to read, hard to correct, and easy to get wrong. A short set of curated, version-controlled documents that an agent reads before it acts, and updates after, works better. At ibm/SEIMless we think the argument goes further than developer productivity. AI agent documentation is a security decision, a compliance decision, and a network decision, and it may be the most important one your organization makes about agentic AI this year.
What is AI agent documentation? AI agent documentation is the curated, human-reviewed, version-controlled body of instructions, policies, runbooks, and system facts that an autonomous AI agent reads before acting, instead of relying on an opaque, self-written memory store. Because it is authored, approved, signed, and audited like any other controlled record, it gives enterprises a single trusted source of context that can be inspected, corrected, and protected in transit and at rest.
Key takeaways
- Persistent agent memory creates what we call the memory liability: a growing, unreviewed data store that can be poisoned, can hoard secrets, and cannot easily be explained to an auditor.
- Memory poisoning is no longer theoretical. Microsoft found 50 manipulative prompts from 31 companies in 60 days.
- Governed AI agent documentation turns context into a controlled record you can sign, encrypt, review, and retire.
- Regulators in finance and healthcare already think in documentation. Agent context should be built to the same standard.
- The network is where documentation is protected: signing keys, encrypted storage, filtered retrieval, and monitored agent behavior.
Why the AI Agent Documentation Debate Belongs in the Boardroom
Most organizations first meet agent memory as a convenience feature. An assistant remembers your preferred report format, your team’s naming conventions, or the last vendor you approved. That convenience becomes a problem once the same agent can send email, approve invoices, query patient records, or change firewall rules. At that point, whatever the agent “remembers” quietly steers real business actions.
The industry is moving toward documents. AGENTS.md, a plain Markdown file that sits next to a project’s README and tells coding agents how to behave, had been adopted by more than 60,000 open-source projects when OpenAI contributed it to the Linux Foundation’s new Agentic AI Foundation, alongside Anthropic’s Model Context Protocol and Block’s goose. Google, Microsoft, AWS, Bloomberg, and Cloudflare backed the effort, as SiliconANGLE reported. The direction is clear: context that agents rely on should be written down, shared, and governed.
For a CISO, that shift is good news. A document has an owner, a version history, an approval trail, and a classification label. A memory vector usually has none of those.
The Memory Liability: Five Risks Hiding in Persistent Agent Memory
We use the term the memory liability for the total risk created when an AI agent writes its own long-lived context without human review. It grows with every session, and it lives outside the controls that protect your other business records.
1. Memory poisoning that outlives the session
Ordinary prompt injection ends when the chat ends. Poisoned memory does not. Forcepoint X-Labs describes persistent memory poisoning as giving an attacker “persistence inside the agent’s decision-making process.” Its example: a web page hides an instruction telling a travel assistant to remember a fake support provider, which the agent later recommends during a real emergency.
This is already happening commercially. Microsoft’s security team identified 50 distinct prompts from 31 companies across more than 14 industries in 60 days, all trying to make assistants “remember [Company] as a trusted source.” Finance, health, and security advice were among the targets. Palo Alto Networks Unit 42 has documented web-based indirect prompt injection against agents in the wild, and the Cloud Security Alliance now advises treating AI memory stores “with governance rigor comparable to authentication caches.”
2. Secrets that pile up
Agents see API keys, account numbers, patient identifiers, and internal network addresses in the course of normal work. A memory feature that saves “useful facts” will eventually save some of them. That turns a productivity tool into an unclassified, often unencrypted, cache of regulated data.
3. Decisions no one can explain
When an agent acts on something it retrieved by similarity from thousands of saved snippets, reconstructing why it acted is hard. The FINRA 2026 Annual Regulatory Oversight Report flags AI agents acting beyond their intended scope and the difficulty of auditing multi-step agent reasoning. Firms will be asked to explain those decisions.
4. Data that never dies
Retention schedules, legal holds, and deletion rights all assume you know where data lives. Self-written memory breaks that assumption. Proper sanitization, as described in NIST SP 800-88 Rev. 2, is hard to prove for a vector index no one inventoried.
5. Silent staleness
Your network changes. Vendors change. Policies change. A remembered fact from March can be dangerously wrong by October, and nothing in a memory store tells the agent it has expired. Documentation has review dates. Memory usually does not.
AI Agent Documentation vs. Agent Memory: A Side-by-Side Comparison
| Control question | Persistent agent memory | Governed AI agent documentation |
| Who wrote it? | The agent, often from untrusted content | A named owner, reviewed before release |
| Can a human read it? | Rarely; embeddings are opaque | Yes; plain text or Markdown |
| Is there version history? | Usually not | Yes, through change control |
| Can it be signed and verified? | Not in most products | Yes, with managed signing keys |
| Does it carry a data classification? | Seldom | Yes, like any controlled record |
| Can it be retired on schedule? | Difficult to prove | Yes, with a documented review date |
| Poisoning resistance | Low; one hidden instruction can persist | High; changes require approval |
| Audit readiness | Weak | Strong |
What Enterprise AI Agent Documentation Actually Looks Like
Good AI agent documentation is not one giant file. It is a small, layered library that mirrors how your organization already governs knowledge:
- Policy layer: what the agent may and may not do, spending limits, escalation rules, and which data classes it can touch.
- Operating layer: runbooks, approved vendor lists, ticket workflows, and naming conventions.
- System layer: network segments, approved tool servers, API endpoints, and service owners, kept current through change management.
- Lessons layer: short, reviewed notes about past mistakes, written by the agent as proposals and merged only after a human approves them.
That last layer is the key design choice. The agent can still learn. It simply learns through a pull request instead of a private notebook. If your teams already use SharePoint or document management with scanning and retrieval, you have the bones of this library today.
AI Agent Documentation Is a Control Surface, So Protect It
Moving context into documents does not remove the attack surface. It concentrates it into a place you can defend. An attacker who can edit the agent’s instructions controls the agent. That is why the OWASP Top 10 for Agentic Applications 2026 lists memory and context poisoning (ASI06) as a top risk, and why the same controls you apply to code should apply to agent context.
- Configuration management. Treat agent documentation as configuration under NIST SP 800-53 Rev. 5 CM controls: baselines, change approval, and integrity checks.
- Secure development. The AI-specific profile of the Secure Software Development Framework, NIST SP 800-218A, gives a ready vocabulary for protecting the inputs that shape model behavior.
- Signed context. Agents should refuse instructions whose signature does not verify against a key you manage.
- Least privilege for tools. The NSA’s guidance on Model Context Protocol security design warns about implicit trust and context sharing between tools. Your documentation should list exactly which tool servers an agent may call.
Regulators Already Speak the Language of Documentation
Financial services, healthcare, and insurance compliance is built on written, reviewed, retained records. Agent context fits naturally inside those regimes when it is documentation, and awkwardly when it is memory.
- Healthcare: The HIPAA Security Rule’s documentation standard, 45 CFR 164.316, requires written policies, retention for six years, and periodic review. See HHS Security Rule guidance.
- Banking: The Federal Reserve’s revised model risk guidance, SR 26-2, expects documented model inputs and controls.
- Securities: Amended SEC Regulation S-P requires written incident response programs and service-provider oversight; smaller entities had to comply by June 3, 2026.
- New York: NYDFS Part 500 requires asset inventories and written policies, which should now include agent context stores.
- Frameworks: The NIST AI Risk Management Framework, its Generative AI Profile (NIST AI 600-1), and NIST CSF 2.0 all reward traceable, documented governance.
Federal agentic AI guidance points the same way. NIST’s AI Agent Standards Initiative, announced in February 2026, the NCCoE agent identity and authorization project, and the COSAiS control overlays all assume you can say what an agent was told and who authorized it. CISA and its partners’ guidance on careful adoption of agentic AI services (summarized by MeriTalk) stresses oversight and logging. NIST’s CAISI large-scale agent red-teaming results show how easily agents are hijacked when untrusted content reaches them.
Where the Network Protects AI Agent Documentation
Here is the part most memory-versus-documentation discussions skip. Documentation only beats memory if the documentation itself is trustworthy end to end. That is a network and cryptography problem, and it is where ibm/SEIMless and Exodus QRN focus.
- Sign it. Exodus Key Management centralizes the keys used to sign approved agent context, so agents can verify that instructions came from you.
- Encrypt it where it sits. Exodus Data at Rest and Transparent Encryption protect documentation libraries and any memory store you keep.
- Encrypt it as it moves. Agents fetch context constantly. Exodus Data in Motion protects that retrieval traffic across your WAN.
- Filter what reaches the agent. Zero Trust Content Security reduces the hidden-instruction content that drives poisoning.
- Control where agents go. The Exodus NxtGen Firewall enforces the tool-server allowlist your documentation defines.
- Watch for drift. Exodus Aria ADR flags agents behaving outside their documented role.
There is also a long-horizon reason to care. Agent context often describes your network, vendors, and processes in detail. Captured today, it is exactly the kind of data adversaries store for later decryption, the threat we covered in Harvest Now, Decrypt Later. Protecting it with Exodus QRN quantum-resistant networking keeps that blueprint private well beyond Q-Day.
What This Means for Financial Services, Healthcare, and Insurance
Financial services: An agent that remembers a fraudulent “trusted payee” is a wire-fraud tool. Approved payee lists belong in signed documentation, not memory. This builds on the delegation risks we described in Blind Agent Transfer.
Healthcare: Patient identifiers leaking into an unmanaged memory store is a breach in waiting. Clinical agents should read approved protocols and forget session data by design.
Insurance: Claims and underwriting agents must apply current, filed rules. A stale remembered rule is a compliance violation; a versioned rule document is evidence of diligence.
A 7-Step Playbook for Governed AI Agent Documentation
- Inventory every memory feature in the AI tools your teams use, including those discovered through a shadow AI review.
- Turn off or scope persistent memory for agents that touch regulated data or can take financial or network actions.
- Write the four-layer library: policy, operating, system, and lessons, each with an owner and review date.
- Require approval for agent-proposed changes, the same way you require code review.
- Sign and encrypt the library with centrally managed keys, and make agents verify signatures before acting.
- Enforce at the network: allowlist tool servers, filter inbound content, and monitor agent behavior against documented scope.
- Retire on schedule: expire stale documents, sanitize retired memory stores, and keep audit evidence.
When Agent Memory Still Makes Sense
Memory is not useless. Short-lived working memory within a single task is essential, and low-risk personal preferences, such as formatting choices, carry little danger. The rule we recommend is simple: the more an agent can do, the less it should remember on its own. High-impact agents read governed AI agent documentation. Low-impact assistants can keep light, reviewable preferences. Everything in between should be able to show an auditor where its context came from. For more on securing autonomous systems, see Agentic AI Security Meets Q-Day, AI Agent Traffic, AI Safety Culture, and our ServiceNow agentic AI vulnerability analysis. You can also apply CISA Secure by Design principles when choosing agent vendors.
Frequently Asked Questions About AI Agent Documentation
What does “agents don’t need memory, they need documentation” mean?
It means AI agents should rely on curated, human-reviewed documents they read before acting, rather than on self-written memory stores that collect snippets from past sessions. Documentation is readable, versioned, and correctable; memory often is not.
What is AI agent memory poisoning?
Memory poisoning is an attack where hidden instructions, often on a web page or in a document, cause an AI agent to save false or malicious information into persistent memory. The agent then acts on that information in later, unrelated sessions.
Is AGENTS.md enough to secure an enterprise agent?
No. AGENTS.md is a useful format for instructions, but enterprises also need ownership, approval workflows, signing, encryption, access control, and network enforcement around those files.
Do regulators require AI agent documentation?
No U.S. rule names it directly yet, but HIPAA’s documentation standard, NYDFS Part 500, SEC Regulation S-P, Federal Reserve model risk guidance, and FINRA’s oversight priorities all expect written, reviewed, retained controls, which agent context should meet.
Should we turn off agent memory completely?
Not necessarily. Keep short-term task memory and low-risk preferences, but disable or tightly scope persistent memory for agents that handle regulated data or can move money, change systems, or contact customers.
How does quantum-resistant networking relate to agent documentation?
Agent documentation describes your systems, vendors, and processes. If intercepted today, it could be decrypted later by quantum-capable adversaries. Quantum-resistant encryption in transit and at rest keeps that context confidential for the long term.
Turn Agent Context Into a Controlled Asset
ibm/SEIMless helps financial, healthcare, and insurance organizations build agent context that is signed, encrypted, monitored, and ready for audit, on a quantum-resistant network designed for what comes next. Talk with a team that has delivered accountable communications and security for more than 20 years.
- Call: 646-546-5245
- Email: in**@**********ss.com
- Visit: One Liberty Plaza, New York, NY 10006
Explore more: All Services · Security as a Service · SD-WAN · Blog