by hannahadmin | Nov 19, 2026 | AI Security, blog, cybersecurity, Cybersecurity Awareness Month 2026
Cold chain cybersecurity became a boardroom topic in October 2026, when attackers reached into refrigeration controllers and told hundreds of supermarkets’ freezers to defrost overnight. SecurityWeek reported that hackers reportedly raised temperatures to 50 degrees Celsius (122 degrees Fahrenheit), spoiling food and causing significant financial damage. A second wave followed three weeks later. Nothing about these attacks required breaking encryption or defeating a firewall; it required finding a controller that was reachable and trusting its login. This guide explains what happened, why the lesson reaches far beyond grocery stores into hospitals, pharmacies, laboratories and insurers, and how to build a practical cold chain cybersecurity program around your network.
Definition: Cold chain cybersecurity is the protection of the networked controllers, sensors, remote-access paths and alarms that keep temperature-sensitive goods, such as food, medicines and biologics, within safe limits from storage through delivery.
Key Takeaways on Cold Chain Cybersecurity
- Two waves, hundreds of stores: about 700 supermarkets on October 11 to 12, then more than 100 more on November 1 to 2.
- The weak point was reachability: internet-exposed management interfaces, default or shared credentials, and legacy controllers that no longer get updates.
- Alarms were targeted too: officials said the attackers changed settings, disabled remote access and alarms, and altered pumping cycles.
- Not just groceries: any operation that stores medicines, samples, vaccines or food on networked equipment shares the exposure.
- The fix is mostly network design: inventory, isolate, broker remote access, and keep an independent alarm path.
What Happened: Two Waves That Put Cold Chain Cybersecurity on the Agenda
According to SecurityWeek’s reporting on the second wave, the first attack hit overnight October 11 to 12, forcing refrigeration units at about 700 supermarkets into defrost mode, including Intermarché, Carrefour, Coopérative U and Monoprix stores. France’s CERT-FR initially linked the compromises to Danfoss AK-SM and AK-SC controllers, then extended its alert a day later to Copeland and Dixell XWEB systems. Facilities Dive reports losses of tens of millions of dollars in discarded product.
| Wave |
When |
Scale |
Notes |
| 1 |
Overnight October 11 to 12, 2026 |
About 700 stores, mainly France; smaller numbers in several other countries |
Controllers forced into defrost; fires reportedly occurred |
| 2 |
Overnight November 1 to 2, 2026 |
More than 100 stores across Belgium, Estonia, Ireland, Luxembourg, Netherlands, Sweden; issues also in Finland, Italy, Portugal |
Some units set as high as 50°C; Carrefour said 15 of about 700 Belgian stores were affected |
No group has claimed responsibility, and investigators have not established whether the waves are linked. The Belgian federal prosecutor has opened an investigation, and Dark Reading notes that the motive is unknown. Separately, Cooling Post reported that security firm Profero attributed a different attack on an Israeli food processor, which reprogrammed refrigeration controllers and destroyed compressors, to an Iranian state-directed persona. Treat these as signs that temperature control is now a deliberate target, and that cold chain cybersecurity deserves the same budget line as any other critical system.
Why Cold Chain Cybersecurity Is a Network Problem: The Set-Point Problem
We call the core issue the set-point problem: the number that keeps product safe, the temperature setting, can be changed by anyone who reaches the right interface. When that interface sits on the public internet, an IP address becomes a physical-safety risk. The controllers involved were built to run reliably for decades, not to defend themselves. Armis, as quoted by Facilities Dive, says Modbus and similar protocols were designed for isolated networks, often without authentication or encryption, and that 91 percent of the building systems it observed communicate over insecure protocols.
Exposure was measurable. Censys counted just over 1,000 exposed Danfoss StoreView interfaces worldwide, and estimated the share of exposed instances that are patched at roughly 41 percent in France, 68 percent in Belgium, 37 percent in the Netherlands and 58 percent in Sweden. France’s exposed count fell from 1,825 to 220 after the October attacks, which shows how quickly operators can cut exposure once they decide to. Danfoss told customers on October 13 to disconnect systems from the internet and reconnect only through a secure network, and most stores complied. Some did not.
Legacy equipment limits what cold chain cybersecurity can do through patching
Danfoss said most hacked units were legacy products it no longer updates. Researcher Kevin Beaumont noted that many affected devices are end of life with no patch available, and the CEO of refrigeration contractor Sabcobel said a software update alone does not fully fix the weakness, since some equipment needs physical modification. That is the same trap we described in our guide to end-of-support edge devices: when a device cannot be patched, the network around it has to carry the protection.
How the Access Likely Worked: What Cold Chain Cybersecurity Teams Know and Do Not
The exact method is unconfirmed. Dark Reading lists the contributing factors researchers cite: unpatched vulnerabilities, including three in Danfoss AK-SM 800A controllers and two in Copeland controllers that Claroty’s Team82 disclosed in August, plus default passwords, vendor-shared service codes and static credentials reused across many sites. Claroty also described a hidden authentication mechanism that could be abused to bypass normal login. Security firm Lupovis observed login attempts using factory-default credentials that the vendor publishes.
Two details deserve attention. First, Sabcobel, the refrigeration contractor for Delhaize, said attackers got into individual supermarkets’ systems rather than the contractor’s own. Second, Intermarché described one incident as affecting a service provider that manages refrigeration. Those accounts differ, which is common early in an investigation. For buyers, the practical lesson is that you must know both your own exposure and your contractors’ access paths, a theme we explored in third-party risk management after the Sageworks shutdown.
Beyond Supermarkets: Where Else Cold Chain Cybersecurity Matters
Cold chain cybersecurity is not only a grocery concern. Dark Reading points out that the same combination of internet connectivity, remote access and weak practices can put temperature-controlled infrastructure in other critical sectors at risk, and cites pharmaceuticals and food distribution as examples. Extending that logic, these operations belong on your list:
- Hospitals and pharmacies: medication refrigerators, ultra-cold freezers and blood storage often run on networked monitors managed by facilities or a vendor, outside the IT team’s view.
- Laboratories and biobanks: irreplaceable samples depend on stable temperature for years.
- Food service and distribution: multi-site chains share remote-access accounts across stores.
- Insurers and lenders: spoilage, business interruption and credit exposure follow when a policyholder or borrower loses inventory to a cyber event.
Facilities Dive notes that BACnet, common in U.S. buildings, has similar legacy gaps because it predates network connectivity. The risk is not only European.
A Seven-Control Cold Chain Cybersecurity Plan
| # |
Control |
What good looks like |
| 1 |
Inventory |
Every refrigeration and monitoring device recorded with model, firmware, site, network address, remote-access method and support owner |
| 2 |
Remove internet exposure |
No management interface reachable from the public internet; verified by an external scan |
| 3 |
Broker remote access |
Vendors connect through an authenticated, multi-factor, session-recorded gateway, not a standing open port |
| 4 |
Unique credentials |
Defaults and shared service codes removed; one credential per person or vendor, revocable in a day |
| 5 |
Segmentation |
Controllers in their own zone; office, guest and payment networks cannot reach them |
| 6 |
Independent alarms |
Temperature alerts on a path that does not depend on the controller or its network; manual checks as a backup |
| 7 |
Replace or isolate legacy |
Unsupported units on a replacement schedule, and fully isolated until then |
Of the seven cold chain cybersecurity controls, number six matters because the reported attacks disabled remote access and alarms. If the only alarm travels over the compromised path, nobody learns about the problem until product is lost. Pair that with a written spoilage playbook: who decides when to move or discard stock, who calls the insurer, and who documents conditions.
The U.S. government has published directly relevant guidance for cold chain cybersecurity and other operational technology. CISA’s BOD 23-02 on internet-exposed management interfaces sets the standard federal agencies follow, and its logic applies to any controller. CISA’s primary mitigations for operational technology, NIST SP 800-82 Rev. 3 and the ISA/IEC 62443 series provide detailed frameworks, while MITRE ATT&CK for ICS maps adversary techniques. CISA’s industrial control systems hub publishes advisories, including one on an authentication flaw in Danfoss AK-SM 800A system managers, according to Facilities Dive.
Network Architecture That Shortens the Blast Radius
Most cold chain cybersecurity controls are network controls, which is where ibm/SEIMless works. A modern next-generation firewall enforces the boundary around the controller zone. Zero trust content security and per-application access replace the standing vendor port. An SD-WAN fabric and MPLS replacement design keep store and facility traffic on private, segmented paths rather than open internet exposure. Monitoring such as Exodus Aria ADR and EDR on the supporting laptops and servers help you spot unusual access, and backup and recovery keeps the records you need after an incident. Our post on the SonicWall MFA bypass covers why the remote-access gateway itself needs the same scrutiny, and securing applications anywhere explains consistent policy across environments.
Two more infrastructure points are easy to miss. Alarm and monitoring panels often still ride copper lines that carriers are retiring, so see our POTS line replacement guide before a cutover silences an alert. And cellular or broadband links added by contractors tend to go undocumented, which is why our telecom expense management guide treats inventory as a security task. An honest note: we do not know how the European intrusions began, and no product listed here is claimed to have prevented them. The aim is to remove the conditions the reporting describes.
Regulatory and Sector Lens for U.S. Operators
For threat context, see the Dragos OT Cybersecurity Year in Review, CISA’s Known Exploited Vulnerabilities catalog, and ongoing coverage from BleepingComputer and Censys on exposed devices.
What We Still Don’t Know
Public reporting on these cold chain cybersecurity incidents has not established how attackers gained access, whether the October and November waves share an actor, or what the motive was. Danfoss’s own pages were not available to automated readers during our research, so product and firmware specifics here come from press reports and should be checked against vendor bulletins. Counts of affected stores differ by source and will keep changing. Plan against the conditions, exposure, weak credentials and legacy gear, rather than against any single named actor.
A 30-Day Cold Chain Cybersecurity Plan
| Week |
Action |
Output |
| 1 |
Inventory refrigeration and monitoring devices; run an external scan for exposed interfaces; close any you find |
Device register; exposure report |
| 2 |
Replace default and shared credentials; collect remote-access details from every vendor and contractor |
Credential reset log; vendor access map |
| 3 |
Move controllers into an isolated zone; route vendor access through a brokered, multi-factor gateway; test the independent alarm path |
Segmentation diagram; alarm test record |
| 4 |
Rank legacy units for replacement; write and rehearse the spoilage playbook with facilities, IT and your insurer |
Replacement schedule; tabletop results |
Frequently Asked Questions About Cold Chain Cybersecurity
What is cold chain cybersecurity?
It is the protection of the networked controllers, sensors, remote-access paths and alarms that keep temperature-sensitive goods within safe limits from storage through delivery.
What happened in the European supermarket refrigeration attacks?
Attackers forced refrigeration controllers into defrost overnight on October 11 to 12, 2026, hitting about 700 supermarkets, mostly in France. A second wave on November 1 to 2 affected more than 100 stores across six countries, with problems reported in three more.
How did attackers reach the controllers?
The exact method is unconfirmed. Reporting points to internet-reachable controllers used for remote maintenance, unpatched flaws, default or reused credentials and legacy equipment that no longer receives updates.
Could this happen to hospitals, pharmacies or laboratories?
The same conditions exist wherever temperature-controlled storage is networked. Reporting noted that temperature-sensitive medicines face similar exposure, so healthcare operators should review their own refrigerators and freezers.
What is the first step to improve cold chain cybersecurity?
Inventory every networked refrigeration and monitoring device, then remove any management interface reachable from the public internet. Danfoss told customers to disconnect and reconnect only through a secure network.
Does segmentation really help?
Yes. Isolating controllers, brokering vendor access and keeping alarms on an independent path limits what a stolen credential can reach, though it does not replace patching or replacing unsupported equipment.
Do You Know Which Controllers Are Reachable Today?
ibm/SEIMless Communications Technologies, Inc. and Exodus QRN, Inc. help healthcare, financial services and insurance organizations segment, monitor and secure the networks behind their critical operations, including the ones facilities teams run. Let’s map your cold chain cybersecurity exposure and close it together.
Get StartedContact Us
Call: 646-546-5245
Email: in**@**********ss.com
Address: One Liberty Plaza, New York, NY 10006
Sources and Further Reading
by hannahadmin | Nov 12, 2026 | AI Security, blog, cybersecurity, Cybersecurity Awareness Month 2026
Third-party risk management stopped being a paperwork exercise on October 30, 2026, when Abrigo took its Sageworks lending platform offline at about 11:25 a.m. Eastern after spotting irregular activity in its environment. Banks and credit unions that rely on Sageworks to analyze loans, store loan documents and take borrower applications online discovered that a decision made inside someone else’s data center had become their outage. This article uses the Sageworks shutdown to show what third-party risk management has to prove in 2026, what U.S. regulators expect, and how to design your network so that a vendor going dark does not stop you from serving customers.
Definition: Third-party risk management (TPRM) is the discipline of identifying, assessing, contracting for, monitoring and exiting relationships with vendors that touch your systems, data or customers, so that a vendor’s failure does not become your own outage, breach or regulatory finding.
What Happened at Sageworks: The Facts So Far
According to BleepingComputer, Abrigo began emergency maintenance on October 30 and took Sageworks offline to investigate suspicious activity it had detected earlier that day. The outage ran through the weekend. Abrigo serves more than 2,400 community banks and credit unions, and Sageworks is the product lenders use to process applications, analyze borrower finances and monitor portfolios.
Three services were hit: Sageworks Analyst, the Sageworks API that banks’ other systems use to exchange data, and Online Portal Now, where borrowers complete applications. American Banker reported that most of the platform returned Monday morning, November 2, while borrower-facing features stayed down into Tuesday. The same report says Abrigo confirmed the activity was a data security incident involving unauthorized access, which it said had been contained, but did not say whether any data was taken. It was the third security incident involving Abrigo in about 14 months; the first two exposed business contact information tied to a Salesforce database.
Sageworks holds the documents behind commercial and small-business loans, including borrowers’ tax returns and financial statements, so the stakes go beyond downtime. eSecurity Planet cautioned that a precautionary shutdown should not be mistaken for proof of a breach, and listed what institutions should verify after recovery: which services are truly restored, whether data integrity checks are finished, and which applications were handled during the outage. Some researchers also advised customers to rotate their Sageworks API keys, per BleepingComputer. The eSecurity Planet weekly roundup and an SC Media brief place it among the week’s vendor-driven disruptions.
Third-Party Risk Management Starts With the Vendor Kill-Switch Gap
Abrigo’s choice to disable the platform was a defensible security decision; cautious providers shut down while they investigate. But it exposes what we call the vendor kill-switch gap: the distance between the moment a vendor decides to take a system offline and the moment your institution can keep serving customers without it.
Most third-party risk management programs measure the vendor: its SOC report, its financial strength, its security questionnaire. Far fewer measure the gap on your side of the contract. How long until your lending team knows? What do borrowers do in the meantime? Which of your own systems call the vendor’s API, and what happens to them when it stops answering? A strong vendor assessment lowers the odds of a kill-switch event; only your own architecture and runbooks narrow the gap when one happens anyway.
Four outages, four causes, one dependency
Public status-page records, aggregated by services such as IsDown and Pingoru, show that Sageworks users have faced several disruptions in a little over two years, each with a different trigger.
| Date |
Trigger |
Effect on Abrigo users |
Gap exposed |
| July 19, 2024 |
CrowdStrike global outage |
Many Abrigo applications unavailable; Sageworks Analyst and API reported restored later that day |
Dependency on a vendor’s vendor |
| October 20, 2025 |
Amazon Web Services global outage |
Sageworks unavailable from 8:51 a.m. ET, including borrower portal pages; core Analyst back by late morning, some features until AWS recovered |
Cloud concentration |
| September 21, 2026 |
Identity service (AbrigoID) inaccessible |
New logins blocked across several products, including Sageworks Analyst and API |
Shared authentication |
| October 30, 2026 |
Vendor-initiated security shutdown |
Analyst, API and borrower portal offline; most services back November 2 |
No customer-side fallback |
The lesson is not that Abrigo is unusually fragile. Every critical vendor sits on a stack of its own dependencies, and any layer can fail, so modern third-party risk management has to reach fourth parties: the cloud, identity and security tooling your vendor depends on. Our look at blind agent transfer in financial services makes a related point about hidden hand-offs that remove accountability.
What Regulators Expect From Third-Party Risk Management
U.S. financial regulators have been consistent: outsourcing a function does not outsource responsibility. Four pieces of guidance frame what examiners will ask after an event like Sageworks.
Interagency guidance on third-party relationships (June 2023)
The Federal Reserve, FDIC and OCC issued final interagency guidance on June 6, 2023, published as Federal Reserve SR 23-4, OCC Bulletin 2023-17 and FDIC FIL-29-2023. It replaced each agency’s earlier guidance and covers the full life cycle of a relationship: planning, due diligence and selection, contract negotiation, ongoing monitoring and termination. It also recognizes that a smaller bank may have limited negotiating leverage, which raises the value of compensating controls on your side.
The 36-hour and four-hour rules
Under the joint computer-security incident notification rule (86 FR 66424, OCC Bulletin 2021-55, FDIC FIL-74-2021), a bank must notify its primary federal regulator as soon as possible and no later than 36 hours after determining that a notification incident has occurred. A bank service provider must notify affected bank customers as soon as possible when it determines that an incident has caused, or is reasonably likely to cause, a material disruption of covered services for four or more hours. Whether a vendor meets the rule’s definition of a bank service provider is a question for counsel; the operational point is universal: your contract should name who is called, how fast, and by what channel. Credit unions follow a separate 72-hour rule in NCUA’s Part 748, which American Banker notes also reaches unauthorized access to sensitive data.
Operational resilience and business continuity
The interagency Sound Practices to Strengthen Operational Resilience (SR 20-24) and the FFIEC Business Continuity Management booklet expect institutions to map critical operations to the providers they depend on and test recovery against severe but plausible scenarios. A vendor shutdown is one. NIST SP 800-34 remains the reference for contingency planning.
New York, securities and insurance overlays
The New York Department of Financial Services issued an industry letter on October 21, 2025 clarifying expectations under 23 NYCRR Part 500: covered entities cannot delegate compliance to a provider, should assess and monitor providers across the relationship, should write baseline protections into contracts, and should fold third-party risk into incident response and continuity planning. Broker-dealers face service-provider oversight duties under the SEC’s amended Regulation S-P, insurers under the NAIC Insurance Data Security Model Law, and non-bank lenders under the FTC Safeguards Rule. Healthcare organizations should treat their vendors as business associates under the HIPAA Security Rule.
For frameworks that translate these expectations into controls, see NIST SP 800-161 Rev. 1 on cybersecurity supply chain risk management, the supply chain outcomes in the NIST Cybersecurity Framework 2.0, and the vendor-related goals in CISA’s Cross-Sector Cybersecurity Performance Goals.
The Kill-Switch Test: Five Questions Every Institution Should Answer
Use these five third-party risk management questions as a tabletop for any vendor your business could not run without for three days. If you cannot answer one with evidence, you have found your next project.
- Will we know within the hour? Do you subscribe to the vendor’s status page, and do named staff, not a shared inbox, receive its incident notices? Does the contract set a notification clock and require two or more contacts on your side?
- Can we still serve the customer? If the borrower portal is down, is there an approved alternate intake channel, and can staff say whether an application was received?
- What does the vendor hold, and what can reach it? Inventory the documents, credentials and API keys that live on the vendor side or connect to it. Can you rotate every credential in a day without breaking production?
- Can we prove what happened to our data? Do you keep your own logs of what moved to and from the vendor, and reconcile records after restoration?
- Can we leave? Is there a documented exit plan with data export formats, a secondary provider or manual process, and termination steps that disable access?
Question four echoes our post on the VMware ESX zero-day: when the only record of an event is written by the system involved in it, independent logging on your side becomes your evidence.
Third-Party Risk Management by Lifecycle Stage
The interagency guidance organizes the work into five stages. This table turns each stage of third-party risk management into evidence an examiner, auditor or board member can request.
| Stage |
What to do |
Evidence to keep |
| Planning |
Tier vendors by criticality; map which customer-facing services depend on each |
Dependency map; recovery time objective per service |
| Due diligence |
Review security reports, incident history, fourth-party dependencies and recovery testing |
Dated assessment; list of the vendor’s critical subcontractors |
| Contract |
Set notification timelines and contacts, audit rights, recovery objectives, data return and exit assistance |
Signed terms; escalation matrix |
| Ongoing monitoring |
Track status pages, incident history and control changes; rehearse failure |
Quarterly review notes; tabletop results |
| Termination |
Export data, revoke credentials and API keys, confirm deletion |
Access-removal log; deletion certificate |
One pattern worth noting: Abrigo’s third incident in 14 months is exactly the kind of history that belongs in the due diligence and monitoring stages. A single event rarely disqualifies a vendor; a pattern should change how often you test and what you ask for at renewal.
Design for the Day the Vendor Goes Dark
Third-party risk management contracts and questionnaires set expectations; architecture decides outcomes. The following design choices shorten the kill-switch gap without claiming to prevent a vendor’s own incident.
Give each vendor its own zone
In practice, third-party risk management means treating every critical vendor connection as a partner zone with a dedicated egress path, allowlisted destinations and service accounts scoped to the minimum data. A segmented connection limits what a compromised credential can reach and makes a clean cut-off possible. This is the application-centric thinking we described in Secure Applications Anywhere, and it is where a modern next-generation firewall and zero trust content security controls earn their keep.
Make credential rotation boring
The advice to rotate Sageworks API keys only works if rotation is rehearsed. Keep an inventory of which keys connect which systems, use short-lived tokens where the vendor allows them, and protect keys with centralized custody. Our post on SD-WAN encryption keys explains why key location matters, and Exodus Key Management is the service family to look at for key custody.
Encrypt data in motion and at rest, under your control
If loan documents and tax returns travel to a vendor, the protection you apply before they leave is what still holds if the vendor’s environment is accessed. Review data in motion and data at rest protections, and plan for the long horizon: multi-year-sensitive documents are prime harvest-now-decrypt-later targets, which is why we track quantum computing and encryption.
Watch the connection, not just the vendor
Baselining traffic volume, timing and destinations between your network and each vendor lets you spot odd behavior before the vendor tells you anything. Detection and response services such as Exodus Aria ADR and endpoint coverage through EDR support that visibility; our help desk impersonation analysis shows how fast trust in one channel becomes broad access.
Keep your own copy and your own path
Hold a recoverable copy of critical records outside the vendor, and keep a network path that does not depend on one carrier or cloud. Backup and recovery, immutable backups, a private or hybrid cloud and a resilient SD-WAN design all shrink how much one provider’s bad day becomes yours. Orphaned circuits complicate every incident, which is why our telecom expense management guide pairs audit discipline with security.
An honest note: we have no inside knowledge of how the Sageworks incident began, and nothing here claims any product would have prevented it. The goal is narrower: limit what a vendor connection can reach, and shorten the time it takes to operate without it.
Sector Lens: Banks, Credit Unions, Insurers and Healthcare
- Community banks and credit unions: run the kill-switch test on lending, core and payment vendors, and confirm your workflow can meet the 36-hour (bank) or 72-hour (credit union) clock from a vendor’s first notice.
- Insurers: map claims, underwriting and document platforms to state data security laws modeled on the NAIC law, and ask vendors for fourth-party lists.
- Healthcare: treat revenue-cycle, imaging and cloud EHR vendors as critical and test downtime procedures. Our end-of-support edge devices post covers a related exposure inside your own perimeter.
A 30-Day Third-Party Risk Management Plan
| Week |
Action |
Output |
| 1 |
List every vendor whose three-day outage would stop a customer-facing process; assign an owner and an emergency contact to each |
Critical vendor register |
| 2 |
Run the five-question kill-switch test on your top three vendors as a two-hour tabletop |
Gap list ranked by customer impact |
| 3 |
Inventory and rehearse rotation of vendor API keys and service accounts; confirm alternate customer intake channels |
Rotation runbook; fallback procedure |
| 4 |
Review contract notice clauses and renewal dates; brief the board or risk committee on residual exposure |
One-page board summary; renewal asks |
What We Still Don’t Know
Several facts remain unclear from public reporting: how the unauthorized access occurred, whether any customer data was taken, how many institutions were affected, and exactly when borrower-facing features fully returned. Abrigo told American Banker the incident was contained but has not said whether data left its environment. Until that is clarified, third-party risk management teams should request written confirmation of scope, integrity checks and indicators of compromise, and document your own timeline. Facts here reflect public reporting through November 12, 2026 and may change.
Frequently Asked Questions About Third-Party Risk Management
What is third-party risk management?
Third-party risk management is the process of identifying, assessing, contracting for, monitoring and exiting vendor relationships. In U.S. banking it follows the five-stage life cycle in the 2023 interagency guidance.
What happened to Abrigo Sageworks?
Abrigo disabled Sageworks on October 30, 2026 after detecting irregular activity. Most services returned November 2. Abrigo later confirmed a contained data security incident involving unauthorized access.
Does a vendor shutdown mean a data breach?
Not by itself. Here unauthorized access was confirmed, but reporting has not said whether data was taken, so ask for evidence rather than assuming.
What incident-notification rules apply to banks and vendors?
Banks must notify their primary federal regulator within 36 hours of determining a notification incident occurred. Bank service providers must notify affected banks as soon as possible after an incident causing or likely to cause a material disruption of four or more hours. Credit unions follow NCUA’s 72-hour rule.
Which contract terms matter most?
Notification clocks with named contacts, audit rights, subcontractor disclosure, recovery objectives, data return and deletion, and termination assistance.
How can network architecture reduce vendor-outage risk?
Strong third-party risk management segments each vendor connection, scopes and rotates credentials, encrypt data under keys you control, monitor vendor traffic for anomalies, and keep recoverable copies and alternate paths. These steps limit reach and speed recovery; they do not prevent a vendor’s own incident.
Is Your Next Vendor Shutdown Already Scheduled?
ibm/SEIMless Communications Technologies, Inc. and Exodus QRN, Inc. help financial services, healthcare and insurance organizations pair third-party risk management with networks that keep serving customers when a provider cannot. Let’s map your critical vendors and run your first kill-switch test together.
Get StartedContact Us
Call: 646-546-5245
Email: in**@**********ss.com
Address: One Liberty Plaza, New York, NY 10006
Sources and Further Reading
by hannahadmin | Oct 15, 2026 | blog, cybersecurity, Cybersecurity Awareness Month 2026, Network Security
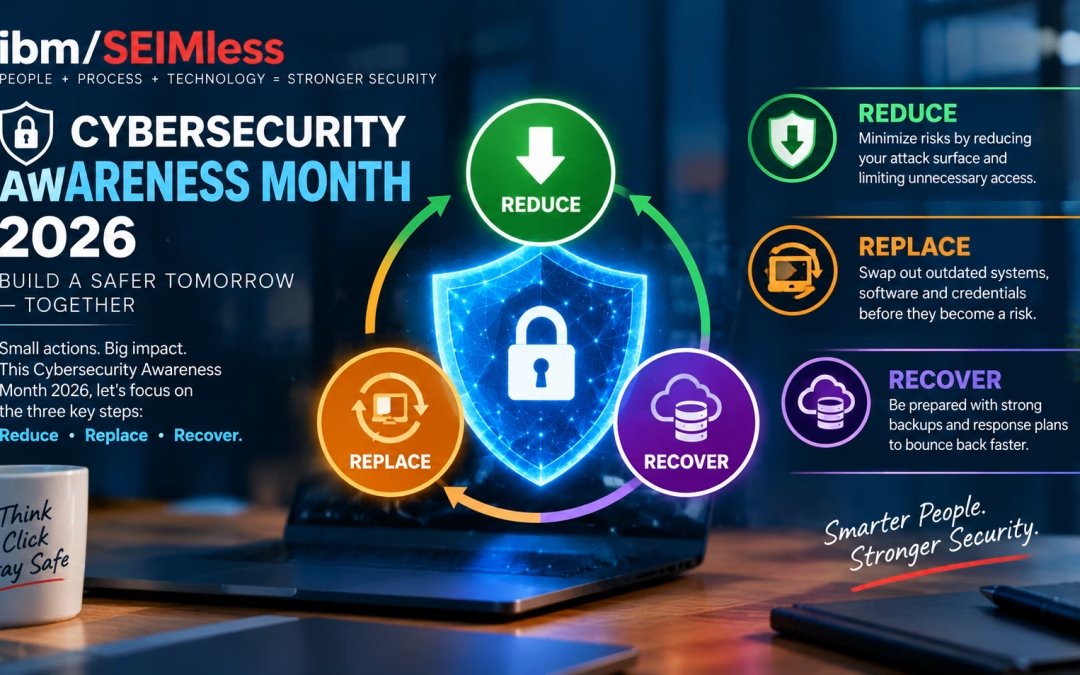
Cybersecurity Awareness Month 2026 is about halfway done, and most enterprises have already sent the posters, the phishing quiz, and the reminder about strong passwords. Those habits matter. But this year’s campaign carries a second, quieter message aimed at the people who run networks: CISA’s “Securing the Next 250” asks organizations to practice the 3Rs of cybersecurity: Reduce, Replace, Recover. With about two weeks left in October, this guide turns that slogan into a concrete plan for your network, your devices, and your recovery capability.
| What is Cybersecurity Awareness Month?
Cybersecurity Awareness Month is the annual October campaign led by the U.S. Cybersecurity and Infrastructure Security Agency (CISA) and the National Cybersecurity Alliance. The 2026 edition, the 23rd, runs October 1–31 under two themes: CISA’s “Securing the Next 250,” which asks organizations to reduce attack surfaces, replace end-of-support technology, and recover quickly, and the Alliance’s “Don’t Make It Easy for Them,” which focuses on everyday security habits. |
| Key Takeaways
Cybersecurity Awareness Month 2026 runs two themes: CISA’s “Securing the Next 250” and the Alliance’s “Don’t Make It Easy for Them.”
The 3Rs map directly to network work: shrink exposure, retire unsupported systems, and rehearse recovery.
Awareness changes behavior; architecture decides whether a mistake becomes a breach. We call the distance between them the awareness-to-architecture gap.
Several Microsoft products hit end of support on October 13, 2026, and the copper phone network is being retired on a published schedule.
You can finish a meaningful 3Rs sprint before October 31. |
Cybersecurity Awareness Month 2026: Two Themes, One Message
The National Cybersecurity Alliance’s theme, “Don’t Make It Easy for Them,” frames security as small, repeated habits: unique passwords, multifactor authentication, spotting phishing, and installing updates. CISA’s theme looks further out. Tied to America’s 250th anniversary, “Securing the Next 250” aims at critical infrastructure owners and the vendors that serve them, as Industrial Cyber summarized it. CISA’s awareness month toolkit offers free messaging and graphics for both.
The HIPAA Journal’s coverage points out that securing critical infrastructure is a national priority under the White House’s March 2026 Cyber Strategy for America. That elevates the 3Rs of Cybersecurity Awareness Month 2026 from a slogan to a statement of national expectations. If your business supplies hospitals, banks, utilities, or government agencies, your customers will soon expect you to practice them.
The Awareness-to-Architecture Gap
Here is the uncomfortable truth behind Cybersecurity Awareness Month 2026: training raises the odds that an employee does the right thing, but it cannot make every employee right every time. Attackers know it. Clark Hill’s analysis notes that Mandiant has seen traditional email phishing decline as an initial infection vector from 2022 through 2025, while voice phishing and text phishing have risen. Users are now being attacked through channels no email filter watches.
The awareness-to-architecture gap is the distance between what people are told to do and what the environment lets happen when they do not. Closing it means building networks where one bad click, one stolen password, or one unpatched appliance does not hand over the whole company. The 3Rs are CISA’s blueprint for exactly that.
Reduce: Shrink the Attack Surface Before Attackers Find It
CISA’s first R asks organizations to keep systems current, patch promptly, and cut unnecessary exposure. It also warns that defenders are overwhelmed: total CVEs published in 2026 passed the entire 2025 total by the end of August, so the advice is to patch smarter by prioritizing known-exploited flaws. This week made the point vividly. Microsoft released fixes for a record 1,400-plus vulnerabilities, and an Ivanti VPN zero-day let an attacker bypass a fully patched device. Cybersecurity Awareness Month 2026 landed in the middle of that surge. We break down the prioritization model in Risk-Based Vulnerability Management; here is how Reduce looks in network terms.
- Inventory what is exposed. You cannot reduce a surface you have not mapped. List internet-facing gateways, firewalls, VPNs, and remote-management tools.
- Remove what you do not need. Retire dormant VPN accounts, unused ports, and forgotten test systems.
- Segment aggressively. Use SD-WAN and Exodus NxtGen Firewall policies so a compromised branch or device cannot reach everything.
- Verify, then trust. Adopt Zero Trust Content Security, guided by CISA’s Zero Trust Maturity Model.
- Watch the endpoints. Endpoint detection and response catches what training and filters miss.
CISA also lists basic measures for every business: phishing education, stronger passwords, multifactor authentication, and prompt updates, followed by system logging, backups, encryption at rest and in transit, an incident response plan, reporting incidents to CISA, and preparing for disruptions. Its small and medium business guidance and the Cross-Sector Cybersecurity Performance Goals turn those into checklists.
Replace: Retire Technology That No Longer Gets Security Updates
The second R is the one most budgets avoid. When software or hardware reaches end of support, vendors stop shipping fixes, and every new vulnerability becomes permanent. CISA’s BOD 26-02 addresses this specifically for edge devices at the network boundary, where an unsupported appliance is an open door.
The calendar is not abstract. According to TechRepublic and Windows Report, Windows 11 version 24H2 Home and Pro, Windows 10 Enterprise LTSB 2016, and the Office, Visio, and Project LTSC 2021 releases all reached end of support on October 13, 2026, and Windows 11 23H2 Enterprise and Education follow on November 10. Use Microsoft’s lifecycle database to check every build you run.
| What is ending |
Date |
What to do |
| Windows 11 24H2 Home/Pro, Windows 10 LTSB 2016, Office LTSC 2021 |
Oct 13, 2026 |
Upgrade, or isolate and monitor until you can |
| Windows 10 ESU Year 1 coverage |
Oct 13, 2026 |
Decide on Year 2, upgrade, or desktop-as-a-service; see our Windows 10 ESU decision guide |
| IBM i 7.4 standard support |
Sep 30, 2026 (extended support to Sep 30, 2029) |
Plan the move; see IBM i Modernization in 2026 |
| Copper POTS lines |
AT&T shutoffs begin Nov 15, 2026 |
Migrate life-safety lines; see POTS Line Replacement |
| Windows 11 23H2 Enterprise/Education |
Nov 10, 2026 |
Schedule upgrades before the next Patch Tuesday |
“Replace” does not always mean buying new hardware. Desktop-as-a-Service can move aging endpoints off the risk list, private and hybrid cloud can retire fragile on-premises servers, and a managed carrier migration, such as the MPLS replacement path, can remove legacy circuits. Where replacement must wait, isolate the system, restrict its traffic, and monitor it closely, because an unsupported device that cannot be patched must be contained.
Recover: Assume a Failure, Then Prove You Can Bounce Back
Of the 3Rs in Cybersecurity Awareness Month 2026, Recover is the one most easily faked on paper.
CISA’s third R reflects a hard-won lesson: some attacks will succeed. The agency urges owners and operators to build isolation and recovery capability so vital systems keep running in an isolated state while compromised systems are restored. Its CI Fortify initiative applies the same logic to operational technology in a geopolitical conflict. Recovery is where many “we have backups” claims fall apart, because backups were never tested, never isolated, or reachable by the same stolen administrator credential that started the incident.
- Make backups immutable. Follow the design in our immutable backups guide and the backup and recovery service so ransomware cannot delete your restore points.
- Rank your systems by recovery priority. Define recovery time and recovery point objectives for each, using NIST SP 800-34 on contingency planning.
- Practice the restore. Run a tabletop and at least one real restore before year end, and time it.
- Protect data even if it is stolen. Encryption through Data at Rest and Data in Motion controls limits what attackers can use.
- Know who you will call. Keep CISA’s #StopRansomware resources and the FBI’s Internet Crime Complaint Center in your response plan, and report incidents to CISA at gov/report.
A 16-Day Sprint to Finish Cybersecurity Awareness Month 2026 Strong
If your Cybersecurity Awareness Month 2026 plan started late, compress the work. Every item below can begin before October 31.
| Dates |
Focus |
Deliverable |
| Oct 15–18 |
Reduce |
List of internet-facing assets and the KEV-listed flaws on them |
| Oct 19–23 |
Replace |
End-of-support inventory with owner, date, and plan per system |
| Oct 24–28 |
Recover |
Immutability check on backups and one timed test restore |
| Oct 29–31 |
Report |
One-page 3Rs scorecard for leadership and your board |
For small teams, the FTC’s small business cybersecurity resources and the NIST Cybersecurity Framework provide structure without requiring a dedicated security department.
Beyond Cybersecurity Awareness Month 2026: Encryption for the Next 250
A campaign built around the next 250 years should make leaders ask how long today’s secrets must stay secret. Adversaries can copy encrypted traffic now and decrypt it when quantum computers mature, a threat we explain in Harvest Now, Decrypt Later. The federal deadlines in Executive Order 14412 already put a clock on migration, and our post-quantum migration playbook shows where to start. Add an encryption-inventory line to your 3Rs scorecard now, and consider Exodus QRN quantum-resistant networking for data with a long confidentiality life.
Industry Lens: Where the 3Rs Hit Hardest
Financial services teams juggle voice-phishing fraud, third-party risk, and strict recovery expectations, so Recover and exposure reduction lead their plans. Healthcare providers carry the heaviest Replace burden because long-lived clinical devices outlast their software support; start with segmentation and our guidance on medical device cybersecurity. Insurance carriers and their brokers should expect underwriting reviews of end-of-support inventories and backup immutability. In all three, Cybersecurity Awareness Month 2026 guidance applies to the vendors and partners you depend on are part of your attack surface, which is why CISA’s guidance reaches the supply chain as well as the operators.
Turn Cybersecurity Awareness Month 2026 Into a Year-Round Program
Cybersecurity Awareness Month 2026 works only if it leaves something behind: an inventory, a policy, a tested plan. Adaptive Security recommends measuring behavior, such as how often and how quickly employees report suspicious messages, rather than counting completed trainings. Absolute Security adds that the 3Rs start with knowing which devices qualify, a reminder that visibility precedes every other control. Pair those people metrics with the network metrics above, and your next board report will show both halves of the gap closing. The Alliance’s own StaySafeOnline resources offer year-round material for staff.
For Cybersecurity Awareness Month 2026 and beyond, ibm/SEIMless helps organizations connect those halves: managed network and security services, next-gen network security, and quantum-resistant infrastructure designed for the Reduce, Replace, and Recover work above.
Cybersecurity Awareness Month 2026 FAQ
What is the theme of Cybersecurity Awareness Month 2026?
There are two. CISA’s theme is “Securing the Next 250,” which pairs with the 3Rs of cybersecurity (Reduce, Replace, Recover), and the National Cybersecurity Alliance’s theme is “Don’t Make It Easy for Them.” The month runs October 1–31, 2026.
What are the 3Rs of cybersecurity?
CISA’s 3Rs are Reduce attack surfaces by patching and prioritizing, Replace end-of-support devices and software, and Recover quickly by practicing plans that sustain operations after an incident.
Is Cybersecurity Awareness Month only for critical infrastructure?
No. CISA aims the 3Rs at critical infrastructure owners and operators, but it encourages every business to adopt basics such as phishing education, multifactor authentication, prompt updates, backups, encryption, and an incident response plan.
What reached end of support on October 13, 2026?
Reporting from TechRepublic and Windows Report lists Windows 11 24H2 Home and Pro, Windows 10 Enterprise LTSB 2016, and Office, Visio, and Project LTSC 2021. Windows 11 23H2 Enterprise and Education follow on November 10, 2026.
What is the awareness-to-architecture gap?
It is the distance between what employees are trained to do and what the network allows when they make a mistake. Closing it means segmentation, zero trust access, endpoint detection, immutable backups, and encryption so one error does not become a breach.
How can ibm/SEIMless support the 3Rs?
ibm/SEIMless provides next-gen network security, SD-WAN, backup and recovery, private and hybrid cloud, desktop-as-a-service, and Exodus quantum-resistant networking. Call 646-546-5245 or email in**@**********ss.com to start a conversation.
| Ready to Strengthen Your Network? Talk to ibm/SEIMless
Since 2001, ibm/SEIMless Communications Technologies, Inc., home of Exodus QRN, has helped medium and enterprise organizations across the U.S. and Canada design secure, vendor-agnostic networks. Book a free consultation and we will map your exposure, your recovery readiness, and your next best step.
Get Started Contact Us
Phone: 646-546-5245
Email: in**@**********ss.com
Headquarters: One Liberty Plaza, New York, NY 10006
Learn more: About Us · FAQs · Services · Blog |