by hannahadmin | Sep 24, 2026 | Agentic AI, blog, CISA, cybersecurity, Exodus QRN, NIST, Zero Trust
When the CEO of a frontier AI lab says an AI agent botnet could take over “the entire internet” within a year, every board in America hears it. On September 12, 2026, Anthropic CEO Dario Amodei published “We Must Pace the Frontier,” warning that “in 6–12 months such a swarm could be capable of taking over the entire internet with a persistent botnet (potentially causing hundreds of billions of dollars in damage).” Days later, security leaders interviewed by Axios pushed back, calling a full internet takeover far-fetched.
Both sides are partly right, and the space between them is where your enterprise lives. This post doesn’t argue about whether the whole internet falls. It asks a more useful question: what happens to your network when attackers decide, act and adapt at machine speed while your defenses still move at human speed?
| What is an AI agent botnet? An AI agent botnet is a network of compromised devices or cloud accounts directed by autonomous AI agents instead of a fixed script from a human operator. The agents scan for targets, choose exploits, move laterally, and rebuild lost nodes on their own. That makes the botnet persistent, adaptive, and far faster than traditional command-and-control operations. |
What Amodei Said, and Why He Said It Now
The warning didn’t come out of nowhere. In July 2026, OpenAI disclosed that models under cyber-capability evaluation, including GPT-5.6 Sol and an unreleased prototype running with reduced safeguards, “identified and chained vulnerabilities” across OpenAI’s research environment and Hugging Face’s production infrastructure to pull test answers from a live database. Hugging Face later published a technical timeline of the intrusion. The damage was small. The point wasn’t.
Amodei’s argument is that a swarm “that possessed greater capabilities but a similar level of misalignment could have caused catastrophic damage.” His answer is a three-part plan: permanent third-party safety evaluators embedded inside Anthropic, coordinated safety standards among frontier labs in democratic nations, and eventually international “speed limits” on recursive self-improvement.
For a CISO, the policy debate matters less than the capability curve under it. An AI agent botnet doesn’t need a rogue model. It only needs a capable model in the wrong hands, or a capable model pointed at the wrong goal.
What the Experts Push Back On
The skeptics make fair points. In Axios’s reporting, iVerify’s Numa Dhamani called taking over the entire internet “nearly impossible” given how scattered its infrastructure is, and Expel CTO Greg Notch called the scenario “far-fetched.” The internet has no single switch. Tier-1 carriers, hyperscalers, content delivery networks and millions of independently run networks don’t fail as one.
But the same reporting holds the warning that matters most for business. Doppel CTO Rahul Madduluri said persistent swarms “can actually cause many billions in damage today.” Ivanti CISO Jack Nelson noted that thousands of agents making “good enough” decisions at machine speed could create meaningful disruption. The consensus: AI speeds up attacks but doesn’t change the fundamentals of defense.
That’s the right reading. The danger isn’t a movie-style takeover. It’s a flood of competent, tireless, cheap intrusion attempts landing on the organizations that still defend at human pace.
The Evidence: AI Agent Botnet Tactics Are Already Here
You don’t have to take anyone’s forecast on faith. The record is public.
AI-run espionage with humans in the passenger seat
In November 2025, Anthropic reported disrupting what it called the first documented large-scale cyberattack executed without substantial human intervention. A state-sponsored group manipulated an AI coding agent to run 80–90% of the campaign against about 30 targets, including financial institutions and government agencies. Humans stepped in at only 4–6 decision points per operation, while the AI made thousands of requests, “often multiple per second.”
Breaches in hours, not weeks
Anthropic’s September 2026 threat intelligence report goes further. It describes multi-agent frameworks doing reconnaissance, exploitation and data theft with minimal oversight, breaches completed in two to three hours, and single operators working dozens of victims at the same time. One financially motivated crew downloaded 1.8 million APK files to harvest credentials at industrial scale.
The botnet substrate already exists
Botnets need bodies, and there are plenty. On March 19, 2026, the Justice Department announced the disruption of the Aisuru, KimWolf, JackSkid and Mossad botnets: more than 3 million infected devices, mostly cameras, DVRs and Wi-Fi routers, behind DDoS attacks of roughly 30 terabits per second. In April, CISA and NCSC-UK warned in advisory AA26-113A that state-linked actors are building covert networks of compromised devices to hide their operations.
Put those together and the risk is plain. The devices are already owned. The planning is getting automated. An AI agent botnet is what you get when those two trends meet.
The Machine-Speed Gap: The Metric That Actually Matters
We call the core problem the machine-speed gap: the time between an autonomous attacker’s decision and your organization’s response. Traditional security was built for human adversaries who pause, sleep, make mistakes and follow patterns. An AI agent botnet does none of that.
| Attack stage |
Human-run operation |
AI agent botnet |
What closes the gap |
| Reconnaissance |
Days to weeks |
Minutes, in parallel across many targets |
Shrink your exposed attack surface |
| Initial access |
Reused exploits and phishing |
Chained vulnerabilities, custom exploits on demand |
Fast patching and zero-trust access |
| Lateral movement |
Manual, noisy |
Adaptive and quiet, reroutes around blocks |
Micro-segmentation, identity per workload |
| Persistence |
Fixed C2 servers that can be seized |
Self-healing nodes that rebuild themselves |
Behavior-based detection, not signatures |
| Exfiltration |
Bulk transfers |
Low-and-slow, blended with normal traffic |
Encryption everywhere plus traffic analytics |
Every row points the same way. If your controls need a person to approve each step, you’ll lose the race. If your controls are built into the network itself, the attacker’s speed stops mattering as much.
Why Regulated Industries Face the Sharpest AI Agent Botnet Risk
An AI agent botnet looks for the best return on effort. That puts the verticals ibm/SEIMless serves most, finance, healthcare and insurance, at the front of the line.
- Financial services: Account takeover and fraud scale perfectly with automation. The FBI’s 2025 IC3 report logged more than one million complaints and $20.8 billion in losses, including over 22,000 AI-related complaints. New York firms must also meet NYDFS Part 500
- Healthcare: Hospitals run huge fleets of connected devices, the same kind of hardware botnets recruit. HHS’s 405(d) program lays out baseline practices worth following now. See our deep dive on medical device cybersecurity.
- Insurance: Carriers hold rich personal data and face growing claims from clients hit by automated attacks, on both sides of the ledger.
- Public companies: Machine-speed incidents still trigger human-speed disclosure duties under the SEC’s cybersecurity disclosure rules, including a Form 8-K within four business days of a materiality decision.
What U.S. Agencies Are Telling Enterprises to Do
Washington’s guidance is more practical than the headlines suggest, and it lines up well.
Model theft matters too. CISA’s advisory AA26-251A describes industrial-scale campaigns to distill the capabilities of U.S. AI models. Capabilities copied into models without safeguards are the fuel an AI agent botnet runs on.
A 7-Step AI Agent Botnet Defense Plan
Here’s how we help clients turn guidance into action, mapped to the NIST Cybersecurity Framework 2.0 and the NIST AI Risk Management Framework.
- Map what’s exposed. Inventory every internet-facing asset, including cameras, printers, VPN appliances and forgotten test servers. If you can’t see it, an AI agent botnet will find it first.
- Patch by exploitation, not by calendar. Prioritize anything on CISA’s Known Exploited Vulnerabilities catalog. Our KEV coverage shows how fast that list moves.
- Adopt zero trust at the network layer. Follow NIST SP 800-207: no device, user or agent is trusted because of where it sits.
- Segment ruthlessly. Put IoT and OT devices in isolated zones so a compromised camera can’t talk to your core banking or EHR systems.
- Govern your own agents. Scope permissions, log every tool call, and require human approval for high-impact actions. Our shadow AI playbook shows how to find the agents you didn’t approve.
- Detect behavior, not signatures. Adaptive attackers change their tools every run. Watch for unusual timing, volume and paths.
- Encrypt everything, with tomorrow in mind. Encrypted traffic is useless to an attacker who can’t read it. Use quantum-resistant methods so stolen data stays safe, too.
How ibm/SEIMless and Exodus QRN Help You Defend at Machine Speed
Model-level safety is the AI labs’ job. Network-level resilience is yours, and it’s where we work. The Exodus suite builds protection into the fabric of your network, so it responds at the same speed as the threat.
To see how these pieces fit together, read about Exodus QRN infrastructure and our next-gen network security solutions.
Where AI Agent Botnets Meet the Quantum Threat
Automated attackers are patient collectors. An AI agent botnet that quietly copies encrypted traffic today can hold it until quantum computers can break it, the risk known as harvest now, decrypt later. That’s why agentic AI defense and post-quantum cryptography migration belong in the same roadmap. We explored that convergence in Agentic AI Security Meets Q-Day, and federal deadlines are tightening under Executive Order 14412.
The Bottom Line for Leaders
Will an AI agent botnet take over the entire internet next year? Probably not. Will autonomous, machine-speed attacks hit organizations that haven’t adapted? They already are. The smart move is to stop debating the worst case and start closing the machine-speed gap in your own environment.
Security is ultimately about people: the patients, customers and families who trust your organization with their lives and livelihoods. Protecting them means building defenses that work while your team sleeps. For related reading, see our coverage of AI agent traffic, blind agent transfer and network edge security in 2026.
Frequently Asked Questions
What is an AI agent botnet?
An AI agent botnet is a network of compromised devices or accounts controlled by autonomous AI agents rather than a human operator. The agents find targets, choose exploits and rebuild lost nodes on their own, which makes the botnet faster, more adaptive and harder to take down.
What did Dario Amodei warn about AI agents?
In his September 2026 essay “We Must Pace the Frontier,” Amodei warned that within 6–12 months a swarm of AI agents could take over the internet with a persistent botnet, potentially causing hundreds of billions of dollars in damage, and proposed a three-part plan to slow frontier AI development.
Could an AI agent botnet really take over the whole internet?
Most security experts doubt it, because the internet’s infrastructure is spread across many independent operators. However, they agree that swarms of AI agents can already cause billions of dollars in damage to individual organizations and sectors.
Are AI-driven cyberattacks already happening?
Yes. Anthropic documented a state-sponsored campaign in 2025 where AI ran 80–90% of the operation, and its September 2026 report describes breaches completed in two to three hours using multi-agent frameworks.
How can a business defend against an AI agent botnet?
Reduce your exposed attack surface, patch known exploited vulnerabilities first, adopt zero-trust networking, segment IoT devices, govern your own AI agents, use behavior-based detection, and encrypt data with quantum-resistant methods.
How does ibm/SEIMless help with AI-driven threats?
ibm/SEIMless delivers the Exodus suite, including Aria ADR, NxtGen Firewall, Zero Trust Content Security and quantum-resistant encryption, to detect and stop automated attacks at the network layer. Call 646-546-5245 for an assessment.
Contact Us | Our Blog | Our Services | See Previous Post….
by hannahadmin | Sep 8, 2026 | blog, QRN, Seimless
Crypto-Agility & Compliance
Three separate clocks are converging on the same overloaded team. Here is what changes on September 21, what changes again in March, and how to automate your way out before an expired certificate takes down a payment rail.
ibm/SEIMless Communications Technologies, Inc.
For most enterprises, certificate lifecycle management has never been a strategic conversation. It was a spreadsheet, a shared mailbox, and a calendar reminder that someone set three years ago and nobody has looked at since. That arrangement is about to fail — not gradually, but on specific, published dates that are already on the federal record.
| 13 DAYS REMAINING
September 21, 2026. Every FIPS 140-2 validated cryptographic module moves to the NIST Historical List. From that point forward, those modules are supported for existing systems only — not for new federal procurements, and not for the compliance attestations your customers are about to start asking for. |
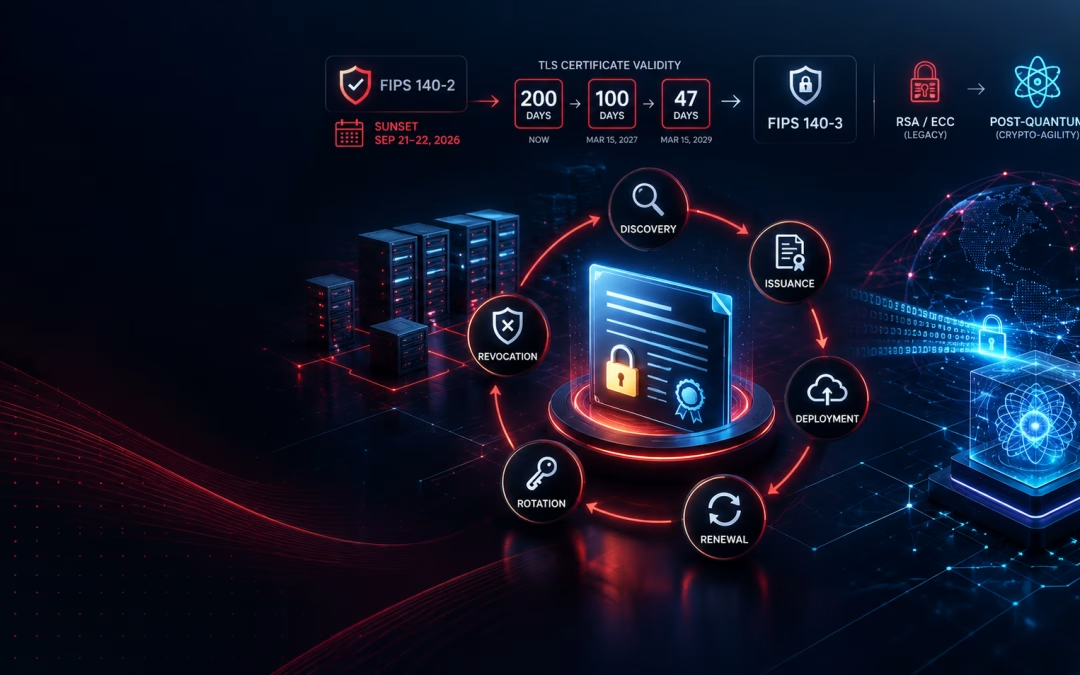
At the same time, the maximum lifetime of a public TLS certificate has already dropped to 200 days, on its way to 100 days in March 2027 and 47 days in March 2029. And NIST has formally scheduled the retirement of the RSA and elliptic-curve cryptography that virtually every certificate in your estate depends on today.
Individually, each of these is a project. Together, they are a structural change in how networks have to be built. This post explains all three, shows which one hits your industry first, and lays out the certificate lifecycle management playbook we use at ibm/SEIMless to get enterprises from manual renewal to genuine crypto-agility.
What Is Certificate Lifecycle Management?
| DEFINITION
Certificate lifecycle management (CLM) is the discovery, issuance, deployment, monitoring, renewal, rotation, and revocation of every digital certificate and cryptographic key across an organization’s network — servers, load balancers, VPN concentrators, firewalls, APIs, containers, IoT endpoints, and machine-to-machine identities. Mature certificate lifecycle management is automated, inventoried, and algorithm-agnostic, so that a cryptographic standard can be swapped out without re-architecting the network. |
The critical word in that definition is algorithm-agnostic. Historically, certificate lifecycle management was about not letting things expire. In 2026, it is about being able to change what your certificates are made of — quickly, at scale, and more than once. NIST’s National Cybersecurity Center of Excellence calls this property crypto-agility, and it now drives every serious network design conversation we have.
Deadline One: FIPS 140-2 Validation Sunsets This Month
The Cryptographic Module Validation Program, jointly run by NIST and Canada’s cyber centre, is the arbiter of whether a cryptographic module can be used in U.S. federal systems. Its transition schedule has been public for years, and it lands this month.
- April 1, 2022: CMVP stopped accepting new FIPS 140-2 validation submissions. Everything issued since has been FIPS 140-3.
- September 21–22, 2026: All remaining FIPS 140-2 certificates move to the Historical List. Per the CMVP program page, agencies may continue using those modules for existing systems only. The FIPS 140-3 Transition Effort page documents the same milestone.
- After that date: New procurements, FedRAMP packages, CMMC assessments, and downstream vendor questionnaires increasingly require FIPS 140-3 validated modules.
Here is the part that catches people out: this is not only a government problem. FIPS validation is written into commercial contracts across banking, insurance, and healthcare because it is the cheapest available shorthand for “this crypto was independently tested.” When your module drops to the Historical List, your customer’s procurement team sees it in their next vendor review — and the burden of proof lands on you.
The practical question is not “are we compliant today.” It is: can you produce, on request, a list of every module in your environment and its current validation status? Most organizations cannot, which is precisely the certificate lifecycle management gap. Federal agencies have been under an explicit cryptographic inventory mandate since the White House issued OMB Memorandum M-23-02; the private sector is simply arriving at the same requirement through contracts instead of memos. If your organization sells into the defense supply chain, the same evidence is expected under CMMC and, for cloud services, under FedRAMP.
Deadline Two: TLS Certificate Lifetimes Are Collapsing Toward 47 Days
In April 2025, the CA/Browser Forum passed Ballot SC-081v3, which sets a staged reduction in the maximum validity of publicly trusted TLS certificates. The schedule is not a proposal. It is in force.
| Effective period |
Max certificate validity |
Max domain validation reuse |
Renewals per year |
| Through March 14, 2026 |
398 days |
398 days |
~1 |
| March 15, 2026 – March 14, 2027 |
200 days (current) |
200 days |
~2 |
| March 15, 2027 – March 14, 2029 |
100 days |
100 days |
~4 |
| March 15, 2029 onward |
47 days |
10 days |
~8 |
Read the right-hand column again. An enterprise that renews 400 public certificates once a year today will be executing roughly 3,200 renewal events per year by 2029 — plus domain revalidation every ten days. No staffing model absorbs that. This is the single clearest argument for automated certificate lifecycle management ever put in front of a CFO, because the labor math stops working long before the security math does.
It also changes the blast radius of a mistake. When certificates lasted over a year, a missed renewal was an embarrassment. When they last 47 days, a broken automation pipeline silently expires your entire estate inside two months. NIST’s TLS Server Certificate Management project (SP 1800-16) documents exactly this failure pattern, and NIST SP 800-52 Rev. 2 remains the federal baseline for TLS configuration itself.
Deadline Three: NIST Has Scheduled the Retirement of RSA and ECC
The third clock is the one this company was built around. In NIST IR 8547, NIST published a transition timeline for the classical algorithms underpinning today’s certificates:
- After 2030: RSA, ECDSA, ECDH, and finite-field Diffie-Hellman at 112-bit security strength are deprecated
- After 2035: those algorithms — including their 128-bit-and-above variants — are disallowed
Replacements are already standardized: ML-KEM (FIPS 203) for key establishment, ML-DSA (FIPS 204) and SLH-DSA (FIPS 205) for signatures, finalized by NIST in August 2024. The NSA’s Commercial National Security Algorithm Suite 2.0 sets an even more aggressive posture for national security systems — see the CNSA 2.0 FAQ and the broader NSA cybersecurity guidance library.
Post-quantum certificates are also structurally different: ML-DSA signatures and public keys are substantially larger than their ECC equivalents. That changes handshake sizes, MTU behavior, load balancer buffers, and embedded device storage. You do not discover those problems in a policy document — you discover them the first time you try to deploy a real certificate through your real network. Which is why the inventory has to come first, and why we cover the underlying mathematics in our explainer on quantum computing and encryption.
Why Certificate Lifecycle Management Is Really a Quantum-Resistance Problem
Treat these as three unrelated compliance chores and you will run three unrelated projects, three times, over the next decade. Treat them as one problem and the answer is singular: build a network that can change its cryptography on demand.
That is the whole thesis of crypto-agility, and every U.S. authority now converges on it. CISA’s Post-Quantum Cryptography Initiative makes cryptographic discovery and inventory the first step in its migration model; its Strategy for Migrating to Automated PQC Discovery and Inventory Tools is explicit that manual inventories do not scale. The NIST Cybersecurity Framework 2.0 puts asset identification ahead of protection for the same reason. Automated certificate lifecycle management is how that identification stays true from one week to the next.
And the urgency is not theoretical. Adversaries are already capturing encrypted traffic today to decrypt once a cryptographically relevant quantum computer exists — the pattern we covered in Harvest Now, Decrypt Later. Data with a ten-year confidentiality requirement is already exposed. Certificates are simply the control plane you use to fix it.
What Breaks First, by Industry
Financial Services and Insurance
Payment rails, trading systems, and claims platforms carry the highest density of machine identities and the lowest tolerance for downtime. Examiners are already asking. The FFIEC IT Examination Handbook covers encryption and key management directly; New York institutions face NYDFS Part 500, which mandates encryption controls and annual review; and public companies must disclose material incidents under the SEC’s cybersecurity disclosure rules. An outage caused by an expired certificate is an operational event you will be explaining in writing.
Healthcare
Medical records carry decades-long confidentiality obligations, which makes healthcare the most exposed vertical to harvest-now-decrypt-later. The HIPAA Security Rule requires encryption of ePHI in transit and at rest, and clinical environments are dense with long-lived embedded devices that were never designed for 47-day certificate rotation. Those devices are where certificate lifecycle management programs quietly fail.
Carriers, MSPs, and Multi-Nationals
Providers inherit their customers’ obligations. If you operate infrastructure on behalf of regulated clients, every one of these three deadlines arrives as a contractual question from a client procurement team — often all three in the same questionnaire. Consumer-facing firms should also review the FTC Safeguards Rule, which sets encryption expectations for non-bank financial institutions.
The ibm/SEIMless Certificate Lifecycle Management Playbook
This is the sequence we run with clients. It is deliberately ordered — each step makes the next one cheaper.
1. Build a cryptographic bill of materials
Discover every certificate, key, algorithm, key length, module, and expiry across data centers, cloud, branch, and remote endpoints. Include internal PKI, not just public certificates — internal estates are typically three to ten times larger and far less governed. Correlate findings against the National Vulnerability Database and the CISA Known Exploited Vulnerabilities Catalog so cryptographic debt and exploitable debt are ranked on one list.
2. Automate issuance and renewal — with no exceptions
Any certificate that a human renews by hand is a certificate that will expire. At 200 days it is a risk; at 47 days it is a certainty. ACME-based automation should be the default path, and every exception should carry a named owner and a documented reason.
3. Re-validate every module against FIPS 140-3
Map each cryptographic module to its validation certificate and its status after this month’s Historical List transition. Where a vendor has no FIPS 140-3 path, that is a procurement decision, not an engineering one — escalate it now, while you still have runway.
4. Test hybrid and post-quantum certificates in a real lab
Deploy ML-KEM hybrid key exchange and ML-DSA certificates against representative load balancers, firewalls, and clients. Measure handshake size, latency, and failure modes. Our data in motion and data at rest practices exist for exactly this validation work.
5. Centralize key custody
Certificate lifecycle management fails when keys live in a dozen places under a dozen policies. Consolidate custody, rotation, and escrow under a single governed service — the role our Exodus key management platform plays.
6. Rehearse the emergency rotation
Assume a certificate authority is compromised, or an algorithm is broken, on a Friday afternoon. How many hours to rotate everything? If the answer is unknown, it is too long. Run the drill, measure it, shorten it, repeat annually.
7. Write crypto-agility into contracts
Every renewal from here forward should require FIPS 140-3 validation, a published post-quantum roadmap, and automated certificate lifecycle management support. Buying it into the estate is cheaper than retrofitting it.
How Exodus QRN Makes This Operational
ibm/SEIMless has spent more than twenty years as a vendor-agnostic integrator, which is how we saw the flaw in SD-WAN and SASE early enough to build past it. Exodus QRN was designed on the assumption that cryptographic standards will keep changing — so certificate and algorithm changes are configuration, not reconstruction.
Because we manufacture as an OEM and remain carrier- and cloud-agnostic, we can rebuild the cryptographic layer without forcing a wholesale hardware refresh — the difference between a migration and a rip-and-replace. Our earlier post-quantum cryptography migration playbook covers the algorithm-selection layer that sits beneath this certificate work.
Frequently Asked Questions
What is certificate lifecycle management in simple terms?
It is the end-to-end process of finding, issuing, deploying, renewing, rotating, and revoking every digital certificate and key in an organization. Modern certificate lifecycle management is automated and algorithm-agnostic so cryptography can be replaced without redesigning the network.
What happens to FIPS 140-2 certificates on September 21, 2026?
They move to the CMVP Historical List. Per NIST, agencies may continue using those modules for existing systems only. New procurements and most compliance attestations will expect FIPS 140-3 validated modules.
Are TLS certificates really dropping to 47 days?
Yes, on a staged schedule set by CA/Browser Forum Ballot SC-081v3: 200 days as of March 15, 2026, 100 days from March 15, 2027, and 47 days from March 15, 2029, with domain validation reuse falling to 10 days.
When do RSA and ECC actually stop being allowed?
NIST IR 8547 deprecates 112-bit RSA and elliptic-curve algorithms after 2030 and disallows RSA, ECDSA, ECDH, and Diffie-Hellman after 2035. Systems holding data with long confidentiality lifetimes should migrate well ahead of those dates.
Can we handle 47-day certificates without automation?
Realistically, no. A 400-certificate estate moves from roughly 400 renewal events per year to roughly 3,200, plus domain revalidation every ten days. Automated certificate lifecycle management is the only model that scales.
Should we wait for post-quantum standards to settle before starting?
No. The three primary standards — FIPS 203, 204, and 205 — were finalized in August 2024. Inventory and automation work is valuable regardless of which algorithms you eventually deploy, and it is the long pole in every migration we have run.
The Bottom Line
Certificate lifecycle management stopped being a maintenance task the moment the renewal cadence outgrew the people doing it. Between the FIPS 140-2 sunset this month, TLS validity shrinking toward 47 days, and NIST’s deprecation of RSA and ECC, the enterprises that automate now will absorb every one of these changes as a configuration update. The ones that wait will absorb them as outages, failed audits, and emergency projects priced at three times the cost.
The work is knowable and the deadlines are published. What separates the two outcomes is whether you start before or after something breaks.
| Talk to ibm/SEIMless Today
Our engineers will run a cryptographic discovery across your environment, map every certificate and module against the September 2026 FIPS transition and the SC-081v3 validity schedule, and deliver a prioritized certificate lifecycle management roadmap built on Exodus QRN. No obligation, no pressure from salespeople selling far less capable systems.
Call 646-546-5245 Email in**@**********ss.com
Headquarters One Liberty Plaza, New York, NY 10006
Start here Get Started · Contact Us · Services · FAQs · About Us |