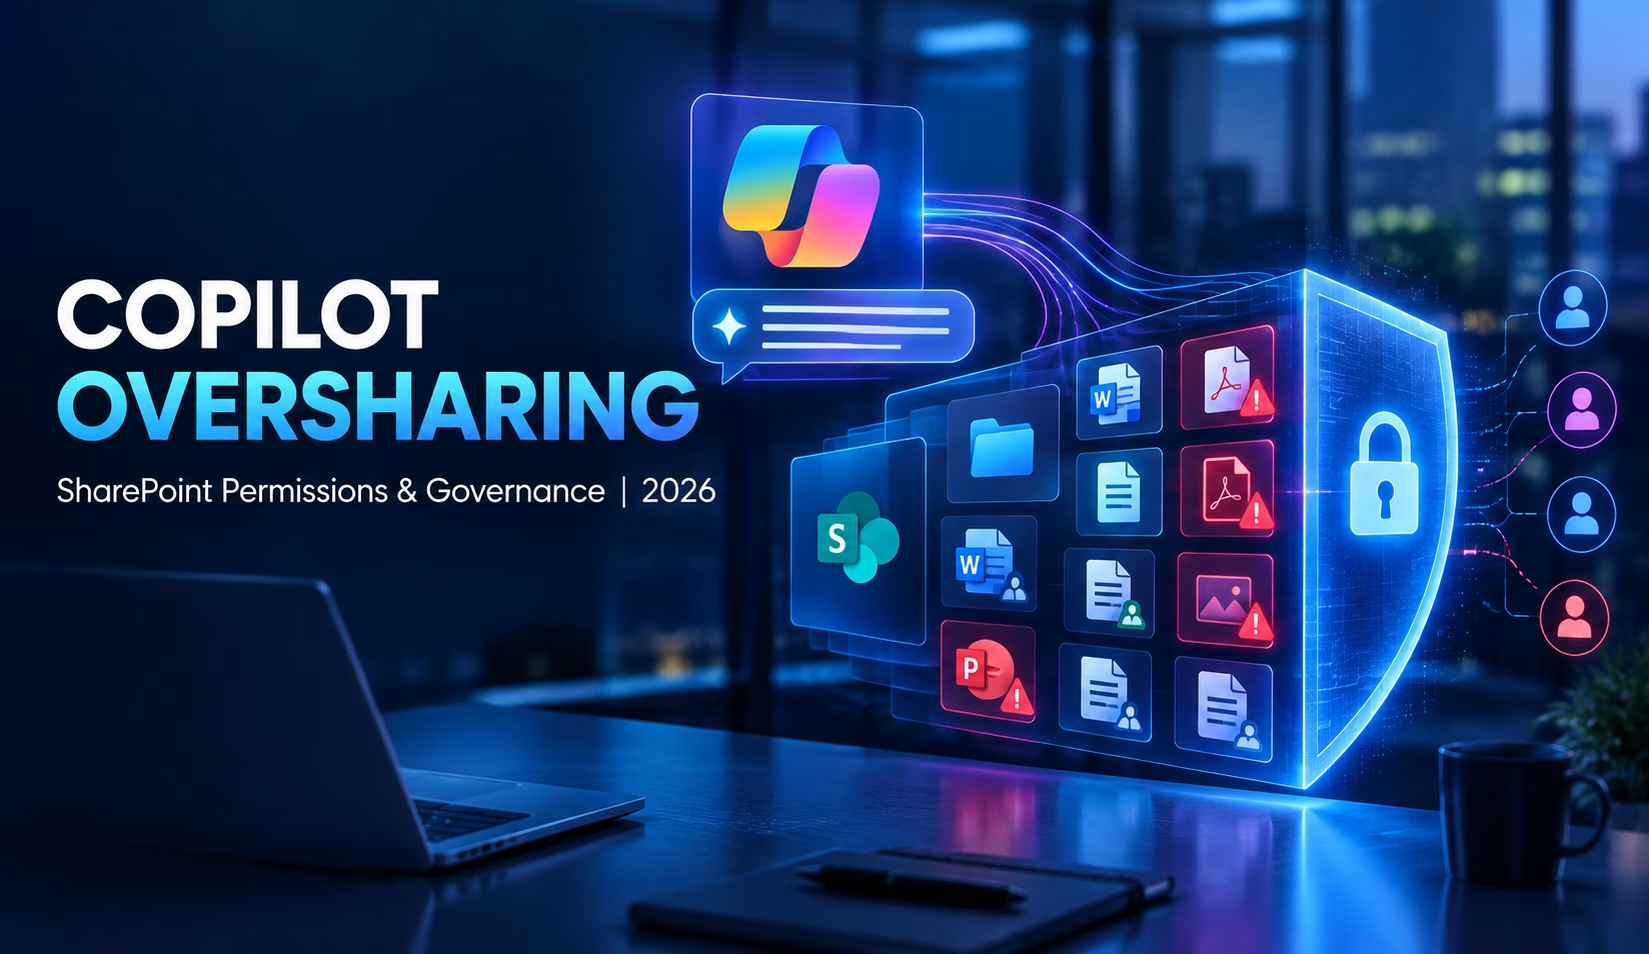
Copilot oversharing is the quiet reason many Microsoft 365 Copilot rollouts stall in security review. Copilot does not break your access rules. It obeys them with perfect, tireless efficiency, and that is the problem: every overly broad SharePoint site, forgotten “everyone” link, and bloated distribution group that was harmless when nobody could find the file is suddenly one natural-language question away from an answer. This guide explains what is driving the issue right now, which Microsoft controls matter, and how to pair them with network-layer protection so a permissions mistake does not become a breach.
Definition: Copilot oversharing is when Microsoft 365 Copilot surfaces files, emails, or chats that a user is technically permitted to open but was never meant to see. It is caused by existing over-permissioned content in SharePoint, OneDrive, and Teams, not by Copilot creating new access.
Key Takeaways
- Microsoft says Copilot only surfaces what a user can already access, so your exposure is the quality of your permissions, labels, and governance.
- We call the accumulated mess permission debt: years of access granted and never revoked. Copilot is the moment the debt comes due.
- Restricted Content Discovery is a temporary tourniquet. The real fix is access reviews, labels, and DLP.
- On-premises SharePoint Server has a separate, exploited-in-the-wild problem. Cleaning permissions does not patch servers, and patching does not clean permissions.
- Network segmentation, encryption, and monitoring are the backstop when a permission slips through.
Why Copilot Oversharing Is Trending This Month
Three developments have put Copilot oversharing on executive agendas in October 2026. First, Microsoft’s own guidance now treats it as the number one deployment blocker. Its Copilot security and governance documentation tells administrators to use Microsoft Purview and SharePoint Advanced Management to assess oversharing risk, including for agents.
Second, the tooling is moving. A roadmap item tracked as ID 559617 reportedly targets October 2026 for putting Purview oversharing visibility and Copilot DLP controls inside the Microsoft 365 admin center for government cloud environments. Third, industry commentary keeps repeating the same uncomfortable gap between confidence and reality: a recent ShareGate report headline put it as “93% confident, 29% already exposed,” and a Channel Dive piece on October 9 framed Copilot as revealing governance lapses rather than causing them.
The common thread is not a new vulnerability. It is a visibility event. Copilot makes the state of your permissions measurable overnight.
Permission Debt: The Concept Behind Copilot Oversharing
Technical debt is shortcuts that compound. Permission debt is the same idea applied to access: every “just give the whole team access” decision, every project site that outlived its project, every group that grew for six years and never shrank. One practitioner guide puts it bluntly, noting that most oversharing traces back to a distribution group that grew and never shrank, which is an identity problem wearing a SharePoint costume.
Before Copilot, permission debt was hidden by obscurity. Finding a salary spreadsheet in a forgotten HR site required knowing it existed. Copilot removes that friction because it searches semantically through the permission-trimmed index and summarizes what it finds. A vendor study cited by one practitioner blog claims 16% of business-critical data is overshared, averaging roughly 802,000 files per organization. Treat that as a vendor figure rather than a benchmark, but the direction matches what administrators report.
Where permission debt hides
- “Everyone except external users” groups attached to sites that were meant for a department.
- Organization-wide sharing links created for a one-time handoff and never expired.
- Large security groups used as site owners or members, so anyone in the group reaches the content.
- Stale Teams and sites with no active owner to review access.
- Inherited folder permissions that quietly override a carefully scoped parent.
Two SharePoint Risks in One Year: The Server in Front and the Permissions Behind
Oversharing is an inside-out problem: authorized users reaching content they should not. SharePoint also faces an outside-in problem, and a complete governance program has to address both.
On the outside-in side, 2026 has been punishing for on-premises SharePoint Server. CISA added CVE-2026-20963, a remote code execution flaw Microsoft fixed in January, to the Known Exploited Vulnerabilities catalog in March. In July, coverage of CISA’s SharePoint hardening warning described three actively exploited flaws, and CISA noted attackers increasingly favor older, unpatched bugs over brand-new zero-days. A Cloud Security Alliance research note tracked CVE-2026-58644, an unauthenticated remote code execution flaw added to KEV on July 16. Another flaw, CVE-2026-45659, could be triggered by a user with only Site Member permissions, which ties the two problems together: broad membership is also broader attack surface.
In August, CVE-2026-55040, an authentication flaw affecting SharePoint Server 2016, 2019, and Subscription Edition, was added to KEV; SharePoint Online was reported as unaffected. You can follow every addition in the CISA Known Exploited Vulnerabilities catalog.
The lesson for planning: patching handles the server, permission hygiene handles the data, and neither substitutes for the other. For a deeper look at prioritization, see our guide to risk-based vulnerability management.
What Microsoft Recommends for Copilot Oversharing
Microsoft’s documented path is consistent across its security guidance and its Copilot architecture and data protection overview: find the exposure, contain it temporarily, fix permissions, label sensitive content, enforce DLP, and monitor. SharePoint Advanced Management is included with Copilot licenses, but note that a Microsoft 365 E5 license alone does not unlock every SAM feature.
| Control | What it does | Best used for |
| Data access governance reports | Surface sites with potentially overshared or sensitive content | Discovery and prioritization |
| Restricted Content Discovery | Removes selected sites from org-wide search and Copilot; permissions unchanged | Temporary containment |
| Restricted access control | Limits site or OneDrive access to a specified group | Locking down flagged sites |
| Site access reviews | Lets site owners clean up access | Permanent permission fixes |
| Purview DSPM for AI | Data risk assessments and oversharing reports | Ongoing posture monitoring |
| Sensitivity labels with encryption | Restrict which files Copilot can process | Protecting the crown jewels |
| Purview DLP for Copilot | Keeps labeled content out of Copilot responses | Enforcement at answer time |
Restricted Content Discovery: A Tourniquet, Not a Cure
Restricted Content Discovery (RCD) is the control most teams reach for first, and for good reason. It flags a site so that users cannot find its content through organization-wide search or Copilot, and Microsoft documents that it does not change existing permissions. Independent write-ups note the block extends to Copilot agents, and that large sites can take more than a week to fully reflect the change.
The trade-off is the one Microsoft itself flags: restricting discovery leaves the underlying access in place, and Copilot cannot help with that content even when it is central to someone’s job. In Microsoft’s own Mechanics walkthrough, the recommendation is to treat RCD as a short-term solution. One practitioner source also reports that new enablement of the older Restricted SharePoint Search was blocked on July 31, 2026; verify that against your tenant’s message center before relying on it, and plan on RCD plus real remediation.
Sensitivity Labels and DLP: Controls That Travel With the Data
Permissions describe who can open a file. Labels describe what the file is. That distinction is what makes Purview sensitivity labels so valuable for Copilot oversharing: a label with encryption can restrict whether Copilot may work with a file at all, and the protection stays attached when the file moves.
Two practical notes. First, when a label applies encryption, a user generally needs both the right to view and the right to extract content for Copilot to use the file, so design usage rights deliberately. Second, standard sensitive-information types will not catch everything that matters to your business. Contracts, pricing models, and M&A drafts need explicit handling, a point echoed in identity-governance guidance on Copilot oversharing that argues for DLP evaluating what Copilot is about to return, not only prompts and files.
Labels also strengthen your backup posture. Encrypted, classified content is easier to place in the right tier of an immutable backup strategy and our backup and recovery services.
Agents Inherit Your Copilot Oversharing Too
Copilot is no longer only a chat box. Agents built in Copilot Studio ground themselves in SharePoint sites, so an agent pointed at an overshared site inherits that site’s exposure. Practitioner guidance recommends least privilege for connectors and actions and a review of every knowledge source. The OWASP GenAI Security Project catalogs the wider class of risks, including excessive agency and sensitive information disclosure.
Agent context has its own liability. If agents write long-lived notes or summaries from overshared content, you have copied the problem into a new place. We covered this in why agents need documentation, not memory, and the identity side in our piece on blind agent transfer. For the broader governance frame, the NIST AI Risk Management Framework maps oversight duties to the people who deploy these tools.
Copilot Oversharing in Financial Services, Healthcare, and Insurance
For regulated firms, Copilot oversharing is a compliance exposure, not just a hygiene issue.
- Financial services: The Federal Reserve’s SR 26-2 revised model risk guidance and the SEC’s Regulation S-P amendments both raise the bar for knowing where customer information flows. New York firms also face the Department of Financial Services’ Part 500 cybersecurity regulation.
- Healthcare: The HIPAA Security Rule requires access controls and minimum-necessary discipline. A Copilot answer that reveals a patient file to an unrelated employee is an impermissible access event regardless of how it happened.
- Insurance and other FTC-covered firms: The FTC Safeguards Rule expects access controls and monitoring for customer information.
All three map neatly to NIST SP 800-53 access control and CSF 2.0 govern and protect outcomes, which is why auditors increasingly ask about AI data exposure alongside traditional access reviews.
The Network Layer: Backing Up Microsoft 365 Controls
Microsoft’s controls operate inside the Microsoft 365 tenant. They are necessary, but a defense-in-depth program assumes some permission will always be wrong. That is where the network layer earns its place, and it aligns with the NIST zero trust architecture principle of never trusting a location or a group by default.
- Segmentation and inspection. The Exodus NxtGen Firewall and Zero Trust Content Security help constrain where SharePoint traffic can go and what content leaves, which matters most for on-premises SharePoint Server estates.
- Detection and response. Exodus Aria ADR and EDR help spot unusual bulk access or lateral movement after a credential is abused.
- Encryption and keys. Exodus Key Management, Data In Motion, Data at Rest, and Transparent Encryption protect content even when it travels or is copied.
- Quantum readiness. Collaboration repositories hold long-lived secrets, which makes them prime targets for the pattern described in Exodus QRN and our analysis of Executive Order 14412.
- Secure connectivity. Branch and remote users reach Microsoft 365 over your WAN, so SD-WAN policy and security as a service belong in the design.
Your Microsoft footprint is also an ibm/SEIMless specialty: see our SharePoint services, Microsoft 365 and Teams, Microsoft Azure, Desktop as a Service, and private and hybrid cloud offerings.
A 30-Day Copilot Oversharing Remediation Plan
Days 1–7: Find it
Run data access governance reports and Purview data risk assessments on your top sites. Rank by sensitivity and by breadth of access, starting with HR, finance, legal, executive, and customer data. Inventory your on-premises SharePoint Server versions against the KEV catalog at the same time.
Days 8–14: Contain it
Apply Restricted Content Discovery to the highest-risk sites and restricted access control where a defined group should have exclusive access. Patch any exposed servers. Keep a written exceptions list so contained sites are not forgotten.
Days 15–24: Fix it
Launch site access reviews so owners remove stale members, “everyone” groups, and old sharing links. Break inheritance mistakes and replace individual grants with security groups. Assign an owner to every site that lacks one, or archive it.
Days 25–30: Protect and monitor it
Publish sensitivity labels for your most sensitive categories, enable DLP for Copilot, and turn on audit review of Copilot interactions. Add network controls and detection so unusual access patterns raise alerts, then repeat quarterly. The NIST National Cybersecurity Center of Excellence publishes practice guides that can anchor the control mapping.
Six Questions to Ask Before You Switch Copilot On
- Which sites contain regulated or board-level data, and who can reach them today?
- Do we have an owner for every site, and when was access last reviewed?
- Which of our on-premises SharePoint servers are on supported, patched builds?
- Is DLP evaluating Copilot responses, or only email and files?
- Can we detect and alert on a user suddenly summarizing hundreds of files?
- Are backups and encryption keys isolated from the same permissions that created the exposure? The Verizon Data Breach Investigations Report, the IBM Cost of a Data Breach study, and the FBI Internet Crime Complaint Center all show how often stolen or misused access is the root cause.
For federal and defense-adjacent teams, the Government Accountability Office and FFIEC regularly publish findings that reinforce the same access-governance themes. If scanned records and faxes still feed your SharePoint libraries, add scanning and retrieval and Fax2Mail to the review, because paper-to-digital pipelines are a common source of unlabeled sensitive content.
Frequently Asked Questions About Copilot Oversharing
What is Copilot oversharing?
It is when Microsoft 365 Copilot surfaces files a user can technically open but was never meant to see. Broad SharePoint access, everyone links, and stale groups become instant answers.
Does Copilot bypass SharePoint permissions?
No. Microsoft states Copilot only surfaces data a user already has access to. The risk is that Copilot makes years of excessive permissions far easier to discover.
What is Restricted Content Discovery?
A SharePoint Advanced Management control that removes selected sites from organization-wide search and Copilot while permissions are reviewed. It does not change permissions, so it is temporary containment.
Do sensitivity labels stop Copilot from using a file?
They can. Purview labels that apply encryption restrict which files Copilot can process, and DLP policies can keep labeled content out of Copilot responses.
Is on-premises SharePoint Server affected by the same problem?
It carries a separate risk: multiple 2026 SharePoint Server vulnerabilities reached the CISA KEV catalog. Permission cleanup and server patching are different jobs, and both are required.
How long does a Copilot oversharing cleanup take?
A focused first pass on the highest-risk sites can take about 30 days, but permission hygiene is ongoing. Access reviews and sharing policies prevent new oversharing from accumulating.
Ready to Make Copilot Safe to Deploy?
ibm/SEIMless helps medium and enterprise organizations pair Microsoft 365 governance with network security, encryption, and quantum-resistant protection. Let us map your permission debt and build a plan that fits your regulators.
Call: 646-546-5245 · Email: in**@**********ss.com
One Liberty Plaza, New York, NY 10006
Explore more: All Services · Blog · AI agent traffic · FBI data breach lessons